2027 Penetration Tester Careers: Skills, Education, Salary & Job Outlook

Co-Founder and Chief Data Scientist
Becoming a penetration tester is a practical career decision, not just a technical ambition. The role asks you to understand how systems are built, how attackers break them, and how organizations can fix weaknesses before real damage occurs. That means the path usually includes a mix of computer science fundamentals, networking, secure coding, ethical hacking practice, documentation skills, and credible proof of ability.
The payoff can be strong for people who commit to that learning curve. Cybersecurity demand continues to support median salaries above $88,000, and penetration testing remains one of the more hands-on, problem-solving-focused paths in the field. This guide explains what penetration testers do, which skills and credentials matter, how salaries and advancement work, and how to decide whether this career fits your strengths and goals.
Key Things You Should Know About Penetration Tester Career
- The typical earning potential for a penetration tester in the United States ranges from $119,895 to $124,127 annually, reflecting strong compensation in cybersecurity.
- This field is highly stable and growing due to a persistent workforce shortage, ensuring solid demand for skilled professionals.
- A bachelor's degree in computer science, cybersecurity, or a related area is usually required, with prior IT or cybersecurity experience providing a valuable edge.
- Success depends on strong technical skills in operating systems, networking, and security frameworks, alongside effective communication and problem-solving abilities.
- Career growth can lead to senior positions such as lead penetration tester or security consultant, or transitions into roles like security architect and information security manager.
What do Penetration Testers do?
Penetration testers, often called ethical hackers, evaluate an organization’s systems by attempting to find and exploit security weaknesses under authorized, controlled conditions. Their goal is not to cause harm. It is to show where harm could happen, how serious the exposure is, and what the organization should fix first.
The work goes beyond running automated vulnerability scanners. A penetration tester may assess networks, web applications, cloud environments, APIs, wireless systems, employee security behaviors, or internal access controls. They combine tools, manual testing, research, and attacker-style thinking to uncover issues that routine monitoring may miss.
A Day in the Life of Penetration Testers
A typical day may include reviewing a test scope, setting up lab environments, running scans, manually validating findings, attempting controlled exploitation, documenting evidence, and meeting with security teams or clients. Some days are highly technical and independent. Others focus on explaining results to managers, developers, auditors, or executives who need clear remediation priorities.
The final deliverable is usually a written report. A strong report does more than list vulnerabilities. It explains business risk, evidence, severity, likely attack paths, and realistic fixes. In many organizations, the report becomes the roadmap for closing security gaps and reducing breach risk.
What are the key responsibilities of Penetration Testers?
Penetration testers are responsible for safely testing security defenses and translating technical findings into action. Their work must be methodical because a poorly planned test can miss serious vulnerabilities, disrupt systems, or create confusion for the teams responsible for remediation.
- Define the test scope, rules of engagement, authorized targets, timelines, and safety limits before testing begins.
- Conduct vulnerability assessments with specialized tools to identify potential security gaps.
- Plan and execute realistic penetration tests against networks, systems, applications, cloud assets, or other approved targets.
- Validate findings manually so reports do not rely only on automated scanner output.
- Collect and analyze test data to identify unauthorized access paths, weak configurations, missing controls, and exploitable vulnerabilities.
- Document findings with enough evidence for technical teams to reproduce and fix the issue.
- Recommend practical improvements, such as stronger authentication, software updates, secure configuration changes, network segmentation, or better monitoring.
- Brief technical and nontechnical stakeholders on risk, impact, and remediation priorities.
The Most Challenging vs. The Most Rewarding Tasks
One of the most challenging tasks is social engineering testing. It requires testers to evaluate human and process weaknesses without crossing ethical boundaries or damaging trust. Good social engineering assessments depend on careful authorization, clear limits, discretion, and empathy as much as technical skill.
The most rewarding work often comes from finding a serious vulnerability before an attacker does. When a tester helps prevent data exposure, account compromise, fraud, or operational disruption, the impact is concrete. That is one reason cybersecurity remains connected to many of the most in demand college majors: organizations need professionals who can protect digital systems that people and businesses depend on every day.
What are the key skills for Penetration Testers?
Successful penetration testers need a combination of technical depth, disciplined judgment, and clear communication. Tools matter, but employers usually look for people who understand why a vulnerability exists, how it can be exploited, what risk it creates, and how to fix it.
Core Technical Hard Skills
- Penetration testing tools: Tools such as Metasploit, Burp Suite, and Nmap help testers discover, validate, and demonstrate vulnerabilities.
- Programming and scripting: Languages such as Python, PowerShell, and Bash are useful for automation, custom testing, parsing results, and building proof-of-concept exploits.
- Operating systems: Testers should understand Windows, Linux, and macOS environments, including permissions, services, logs, file systems, and common misconfigurations.
- Networking: Strong knowledge of protocols, ports, routing, firewalls, DNS, authentication, and segmentation helps testers map attack paths accurately.
- Web application security: Many roles require knowledge of authentication flaws, injection risks, access control issues, session handling, APIs, and secure development concepts.
- Vulnerability assessment and management: Testers must identify, prioritize, validate, and explain security flaws in ways that support remediation.
Essential Soft Skills
- Critical thinking: Penetration testers must interpret incomplete information and think several steps ahead.
- Complex problem solving: Real environments rarely behave like training labs, so testers need persistence and creativity.
- Communication: Clear writing and speaking skills are essential because reports influence security spending, engineering priorities, and compliance decisions.
- Attention to detail: Small configuration errors, overlooked permissions, or subtle application behaviors can create major security weaknesses.
- Professional ethics: Testers work with sensitive systems and data, so trust, discretion, and respect for scope are nonnegotiable.
The One Overlooked Skill That Separates the Good from the Great
Business acumen is often overlooked, but it is one of the skills that makes a penetration tester more valuable. It means understanding how a technical issue affects operations, revenue, legal exposure, customer trust, or regulatory obligations.
For example, a tester may find a vulnerability that appears technical on the surface but could lead to account takeover, payment fraud, or exposure of confidential records. A tester with strong business judgment can explain why the issue matters, who is affected, and why fixing it should be prioritized over lower-risk items.
That combination of technical credibility and business context is especially valuable in sectors such as finance and insurance, where security risk can carry major operational and reputational consequences. For learners still building academic foundations, an easiest master's degree may be worth comparing with certification-focused or experience-focused routes before committing time and tuition.
The path into penetration testing is usually built in stages. Very few people become effective testers by learning tools alone. You need fundamentals first, then practice, then proof that you can work safely in real environments.
- Build your technical base. Study computer systems, networking, operating systems, programming, databases, and basic security principles.
- Practice in legal lab environments. Use capture-the-flag exercises, intentionally vulnerable applications, home labs, and training platforms to learn exploitation safely.
- Gain adjacent IT or cybersecurity experience. Entry-level roles in help desk, system administration, network administration, security operations, or security analysis can build the operational knowledge penetration testers need.
- Earn targeted certifications. Choose credentials that match your current level and the jobs you want, rather than collecting certificates without hands-on skill.
- Create evidence of ability. Keep a portfolio of sanitized reports, lab write-ups, projects, scripts, or bug bounty experience that shows how you think and communicate.
- Apply for junior penetration testing or security assessment roles. Tailor your resume to testing skills, report writing, tools, labs, certifications, and relevant IT experience.
- Keep learning after you are hired. Attack techniques, cloud platforms, application frameworks, and defensive controls change constantly, so ongoing practice is part of the job.
A realistic roadmap turns a broad goal into a sequence of concrete milestones. If you are new to the field, focus first on fundamentals and hands-on practice. If you already work in IT or security, identify the gaps between your current responsibilities and the testing work you want to perform.
Penetration tester roles typically require a bachelor's degree in fields such as Computer Science, Cybersecurity, Information Technology, or Information Assurance. Some colleges also offer specialized bachelor's programs in Cybersecurity with a focus on Penetration Testing. A degree can help with fundamentals, employer screening, internships, and long-term advancement, but hands-on ability remains critical.
Important certifications include the Certified Ethical Hacker (CEH) from EC-Council and the Offensive Security Certified Professional (OSCP) from Offensive Security. Both are valued by employers, though they signal different strengths. CEH is often associated with ethical hacking concepts and terminology, while OSCP is widely known for practical, hands-on testing demands.
On-the-job preparation commonly includes 2-5 years of related IT or cybersecurity experience, often through roles such as network administrator or security analyst. Internships, bug bounty programs, supervised projects, labs, and security competitions can also help demonstrate practical readiness, especially for candidates without a long professional background.
How to Choose the Right Preparation Path
| Path | Best For | Main Trade-Off |
| Bachelor's degree | Students who want broad foundations, internships, and access to employers that prefer degrees | Requires significant time and tuition |
| Certifications | Career changers or IT professionals who need to validate specific security skills | Certifications are strongest when backed by hands-on experience |
| IT or security experience | People building practical knowledge through administration, operations, or analyst roles | The route may take longer if testing duties are not part of the job |
| Labs, bug bounties, and projects | Learners who need portfolio evidence and practical repetition | Self-directed work requires discipline and careful documentation |
Are advanced degrees or niche certifications worth the investment?
Advanced degrees such as a Master of Science in Cybersecurity can help for senior, research, teaching, leadership, or government-focused roles. They may also strengthen your understanding of policy, risk, secure systems, and management. However, they involve tuition, time, and opportunity cost, and most entry-level penetration testing jobs do not require a master's degree.
Specialized certifications such as OSCP and CISSP may offer a faster route to certain roles, especially when paired with proven technical work. Before enrolling in any program, compare employer requirements in your target job postings, your current experience level, your budget, and whether the credential teaches skills you will actually use.
For those aiming at research or academia, options such as PhD programs without a dissertation may be worth reviewing carefully. As with any advanced credential, verify accreditation, admission requirements, program outcomes, and whether the degree aligns with your career goal before investing.
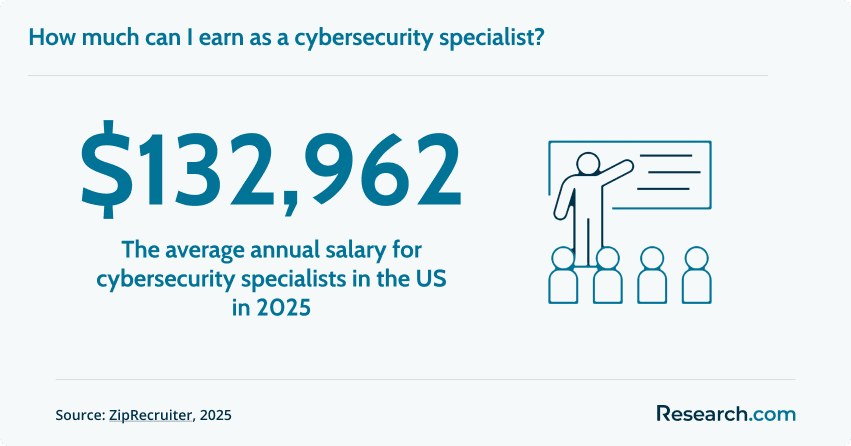
The entry-level penetration tester starting salary is typically around $66,000. That figure gives new candidates a realistic baseline, but actual pay can vary by employer, location, degree requirements, certification expectations, and whether the role is internal security, consulting, government contracting, or a specialized red team position.
The median salary for a penetration tester stands at $101,082 per year. The penetration tester salary range 2025 spans from about $66,000 at entry-level to $150,000 or more for senior roles. This range reflects how much compensation can grow as testers build deeper technical expertise, lead complex engagements, communicate risk effectively, and specialize in high-demand areas.
Several factors can influence where a professional lands within that range. Experience is one of the biggest. Certifications such as OSCP or CEH can also affect competitiveness, especially when employers use them to screen candidates. Industry matters as well: organizations in high-demand sectors such as finance and technology may offer higher pay because the business impact of security failure can be significant. Geographic location and remote-work policies can also shape compensation.
| Career Stage | Typical Salary Context | What Usually Increases Pay |
| Entry-level | Around $66,000 | Strong fundamentals, labs, internships, junior security experience, and early certifications |
| Mid-career | Closer to the median salary of $101,082 per year | Independent testing, strong reports, client communication, and validated technical depth |
| Senior roles | $150,000 or more for some roles | Leadership, specialization, red teaming, cloud security, consulting expertise, and advanced certifications |
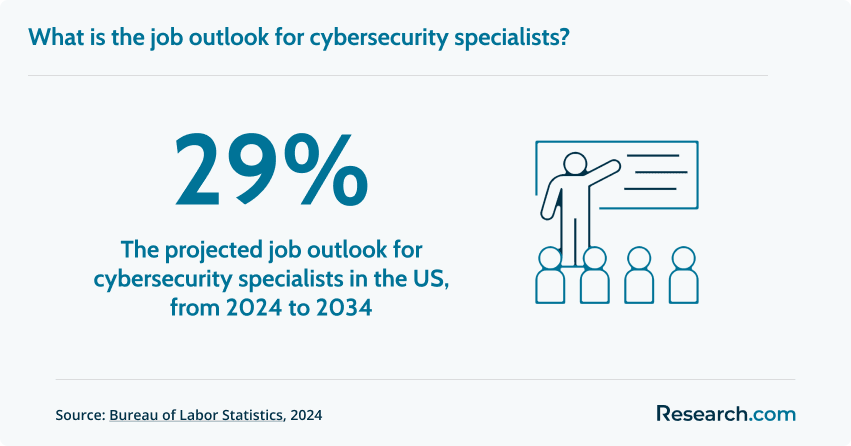
The projected job growth for information security analysts, including penetration testers, is 33 percent between 2023 and 2033. That is much faster than the average growth for all occupations in the U.S. While no career is immune to hiring cycles, the long-term need for security testing remains strong because organizations continue to depend on interconnected systems, cloud platforms, applications, and sensitive data.
The Key Factors Shaping the Future Outlook
The demand for penetration testers is driven by the frequency and sophistication of cybersecurity threats. Organizations need professionals who can think like attackers, test defenses, and help close weaknesses before those weaknesses become incidents. Compliance requirements also support demand because many organizations must demonstrate that they assess and manage security risk on an ongoing basis.
Technology changes are also expanding the role. Cloud computing, IoT devices, APIs, remote work environments, and AI-driven threat simulations create new testing challenges. Penetration testers who can adapt to modern architectures and explain risk clearly will be better positioned than those who rely only on older tools or narrow techniques.
For students and working adults evaluating education options, non profit regionally accredited online colleges can be one place to compare programs that may support cybersecurity preparation. Always review accreditation, curriculum, hands-on lab access, faculty experience, and career support before choosing a program.
The typical work environment for penetration testers includes employer offices, client sites, secure labs, and remote or hybrid setups. Because the work involves sensitive systems and confidential findings, organizations often require controlled access, approved devices, secure communication channels, and strict documentation practices.
Employment is concentrated in industries that depend heavily on digital infrastructure. In this field, 26% work in computer systems design, 19% in finance and insurance, and 10% in information sectors. These environments often require a mix of independent technical work, team coordination, client communication, and formal reporting.
Work-life balance varies by employer and project type. Many penetration testers work mostly standard business hours, but evening or weekend work may be needed when testing could disrupt production systems or when deadlines are tight. Consulting roles can involve more client-facing pressure and shifting timelines, while internal security roles may offer more predictable schedules.
Remote work is increasingly common for assessments that can be performed through secure access, but some projects still require on-site presence. Physical security testing, highly sensitive environments, regulated systems, or client policies may limit remote flexibility.
Penetration testing can be intellectually rewarding, financially promising, and mission-driven. It can also be demanding. The best fit is someone who enjoys solving technical problems, documenting work carefully, learning continuously, and operating within strict ethical boundaries.
Pros
- Meaningful impact: Penetration testers help prevent breaches, data exposure, fraud, and service disruption.
- Challenging work: The role involves complex puzzles, changing environments, and attacker-style problem solving.
- Continuous learning: New systems, vulnerabilities, tools, and defenses keep the career from becoming static.
- Strong advancement potential: Testers can move into senior testing, red teaming, security engineering, consulting, leadership, or specialized research.
- Variety: Different clients, technologies, applications, and environments can keep projects engaging.
Cons
- High learning curve: New testers must build competence across networking, operating systems, applications, scripting, tools, and reporting.
- Pressure and deadlines: Critical tests may involve tight timelines, sensitive systems, and high expectations.
- Heavy documentation: The job is not only exploitation; clear reporting is a major responsibility.
- Repetition: Some engagements reveal similar misconfigurations or common vulnerabilities, especially in less mature environments.
- Constant skill maintenance: Falling behind can limit effectiveness as platforms and attack techniques evolve.
If you want to prepare for this field while balancing work, cost, and flexibility, comparing the best affordable online universities for working adults may help you identify programs that fit your schedule and budget. Be sure to evaluate hands-on cybersecurity coursework, lab access, accreditation, and career services rather than price alone.
Penetration testing offers several advancement routes. Some professionals move upward into senior or lead testing roles. Others specialize deeply in areas such as web applications, cloud security, exploit development, or red teaming. Some transition into security architecture, management, consulting, or governance roles.
Typical Penetration Tester Promotion Path
- Junior Penetration Tester: 0-2 years experience focusing on learning, supervised tests, tool use, documentation, and foundational assessments.
- Penetration Tester: 2-5 years experience handling independent engagements, validating vulnerabilities, communicating with clients or internal teams, and mentoring less experienced testers.
- Senior Penetration Tester/Lead: 5-10 years experience leading complex projects, designing testing methods, reviewing reports, guiding teams, and advising stakeholders on risk.
Specialization Areas to Enhance Growth
- Web Application Security: Focuses on application logic, authentication, APIs, OWASP top vulnerabilities, and tools such as Burp Suite and ZAP.
- Network Security: Involves network protocols, segmentation, architecture, privilege paths, and tools such as Nmap and Wireshark.
- Cloud Security: Centers on cloud identity, misconfigurations, permissions, storage exposure, and secure cloud architecture.
- Red Teaming: Simulates real-world adversaries to test detection, response, and organizational resilience.
- Exploit Development: Focuses on deeper vulnerability research, reverse engineering, and proof-of-concept development.
- Security Leadership: Moves from hands-on testing into program management, risk prioritization, team leadership, or executive advisory work.
Advancement depends on more than technical skill. Senior penetration testers are expected to scope work responsibly, manage client or stakeholder expectations, mentor others, write clear reports, and connect findings to business risk. The professionals who grow fastest usually combine hands-on ability with judgment, communication, and reliability.
If penetration testing interests you but does not perfectly match your strengths, several related cybersecurity careers use similar knowledge in different ways. Comparing these options can help you choose a path based on whether you prefer offense, defense, investigation, engineering, compliance, or leadership.
- Cybersecurity Analyst: Monitors systems, investigates alerts, assesses threats, and supports day-to-day defense operations.
- Incident Response Analyst: Responds to security incidents, investigates breaches, contains threats, and helps organizations recover.
- Security Engineer: Designs, implements, and improves security controls across systems, networks, applications, and cloud environments.
- IT Auditor: Evaluates IT controls, risk management processes, policies, and compliance with internal or external requirements.
- Digital Forensic Examiner: Analyzes compromised systems, recovers evidence, traces attack activity, and supports investigations.
- Security Consultant: Advises clients on risk, security strategy, compliance, architecture, testing, and remediation planning.
Choose penetration testing if you enjoy authorized attack simulation, technical discovery, and report-driven remediation. Consider defensive operations if you prefer monitoring and response, engineering if you like building controls, and auditing if you are drawn to governance and compliance. The best career path is the one that matches your technical interests, tolerance for pressure, communication style, and long-term goals.
Here's What Professionals Say About Their Penetration Tester Careers
- Naomi: "The responsibility I carry every day as a penetration tester is immense-I'm constantly aware that the vulnerabilities I uncover could be exploited by cybercriminals to harm millions. My favorite part is thinking like an attacker, tracing their possible moves through complex systems to find those hidden weak spots. Knowing that my efforts help protect sensitive information and maintain trust for clients fuels my commitment. This role reminds me that behind every line of code, real people's data and security depend on the work I do."
- Lucas: "When I first dove into penetration testing, the volume of knowledge felt overwhelming, especially with all the frameworks, tools, and attack vectors I had to learn. I remember countless nights struggling with my first Capture The Flag challenges, feeling stuck and frustrated. But I made a habit of breaking down complex concepts, building detailed notes, and methodically practicing, which gradually boosted my confidence and skill set. That persistence paid off as I saw steady progress and started tackling tougher scenarios with less hesitation."
- Amina: "After finally landing my first penetration tester role, the rush of accomplishment was incredible, but so were the moments of self-doubt that followed. I had worked nonstop for over two years, constantly studying and practicing to get to that point. The biggest reward came from realizing that my knowledge and skills were valued, and that I could truly help secure systems against attackers. Support from more experienced colleagues made a huge difference, reminding me that even professionals struggle but can grow beyond it."
Other Things You Should Know About Penetration Tester
In 2027, beneficial certifications for penetration testers include Certified Ethical Hacker (CEH), Offensive Security Certified Professional (OSCP), and Certified Information Systems Security Professional (CISSP). These certifications validate key skills required for successful penetration testing and enhance career prospects.
In 2027, the employment outlook for penetration testers remains robust, with increasing demand as cybersecurity threats grow. Organizations are prioritizing safeguarding sensitive information, driving a need for skilled professionals. Job growth is expected as cybersecurity continues to be a critical area for investment.
Most penetration testers work 40-hour weeks in full-time roles, with longer hours during client assessments, incident-response support, or deadline-driven engagements. Consulting teams may also travel to client sites for several days at a time, especially during large network or web application tests.
- How to Become a Penetration Tester | Cyber Degrees https://www.cyberdegrees.org/careers/penetration-tester/how-to-become/
- Associate Penetration Tester Position at Schellman and What To Expect | Schellman https://www.schellman.com/blog/careers/associate-penetration-tester-position-what-to-expect
- Gaining a Foothold: Transitioning into a Penetration Testing Career https://www.optiv.com/insights/discover/blog/gaining-foothold-transitioning-penetration-testing-career
- A Day in the Life of a Penetration Tester https://www.careersinaudit.com/careers/2021/05/a-day-in-the-life-of-a-penetration-tester/
- How to become a penetration tester in 2025: (Practical) career guide https://www.hackthebox.com/blog/how-to-become-a-pentester
- How Much Can You Make As A Penetration Tester in 2025? https://www.hackingloops.com/how-much-penetration-testers-make/
- I love my job: pen testers are like the rock stars of IT! - Jisc https://www.jisc.ac.uk/blog/i-love-my-job-pen-testers-are-like-the-rock-stars-of-it
- Penetration Tester – Why their role is essential in cybersecurity https://testarmy.com/blog/penetration-tester-why-their-role-is-essential-in-cybersecurity
- Spotterful | Main Responsibilities and Required Skills for Penetration Tester https://spotterful.com/en/blog/job-description-template/penetration-tester-responsibilities-and-required-skills
- Advantages and Disadvantages of Penetration Testing in Cybersecurity [UPDATED 2025] https://cybersapiens.com.au/advantages-and-disadvantages-of-penetration-testing-in-cybersecurity/