2027 Role-Based Access in Health Information Systems

Co-Founder and Chief Data Scientist
A nurse needs a patient's chart to provide care; a billing specialist needs different information to submit a claim. Giving both unrestricted access creates avoidable privacy and security risks. Role-based access helps health information systems match permissions to job responsibilities without obstructing legitimate care.
This guide explains how those permissions work, where they can fail, and what education prepares people to design or oversee them. It also helps prospective students distinguish technical health information roles from healthcare management careers before choosing a degree.
Key Things You Should Know
- Role-based access assigns system permissions to defined job roles, then assigns people to those roles; it requires regular review because job titles alone cannot capture every clinical need.
- HIPAA requires access controls and workforce access management for covered systems but does not require every organization to use a particular role-based access design.
- For career planning, health information management or informatics study generally provides more direct preparation for access governance than a general MBA; the right credential depends on whether you want to configure systems or lead teams.
What Is Role-Based Access in Health Information Systems?
Role-based access control (RBAC) is a method for deciding what a person can do in an electronic health record (EHR) or other health information system. An organization defines roles such as treating clinician, scheduler, or billing specialist; attaches permissions to each role; and assigns staff to the appropriate roles. Permissions can distinguish viewing a record from editing it, ordering a medication, or exporting data.
RBAC is not simply a list of job titles. A nurse who also covers a specialty clinic may need a carefully approved combination of roles. Conversely, a manager's seniority does not automatically justify access to every patient record.
Understanding who designs those permissions can help readers distinguish healthcare leadership education compared with health information management: administrators may set policy and accountability, while information-system specialists translate those decisions into configured access.
Why Is Role-Based Access Important in Healthcare?
Healthcare organizations need to make information available quickly while limiting unnecessary access. RBAC gives them a repeatable starting point: staff with the same approved duties receive consistent baseline permissions. That can reduce accidental exposure and make onboarding, transfers, and access reviews easier to manage.
Its value depends on governance, not just software. Clinical leaders must identify what staff need to do their jobs; privacy and security teams must examine inappropriate access; and system administrators must test whether permissions behave as intended.
For readers interested in overseeing those decisions, healthcare administration employment paths and advancement offer a different career direction from hands-on EHR access administration.
How Does Role-Based Access Protect Patient Health Information?
RBAC limits ordinary access to approved functions, but it is only one layer of protection. A practical design connects permissions to verified identities, records access in audit logs, reviews role assignments when duties change, and provides a controlled way to handle emergencies. An emergency "break-glass" function may permit access outside a normal role while requiring a reason and generating an audit trail; its safeguards depend on the organization's implementation.
The HIPAA Security Rule requires covered entities and business associates to implement access controls and manage workforce access to electronic protected health information. It does not prescribe RBAC as the sole acceptable architecture. Nor should the HIPAA Privacy Rule's minimum-necessary standard be used to deny information needed for treatment: that standard generally does not apply to disclosures to, or requests by, healthcare providers for treatment. Organizations still need appropriate authorization and security controls.
Overly restrictive roles can delay care, while overly broad roles weaken privacy. Leaders evaluating advanced governance education can explore evaluating faster healthcare leadership doctorate pathways, but a leadership doctorate is not a substitute for learning how access rules are configured and tested.
Start with the work you want to perform. Access analysts and EHR administrators need familiarity with clinical workflows, identity and access management, privacy rules, and system testing. Health information managers may supervise records processes and data governance. Healthcare administrators more often lead budgets, staffing, compliance coordination, and organizational change.
An associate or bachelor's degree can support entry into some health information positions; specialized graduate study can help experienced professionals move into informatics or management. Employers may also value EHR experience, clinical experience, or demonstrated security work. A degree alone does not grant access to a hospital's systems or qualify someone to configure a particular vendor's software.
If the goal is healthcare operations leadership rather than technical permissions work, healthcare administration graduate study within a one-year format may be worth comparing. Verify the actual schedule and prerequisites: faster completion does not necessarily mean lighter coursework.
These degree categories overlap, but they prepare students for different decisions. The comparison below focuses on curriculum fit rather than assuming a degree title guarantees a particular job:
| Degree path | Typical emphasis | Best fit for RBAC-related goals |
| Health information management | Health records, data governance, privacy, and information workflows | Managing information practices and coordinating access policy |
| Health informatics or health information systems | Clinical systems, data, workflows, and technology implementation | Analyzing or improving EHR access design |
| Cybersecurity or information systems | Identity management, system security, and technical controls | Engineering or administering access controls, with healthcare-specific training |
| Master of Health Administration (MHA) or healthcare-focused MBA | Organizational leadership, finance, operations, and strategy | Overseeing teams and governance rather than configuring permissions |
An MBA provides a broad management core; a healthcare concentration, when formally offered, adds selected industry coursework. An MHA is more specifically oriented toward healthcare administration. Neither is automatically equivalent to technical informatics training. Readers aiming for executive operations roles can examine online Master of Health Administration programs alongside informatics degrees before committing to a path.
Look for assignments that require students to map a clinical workflow to permissions, identify conflicting duties, document an emergency-access process, or interpret audit findings. Management-focused programs may instead address risk, budgeting, and change management. If an MBA is under consideration, compare accelerated healthcare-focused MBA degrees by their actual courses and projects, not just completion time; an accelerated management curriculum may leave substantial technical training to be gained elsewhere.
Online programs can be accredited, but accreditation must be checked at the right level. Institutional accreditation applies to the college or university. Specialized accreditation, where available, evaluates a particular program or field; it is not interchangeable with institutional accreditation.
For example, CAHIIM accredits eligible health information management and health informatics programs, while CAHME accredits eligible healthcare management graduate programs. An online MHA's CAHME status does not establish that its students receive technical RBAC training. Readers comparing CAHME-accredited online healthcare administration study should confirm that the specific program and delivery option are covered and then inspect the curriculum for information-governance content.
Certifications can signal focused knowledge, but they serve different purposes. AHIMA's RHIA and RHIT credentials relate to health information practice and have specific eligibility rules. Privacy and security credentials may support governance or technical security roles. An EHR vendor's training may be especially relevant to configuring its product, though access to that training and employer expectations vary.
Choose a credential after reviewing job postings for your target role, then verify eligibility, exam content, renewal obligations, and employer recognition with the issuing organization. A certification is not interchangeable with a degree or practical system experience. If you are deciding between targeted training and review accelerated online healthcare management degrees, the shorter credential may be more direct for an existing employee with a specific access-governance skill gap; a degree may better suit a broader management transition.
Potential paths include EHR access analyst, identity and access management analyst, health information manager, privacy officer, informatics specialist, and healthcare operations manager. Titles are not standardized: an "analyst" might configure roles at one employer and only process approved access requests at another. Review the duties and required experience before treating two postings as equivalent.
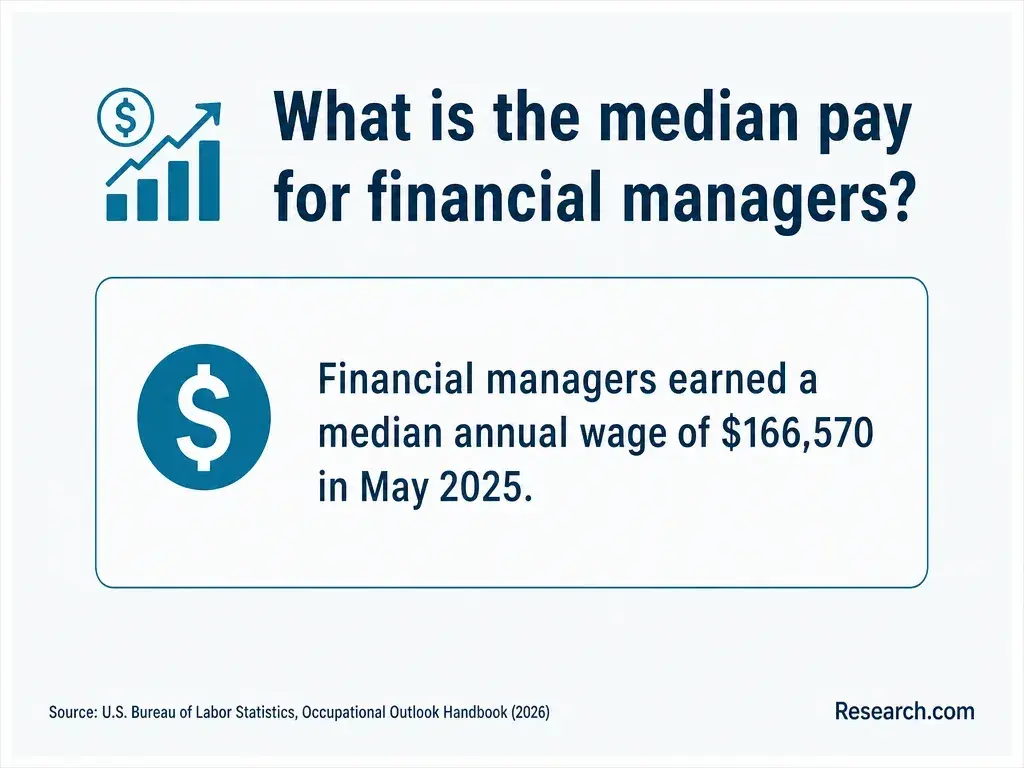
The U.S. Bureau of Labor Statistics reports that the median annual wage across management occupations was $126,520 in May 2025. That broad figure is not the pay of an EHR access analyst, a healthcare administrator specifically, or a new graduate. BLS also projects about 1.1 million openings annually across management occupations from 2025 to 2035; it should not be read as a forecast for health information systems jobs alone.
For advancement into senior governance or executive roles, weigh experience and employer requirements before paying for another degree. Someone considering a doctorate should treat budgeting for an online healthcare administration doctorate as a separate decision, not as a routine requirement for RBAC or informatics work.
How Do You Choose a Reputable Health Information Systems Program?
Choose backward from a realistic target role. A program is a stronger fit when its coursework, applied work, and career support address the tasks employers actually assign—not merely when its marketing mentions healthcare technology. Use the following checks to narrow your options before applying:
- Compare target job postings with required courses, especially EHR workflows, privacy, identity management, and hands-on projects.
- Verify institutional accreditation and any claimed programmatic accreditation with the relevant accreditor; ask whether it covers the online option.
- Request the full tuition and mandatory-fee schedule, plus information about software, required visits, and employer reimbursement.
- Ask whether classes have live meetings, group projects, practicums, or vendor-platform access, and confirm how those requirements fit your work schedule.
- Ask career services which employers recruit online students and whether outcomes are reported for this specific program rather than the institution overall.
Cost comparisons should use the full program expense, not a tuition headline. If leadership rather than technical access work is your goal, low-cost healthcare administration master's degrees can provide comparison points. The least expensive option is not necessarily the best value if it lacks the courses or practical experience your intended role requires.
Other Things You Should Know About Healthcare Administration
Patients can ask their provider about record-access concerns, but HIPAA does not generally require an organization to give patients a complete log of every workforce member who viewed a chart. Rights to an accounting of disclosures are different from access to an internal audit log.
Organizations should promptly remove access that is no longer authorized. Their procedures should account for departures, transfers, contractors, and shared responsibilities; a fixed deadline cannot replace checking the applicable policy and facts.
No. Access controls should reflect the practice's size, systems, and workforce. A small team may have broader duties, but it still needs a defensible way to authorize, review, and end access.
Approval should follow the organization's documented process, usually involving a manager or designated role owner who can confirm job duties. IT can implement the approved access, but should not have to guess what clinical or administrative information the employee needs.
- Using electronic health record audit logs to study clinical activity | nih.gov https://pmc.ncbi.nlm.nih.gov/articles/PMC7025338/
- Summary of the HIPAA Security Rule | hhs.gov https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html
- Separation of Duties and Least Privilege (Part 15 of 20 | SEI Blog https://www.sei.cmu.edu/blog/separation-of-duties-and-least-privilege-part-15-of-20-cert-best-practices-to-mitigate-insider-threats-series/
- Health Information Manager - Explore Healthcare Careers | Mayo Clinic College of Medicine and Science https://college.mayo.edu/academics/explore-health-care-careers/careers-a-z/health-information-manager/
- Access control solutions in electronic health record systems | sciencedirect.com https://www.sciencedirect.com/science/article/pii/S2352914824001084
- What are Separation of Duties and Least Privilege? | OpenText Blogs https://blogs.opentext.com/separation-of-duties-and-least-privilege/
- What Is the Principle of Least Privilege? | Palo Alto Networks https://www.paloaltonetworks.com/cyberpedia/what-is-the-principle-of-least-privilege
- How Role-Based Controls Protect Patient Data | Censinet https://censinet.com/perspectives/how-role-based-controls-protect-patient-data
- Least Privilege Access (Healthcare): A Simple Guide | getsolum.com https://getsolum.com/glossary/least-privilege-access-healthcare
- Health Information 101 | AHIMA https://www.ahima.org/certification-careers/certifications-overview/career-tools/career-pages/health-information-101/