2027 What Does a Privacy Officer Do: Responsibilities, Requirements, and Salary

Co-Founder and Chief Data Scientist
Becoming a privacy officer is a career decision for people who want to work where law, technology, cybersecurity, risk management, and business strategy meet. The role is no longer limited to writing policies or checking compliance boxes. Privacy officers now help organizations decide how personal data can be collected, stored, shared, analyzed, protected, deleted, and used in emerging areas such as artificial intelligence.
This guide explains what privacy officers do, the skills and education employers typically look for, which certifications can strengthen your profile, how salaries and advancement work, and what laws, challenges, and trends are reshaping the field. It is written for students, compliance professionals, IT and cybersecurity workers, legal staff, and career changers who want a realistic view of the privacy officer career path.
The demand for privacy expertise is being shaped by remote work, cloud services, AI governance, cross-border data transfers, stricter privacy laws, and rising public expectations around data protection. Over 80% of privacy teams now handle AI/data governance tasks, which means future privacy officers will need to combine regulatory knowledge with practical technology and business judgment.
Key Things You Should Know About What a Privacy Officer Does
- The demand for privacy professionals continues to surge, driven by the expansion of U.S. and global data protection laws. Privacy officers earn competitive salaries, with even higher compensation for those in regulated industries such as finance and healthcare.
- Privacy officers play a crucial role in shaping ethical data use, compliance frameworks, and public trust. They increasingly sit at the intersection of law, technology, and corporate governance—often influencing executive decisions and organizational risk strategy.
- As artificial intelligence and data analytics reshape privacy challenges, professionals in this field gain cutting-edge expertise in emerging regulations, cybersecurity, and AI governance—skills that are in high demand across sectors and resilient to automation.
What does a privacy officer do on a daily basis?
A privacy officer manages how an organization protects personal information and complies with privacy obligations. On a typical day, the work may include reviewing business processes, advising teams on data use, documenting compliance activities, assessing risks, handling privacy requests, supporting vendor reviews, and coordinating responses to data incidents.
The role is highly cross-functional. A privacy officer may work with legal teams on regulatory interpretation, IT and cybersecurity teams on technical safeguards, HR on employee data, marketing on consent and tracking practices, procurement on vendor contracts, and executives on privacy risk.
Common daily responsibilities
- Reviewing data-processing activities: Privacy officers examine how personal information is collected, used, stored, transferred, and deleted. They check whether the activity aligns with applicable laws, internal policies, and business purposes.
- Assessing new projects: They determine whether a new product, system, vendor, or data initiative requires a privacy impact assessment or additional safeguards before launch.
- Maintaining privacy policies and records: This can include updating privacy notices, data retention rules, access controls, data maps, consent processes, and records of processing activities.
- Advising internal teams: A major part of the job is translating privacy requirements into practical guidance for employees who are not privacy specialists.
- Managing data-subject and regulator inquiries: Privacy officers may help respond to access, deletion, correction, opt-out, or complaint requests, depending on the laws that apply.
- Supporting vendor oversight: They review how third parties handle personal data and help ensure contracts include appropriate privacy and security terms.
- Coordinating incident response: If a breach or privacy incident occurs, the privacy officer helps investigate the scope, document findings, determine notification obligations, and recommend corrective action.
The work is both preventive and reactive. Strong privacy officers reduce risk before problems occur, but they also need the judgment and discipline to act quickly when a complaint, audit, breach, or regulatory deadline arises.
What skills are required to become a successful privacy officer?
A successful privacy officer needs more than legal knowledge. The job requires the ability to understand regulations, evaluate technology, manage risk, influence people, and build repeatable processes that employees can actually follow.
- Legal and regulatory knowledge: Privacy officers need a working understanding of major data protection frameworks such as the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA). They do not always need to be attorneys, but they must know when legal interpretation is needed and how privacy rules affect day-to-day operations.
- Risk assessment and management: The role requires identifying privacy risks in systems, vendors, business processes, employee practices, marketing tools, and data-sharing arrangements. Strong privacy officers can prioritize the highest-risk issues instead of treating every concern as equally urgent.
- Technical fluency: Privacy officers should understand how data moves through systems, how access controls work, what encryption does and does not solve, how cloud services process information, and how privacy-by-design principles apply to product development. They do not need to code, but they must be able to hold informed conversations with IT, security, engineering, and data teams.
- Communication skills: Privacy rules can be complex, but employees need clear instructions. A good privacy officer can brief executives, train staff, negotiate with vendors, and explain risks without overusing legal jargon.
- Policy and process design: Privacy programs depend on repeatable workflows. This includes procedures for data requests, breach escalation, vendor reviews, retention schedules, privacy assessments, and employee training.
- Attention to detail: Small errors in consent language, data inventories, contracts, retention periods, or notification timelines can create major compliance exposure. Accuracy matters.
- Business judgment: Privacy officers often balance compliance, customer trust, operational needs, and product goals. The best professionals do not simply say “no”; they help teams find lawful, lower-risk ways to achieve legitimate business objectives.
- Adaptability: Privacy law, AI governance, cybersecurity risks, and enforcement priorities change quickly. Continuous learning is part of the job, not an optional extra.
If you are comparing privacy with cybersecurity roles, this guide on whether cybersecurity requires coding can help clarify the technical expectations in a related field.
What education is required to become a privacy officer?
Most employers look for at least a bachelor’s degree in a field connected to law, information technology, cybersecurity, business administration, information governance, public policy, or compliance. The best major depends on the type of privacy role you want. A privacy officer in healthcare may benefit from health information or compliance training, while a technology company may value cybersecurity, information systems, or data governance experience.
Advanced education can be useful for senior roles, especially when the position requires legal analysis, executive advising, cybersecurity oversight, or global privacy program design. A master’s degree in data privacy, cybersecurity law, information management, public administration, or a related area may strengthen a candidate’s profile, but it is not the only route into the profession.
How to choose the right educational path
- If you are starting college: Choose a degree that builds both analytical and practical skills. Courses in privacy law, cybersecurity, database systems, ethics, compliance, risk management, and business operations are especially relevant.
- If you already work in IT or cybersecurity: Add privacy law, governance, and compliance training so you can connect technical controls to legal obligations.
- If you come from law or compliance: Build enough technical literacy to understand data flows, system architecture, vendor platforms, and security safeguards.
- If you are changing careers: Consider a combination of targeted coursework, entry-level compliance or privacy experience, and professional certification rather than assuming you need another full degree immediately.
Professional certifications, especially those from the International Association of Privacy Professionals (IAPP), are often used to demonstrate job-ready privacy knowledge. They usually work best as a supplement to education and experience, not as a complete replacement for both.
For readers exploring technical education options, these shortest cloud engineering online bootcamps may be useful for understanding cloud-focused training paths.
What is the typical career path to becoming a privacy officer?
The path to becoming a privacy officer usually starts in a related function such as compliance, legal operations, IT, cybersecurity, risk management, records management, audit, human resources, or data governance. Few people begin as full privacy officers immediately; most build credibility by handling privacy-adjacent responsibilities first.
Entry-level stage
Common starting roles include privacy analyst, compliance coordinator, legal assistant, IT security analyst, risk associate, records analyst, or vendor management specialist. At this stage, the goal is to learn how data is handled inside an organization and how privacy rules translate into real processes.
Useful early experience includes helping with data inventories, reviewing policies, tracking regulatory requirements, supporting employee training, documenting vendor reviews, and learning frameworks such as General Data Protection Regulation (GDPR) or California Consumer Privacy Act (CCPA).
Mid-career stage
Professionals often move into roles such as privacy manager, data protection specialist, compliance lead, information governance manager, or privacy program manager. These jobs involve more ownership: conducting data protection impact assessments (DPIAs), reviewing vendor privacy terms, managing privacy requests, coordinating audits, and advising business units.
This is also the stage where certifications such as Certified Information Privacy Professional (CIPP) or Certified Information Privacy Manager (CIPM) can be especially helpful. They show employers that the candidate understands privacy obligations and can apply them in a structured program.
Privacy officer stage
A privacy officer typically owns or leads the organization’s privacy program. The role may involve setting strategy, reporting to senior leadership, advising on cross-border data transfers, overseeing privacy training, monitoring legal developments, and ensuring that privacy risk is considered in product, vendor, marketing, HR, and technology decisions.
To reach this level, professionals need more than subject-matter knowledge. They must show sound judgment, leadership, documentation discipline, stakeholder management, and the ability to connect privacy risk to business decisions.
If you are also considering adjacent digital careers, review these best UX design courses online options for comparison.
The most valuable certifications depend on whether your target role is legal/compliance-focused, program-management-focused, or technology-focused. Certifications can improve credibility, but they should support a broader profile that includes practical experience, communication skills, and understanding of the organization’s data environment.
- Certified Information Privacy Professional – U.S.: Offered by the International Association of Privacy Professionals (IAPP), this credential focuses on U.S. privacy laws, regulatory concepts, and the privacy operating environment. It is useful for candidates who work with U.S. compliance obligations.
- Certified Information Privacy Manager: Also offered by the IAPP, this credential emphasizes privacy program governance, risk management, operational controls, and communication. It is especially relevant for professionals who want to lead privacy programs or manage privacy teams.
- Certified Information Privacy Technologist: This certification is designed for professionals working at the intersection of privacy and technology. It is useful for people involved in product design, engineering, IT, security, data architecture, or privacy-by-design work.
- Certified Data Privacy Solutions Engineer: Offered by ISACA, the CDPSE is geared toward professionals who implement privacy solutions and support the technical architecture of privacy programs. It can be valuable for candidates with IT, security, engineering, or systems backgrounds.
- Certified Information Systems Security Professional: The CISSP is broader than privacy, but it is widely recognized in cybersecurity. It can strengthen a privacy officer’s understanding of security governance, risk management, access control, and incident response. For training options, see these accelerated CISSP certification training online programs.
For many privacy officer candidates, a practical certification sequence is to start with a privacy-law or privacy-program credential, then add a technology or security credential if the target role requires deeper technical work.
Privacy officer compensation is generally strong because the role sits at the intersection of compliance risk, data governance, cybersecurity, legal exposure, and executive decision-making. According to one major salary aggregator, the median base salary for a privacy officer in the U.S. is approximately $140,048 per year, with a typical range from about $128,014 to $147,836, as of July 1, 2025.
Actual pay can differ significantly based on role scope. A privacy officer who leads an enterprise-wide global program, reports to senior executives, manages regulatory risk, and advises on AI or cross-border data transfers will usually command more than a privacy professional in a smaller organization with narrower responsibilities.
Factors that affect privacy officer salary
- Experience level: Senior professionals with a record of building privacy programs, managing audits, and advising leadership usually earn more.
- Industry: Highly regulated sectors such as healthcare, finance, technology, insurance, and data-intensive businesses may offer higher compensation for privacy expertise.
- Company size and risk profile: Larger organizations often need more sophisticated privacy programs, especially if they operate across jurisdictions.
- Geographic location: Pay often reflects local labor markets and cost of living.
- Technical depth: Privacy officers who understand cybersecurity, cloud platforms, AI governance, and data architecture may qualify for more complex roles.
- Leadership responsibility: Managing a team, reporting to the board, or owning enterprise risk can increase compensation.
Privacy is not the only path into well-paid technology work. Some professionals also explore the highest-paying tech jobs without a degree when comparing career options.
Moving from privacy officer to chief privacy officer (CPO) requires a shift from managing privacy tasks to leading privacy as an enterprise strategy. A CPO is expected to advise executives, influence business priorities, oversee risk governance, and help the organization use data responsibly while maintaining trust.
- Build strategic leadership skills: A future CPO must show that privacy can support business goals, not only prevent violations. This includes setting a privacy roadmap, aligning resources, and measuring program effectiveness.
- Expand executive visibility: Aspiring CPOs need credibility with senior leaders such as the CEO, CIO, CISO, general counsel, and business unit heads. The ability to explain privacy risk in financial, operational, and reputational terms is essential.
- Develop broad privacy and data experience: Most CPOs have over 10 years of experience across privacy, compliance, data protection, cybersecurity, legal risk, or governance. Breadth matters because CPO decisions often affect many parts of the organization.
- Strengthen credentials and specialization: Certifications such as CIPP, CIPM, or CDPSE can help validate expertise, especially when combined with a record of leading programs, managing incidents, and working across jurisdictions.
- Move from compliance partner to strategic advisor: CPOs help organizations make better data decisions. That means advising on AI, analytics, product design, customer trust, vendor risk, regulatory exposure, and data ethics.
- Lead culture change: Privacy maturity depends on employee behavior. A CPO must build training, accountability, escalation paths, and incentives that make responsible data handling part of normal operations.
- Stay current and visible in the field: Privacy leaders need to monitor laws such as GDPR and CCPA, track enforcement trends, understand emerging technologies, and participate in professional communities.
The strongest candidates for CPO roles can speak fluently to three audiences: legal teams that need defensible compliance, technical teams that need practical controls, and executives who need risk-based business guidance.
The outlook for privacy officer roles is favorable, but candidates should understand how the occupation is classified. Formal government projections for the exact title “privacy officer” are limited because these jobs may be grouped under compliance, legal, information security, risk management, or management roles.
The broader demand drivers are strong. Organizations continue to face expanding privacy laws, higher expectations from customers and regulators, more complex vendor ecosystems, AI governance concerns, cross-border data-transfer issues, and frequent data security incidents. These pressures increase the need for professionals who can build and manage privacy programs.
For a broader benchmark, the U.S. Bureau of Labor Statistics reports that compliance officers in general are projected to grow around 3 % from 2024-2034, which is about as fast as average for all occupations. Privacy officer roles may perform differently from that broad category because they often combine compliance, cybersecurity, legal risk, data governance, and technology oversight.
Candidates can improve their job prospects by developing a clear specialization. Strong options include healthcare privacy, financial services privacy, AI governance, cybersecurity and privacy operations, global privacy compliance, vendor risk, or privacy engineering. Employers are more likely to value candidates who can solve specific privacy problems rather than those who only claim general interest in the field.
The number of distributed denial-of-service (DDoS) attacks grew in 2024, with the following industries most commonly hit:
Privacy officers face pressure from several directions at once: more regulation, more data collection, more automation, more vendor dependence, and higher expectations from regulators, customers, employees, and executives. The work is becoming more strategic, but also more operationally demanding.
Rapidly evolving regulation and fragmented compliance requirements
Privacy laws are expanding across states and countries, but they do not all use the same definitions, rights, exemptions, consent rules, or enforcement models. This creates a patchwork of obligations that can be difficult to manage with a single policy or workflow.
The practical challenge is consistency. Privacy officers must design programs flexible enough to meet different legal requirements while still being understandable to employees and scalable across the organization.
Integration of emerging technologies and data-use complexities
Artificial intelligence, machine learning, large-scale analytics, connected devices, and behavioral tracking create privacy questions that traditional policies may not fully address. Risks can include algorithmic bias, black-box decision-making, inference risks, excessive data collection, and re-identification through data aggregation.
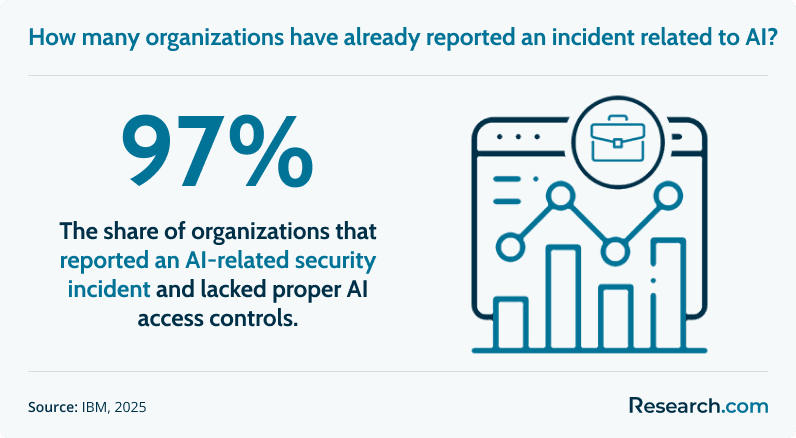
Privacy officers increasingly need to participate earlier in technology decisions. Waiting until a tool is already purchased or a model is already deployed makes privacy review harder and more expensive.
Escalating threat landscape and operational maturity gaps
Data breaches, third-party failures, and vendor supply-chain weaknesses make privacy work closely connected to cybersecurity and incident response. Privacy officers must know how incidents are escalated, who makes notification decisions, what evidence must be preserved, and how lessons learned are converted into stronger controls.
Many organizations also struggle with incomplete data inventories, unclear ownership, inconsistent training, weak retention practices, and limited visibility into where personal information resides. Without operational maturity, privacy programs become reactive instead of preventive.
Balancing business innovation with responsible data use
Business teams often want to move quickly with personalization, analytics, automation, and AI. Privacy officers must help evaluate whether the proposed data use is lawful, necessary, transparent, secure, and aligned with customer expectations. The strongest privacy leaders help teams innovate within clear guardrails rather than blocking every new idea.
Several trends are reshaping privacy officer jobs and expanding the skills required to succeed. The role is moving from a narrow compliance function to a broader data governance and trust function.
AI governance will become a core privacy responsibility
The integration of AI, machine learning, and advanced analytics into business processes means privacy officers must evaluate how data is used to train, test, deploy, and monitor automated systems. More than 80% of privacy teams now handle AI and data governance responsibilities, showing how quickly the role is expanding.
This does not mean every privacy officer must become an AI engineer. It does mean they need to understand data minimization, consent, transparency, bias risks, model outputs, automated decision-making, and governance controls. Professionals interested in this intersection may also want to explore how privacy skills relate to artificial intelligence salary opportunities.
Regulation and enforcement will remain major drivers
Privacy officers will continue to manage complex compliance ecosystems as U.S. state laws, global privacy frameworks, and enforcement activity evolve. Cross-border data flows, vendor oversight, sensitive data, consumer rights, employee monitoring, and children’s data will remain important areas of risk.
Privacy will be tied more closely to cybersecurity
Privacy and security are not the same, but they are increasingly connected. A privacy program depends on access controls, data classification, retention practices, encryption, monitoring, incident response, and vendor security. Privacy officers who can work effectively with CISOs and security teams will be better positioned for senior roles.
Privacy-by-design will matter more
Organizations are under pressure to consider privacy earlier in product design, procurement, analytics, and data architecture. This trend favors privacy officers who can create practical review processes and help teams build compliant systems from the start.
The role will become more strategic
Privacy is increasingly viewed as part of customer trust, brand reputation, and responsible innovation. Future privacy officers will need stronger leadership, communication, ethics, and business skills. The job will be less about saying “follow the rule” and more about helping organizations make defensible decisions about data use.
- : "Becoming a privacy officer put me at the intersection of law, technology, and ethics. I like that the work is practical: teams come to me with real business questions, and I help them protect sensitive data while staying compliant. — Niki"
- : "The role opened doors I did not expect. One day I may be reviewing a vendor risk issue, and the next I may be advising on a new data initiative. The variety keeps the work challenging and meaningful. — Amira"
- : "What I enjoy most is knowing the work matters. Safeguarding people’s information and helping build a culture of trust across the organization gives me pride in my career. — Mei"
Key Findings
- Privacy officers oversee how organizations collect, use, protect, share, retain, and delete personal data.
- The role combines legal knowledge, technology fluency, risk management, communication, and business judgment.
- Most employers expect at least a bachelor’s degree in a related field, while certifications can strengthen credibility for privacy, compliance, technology, or leadership roles.
- Common career paths start in compliance, IT, cybersecurity, legal operations, risk management, information governance, or data protection roles.
- Valuable certifications include CIPP, CIPM, CIPT, CDPSE, and CISSP, depending on the candidate’s target role and background.
- According to one major salary aggregator, the median base salary for a privacy officer in the U.S. is approximately $140,048 per year, with a typical range from about $128,014 to $147,836, as of July 1, 2025.
- Advancing to a CPO role requires strategic leadership, executive influence, broad privacy experience, and the ability to connect privacy to business value.
- Formal projections for the exact privacy officer title are limited, but privacy-related demand is supported by expanding regulation, AI governance, cybersecurity risk, and growing expectations around data protection.
- Future privacy officers will need to understand AI governance, privacy-by-design, vendor risk, cross-border compliance, and the relationship between privacy and cybersecurity.
- BLS. (2025, August 28). Compliance Officers. Retrieved October 28, 2025, from BLS.
- Jodka, S. (2025, March 28). The privacy tug-of-war: States grappling with divergent consent standards. Retrieved October 28, 2025, from Reuters.
- Salary.com. (n.d.) Privacy Officer Salary in the United States. Retrieved October 28, 2025, from Salary.com.
- Stupp, C. (2024, September 5). AI, Growing Data Risks Expand the Role of Chief Privacy Officer. Retrieved October 28, 2025, from Wall Street Journal.
- Zippia. (n.d.). Information Officer Job Outlook And Growth In The US. Retrieved October 28, 2025, from Zippia.