2027 Information Security Engineer Careers: Skills, Education, Salary & Job Outlook

Co-Founder and Chief Data Scientist
Choosing an information security engineer career means deciding whether you want a technical role built around protecting systems, reducing business risk, and responding to real cyber threats. The work is demanding: employers expect fluency in operating systems, network protocols, cryptography, cloud environments, vulnerability management, and incident response. They also expect judgment, because security engineers often decide which risks need immediate action and which controls are realistic for the organization.
The career can be attractive for students, IT professionals, software developers, network administrators, and analysts who want a higher-impact cybersecurity role. It also requires planning. A strong path usually combines a relevant degree, hands-on technical experience, recognized certifications, and continuous learning as threats and tools change.
Demand is a major reason people consider this field. Employment for information security roles is expected to grow 32% through 2032, with median salaries around $125,000 and top earners reaching $170,000. This guide explains what information security engineers do, which skills and credentials matter, how earnings and job outlook look, and how to decide whether this career fits your strengths and long-term goals.
Key Things You Should Know About Information Security Engineer Career
- The typical earning potential for an information security engineer ranges from about $102,573 to $126,833 annually, reflecting experience and data source differences.
- This field is highly stable and growing, with related roles like information security analysts expected to expand by 32% from 2022 to 2032, much faster than average.
- A bachelor's degree in computer science, information technology, cybersecurity, or a related field is usually required to start, with professional certifications like CISSP, CISM, or CompTIA Security+ often preferred.
- Success depends on skills in network and system security, firewalls, intrusion detection, risk assessment, incident response, strong problem-solving, analytical thinking, communication, and continuous learning.
- Career advancement can lead to positions such as senior information security engineer, information security manager, chief information security officer, or specialized roles in penetration testing, threat intelligence, or security architecture.
What do Information Security Engineers do?
Information security engineers design, build, test, and maintain the defenses that protect an organization’s systems and data. Their work sits between engineering, operations, and risk management. They do not simply “monitor alerts”; they help create secure networks, harden systems, evaluate vulnerabilities, implement security tools, and respond when something goes wrong.
In practical terms, an information security engineer turns security requirements into working technical controls. That may include configuring firewalls, securing cloud environments, improving identity and access management, reviewing logs, automating detection workflows, testing for weaknesses, or helping teams recover from an attempted breach.
A day in the life of Information Security Engineers
A typical day combines planned security work with unexpected issues. An engineer may start by reviewing overnight alerts, checking vulnerability scan results, or investigating suspicious activity. Later, they may join a meeting with infrastructure, software, compliance, or leadership teams to explain risk and recommend fixes. Some days are quiet and focused on architecture or documentation; others are shaped by urgent incident response.
The role is best suited for people who like technical problem-solving, can stay calm under pressure, and are comfortable explaining complex security risks to nontechnical stakeholders. The strongest engineers are not only good at finding problems; they know how to help the organization fix them without disrupting essential operations.
What are the key responsibilities of Information Security Engineers?
Information security engineers are responsible for strengthening an organization’s defenses before an attack happens and helping contain damage when incidents occur. Their responsibilities vary by employer size and industry, but most roles include a mix of prevention, detection, response, and policy support.
- Monitor security systems and alerts: Review logs, intrusion detection data, endpoint alerts, and security dashboards to identify unusual activity.
- Design and maintain security controls: Configure and improve firewalls, intrusion detection and prevention systems, endpoint protection, access controls, encryption, and secure network architecture.
- Assess vulnerabilities: Run vulnerability scans, support penetration tests, prioritize weaknesses, and communicate remediation steps to technical teams.
- Respond to incidents: Investigate alerts, contain threats, coordinate recovery, preserve evidence when needed, and document lessons learned.
- Support compliance and policy work: Help develop security standards, procedures, and documentation that align with regulatory and business requirements.
- Train and advise staff: Promote secure practices, explain risks to employees and teams, and support security awareness efforts.
- Improve security processes: Automate repetitive checks, refine detection rules, and recommend tools or controls that reduce risk.
The most challenging vs. the most rewarding tasks
The hardest part of the job is often incident response. During an active breach or high-risk alert, engineers must analyze incomplete information, act quickly, coordinate across teams, and make decisions that may affect data, revenue, operations, and reputation. The pressure can be high because delays or mistakes can increase the damage.
The most rewarding part is seeing prevention and response work succeed. Blocking an attack, closing a serious vulnerability, or helping a company recover safely gives the role a clear sense of purpose. For professionals who want to deepen their credentials quickly, 1 year online masters programs may be worth comparing, especially if they align with cybersecurity, information assurance, or a related technical field.
What are the key skills for Information Security Engineers?
Information security engineers need a balance of technical depth, risk judgment, and communication skills. Tools change, but the underlying skill set remains consistent: understand systems, identify weaknesses, reduce risk, and explain what needs to happen next.
Core hard skills
- Networking and operating systems: Understand TCP/IP, routing, DNS, firewalls, Linux, Windows, and common enterprise infrastructure.
- Threat analysis and mitigation: Recognize attack patterns, evaluate indicators of compromise, and recommend controls that reduce exposure.
- Cloud security architecture: Design and secure cloud environments, permissions, workloads, and configurations while supporting compliance requirements.
- Risk assessment and management: Evaluate vulnerabilities based on severity, likelihood, business impact, and available resources.
- Programming and scripting: Use Python, SQL, and related tools to automate tasks, analyze data, and support investigations.
- Vulnerability management: Run scans, validate findings, prioritize remediation, and track fixes.
- Identity and access management: Support least privilege, multifactor authentication, role-based access, and access review processes.
Key soft skills
- Critical thinking: Separate real threats from noise and make decisions when information is incomplete.
- Complex problem solving: Work through layered technical issues that may involve networks, applications, users, and third-party services.
- Active listening: Understand what business, IT, legal, and compliance teams need before recommending security changes.
- Judgment and decision making: Prioritize urgent risks without overreacting to every alert.
- Clear communication: Explain technical findings in language that executives, managers, and nonsecurity staff can act on.
The one overlooked skill that separates the good from the great
Business acumen is one of the most important differentiators. A skilled engineer can identify a vulnerability; a stronger engineer can explain how that vulnerability could affect revenue, customer trust, compliance exposure, operational downtime, or strategic priorities.
This matters because security teams rarely have unlimited time or budget. Engineers who connect technical risk to business impact are more likely to secure leadership support, prioritize the right fixes, and avoid security recommendations that are technically ideal but operationally unrealistic.
For those still choosing an academic route, an easy degree may sound appealing, but the better question is whether the program builds the technical foundation employers expect. Look for coursework in networking, systems administration, cybersecurity, programming, risk management, and hands-on labs.
Becoming an information security engineer is usually a staged process. Most people do not begin in a full engineering role on day one. They build a foundation in IT, gain hands-on experience, earn credentials, and then move into roles with greater responsibility for security architecture, incident response, and risk reduction.
- Build core IT knowledge. Learn how networks, servers, operating systems, databases, cloud platforms, and identity systems work. Security engineering depends on understanding what you are protecting.
- Complete relevant education. A degree in cybersecurity, computer science, information technology, computer systems engineering, or a related field can provide structure and credibility.
- Get hands-on practice. Use internships, help desk work, systems administration, network support, security analyst roles, labs, capture-the-flag exercises, and home projects to turn theory into skill.
- Learn security tools and workflows. Practice with vulnerability scanners, SIEM platforms, endpoint tools, firewalls, cloud security tools, ticketing systems, and incident response procedures.
- Earn certifications strategically. Choose certifications that match your level and target role rather than collecting credentials without a plan.
- Move into specialized security work. Pursue roles in cloud security, vulnerability management, incident response, security architecture, penetration testing, or governance, risk, and compliance.
- Keep learning continuously. Threats, regulations, tools, and platforms change quickly. Ongoing training is part of the job, not an optional extra.
A practical starting path might be help desk or IT support, then network or systems administration, then security analyst, and finally information security engineer. Some candidates enter more directly through cybersecurity internships or strong technical degree programs, but employers still value proof that you can solve real technical problems.
Most information security engineer roles require a relevant bachelor’s degree or equivalent technical experience. Common degree options include a Bachelor of Science in Cyber Security Engineering, Cybersecurity and Information Assurance, or Computer Science. Degrees in Information Technology or Computer Systems Engineering with a cybersecurity focus can also prepare candidates well.
Formal education is important, but it is not enough by itself. Employers typically look for hands-on experience with systems, networks, cloud environments, security tools, and incident response. On-the-job training may come through internships or at least three years of experience in IT or security analyst roles before advancing into engineering responsibilities.
Common certifications
Certifications can help verify knowledge, especially when paired with practical experience. The Certified Information Systems Security Professional (CISSP) issued by (ISC)² and CompTIA Security+ are widely recognized and often required. Security+ is often more suitable earlier in a career, while CISSP is commonly associated with more experienced professionals and broader security leadership knowledge.
Other certifications can be useful when they match a target specialization. For example, Certified Cloud Security Professional (CCSP) may support cloud security goals, while Offensive Security Certified Professional (OSCP) may be more relevant for penetration testing or offensive security work.
Are advanced degrees or niche certifications worth the investment?
Advanced degrees such as a Master of Science in Cyber Security Engineering or Cybersecurity and Information Assurance can support advancement into leadership, architecture, research, policy, or specialized technical roles. They may also improve marketability for employers that prefer graduate credentials. However, graduate study takes time and money, and many employers weigh demonstrated experience and certifications heavily.
Niche certifications are most valuable when they map directly to your next role. A cloud security credential may be worthwhile if your job involves cloud architecture. A hands-on offensive security certification may be worthwhile if you want red team or penetration testing work. A credential is less useful if it does not build skills you will actually use.
If you are comparing graduate options, fast masters degrees can be part of the research process. Before enrolling, confirm accreditation, curriculum quality, faculty expertise, hands-on learning opportunities, total cost, and whether the program’s outcomes match your career goal.
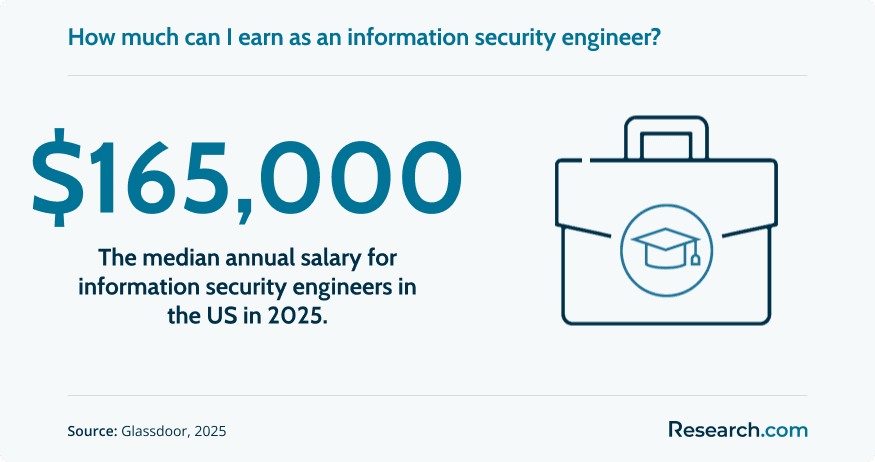
The earning potential for information security engineers is strong, but salaries vary by job title, employer, location, industry, security specialization, years of experience, and credentials. The information security engineer highest earning potential begins around a median annual salary of $102,573 in 2025, making the role competitive within the broader technology labor market.
The information security engineer starting salary 2025 is approximately $68,952 for professionals with less than one year of experience. Experienced professionals can earn up to $141,000 annually, showing meaningful growth as responsibilities expand and technical judgment improves.
Several factors can raise or lower compensation:
- Experience level: Engineers who can independently design controls, lead investigations, and guide remediation usually earn more than entry-level staff.
- Specialization: Cloud security, security architecture, incident response, penetration testing, and governance, risk, and compliance can command different pay levels depending on employer needs.
- Industry: Finance, insurance, technology, government contracting, healthcare, and critical infrastructure may have different salary structures and compliance demands.
- Location and work model: Metropolitan labor markets and remote-first employers may price roles differently.
- Certifications and education: Credentials can strengthen a candidate’s profile, but they usually have the greatest value when backed by hands-on experience.
When evaluating salary offers, look beyond base pay. Bonuses, shift expectations, on-call requirements, training budgets, certification reimbursement, remote-work flexibility, and career progression can change the real value of a role.
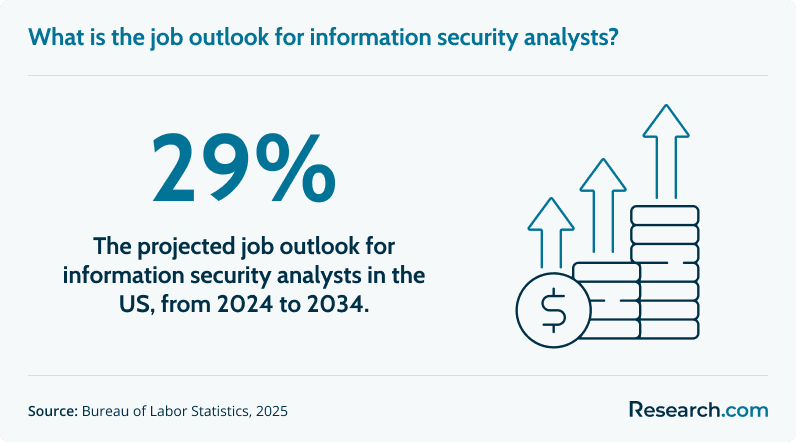
The job outlook for information security engineers is strong, with a projected 29% growth rate from 2024 to 2034. That growth is much faster than the average for all occupations and reflects the increasing need for organizations to secure data, networks, cloud platforms, applications, and digital operations.
Cybersecurity work also tends to be resilient because security risk does not disappear during economic downturns. Even when technology hiring slows, organizations still need professionals who can protect systems, satisfy compliance requirements, and respond to incidents.
The key factors shaping the future outlook
- More frequent and sophisticated attacks: Organizations need engineers who can defend against ransomware, phishing, credential theft, supply-chain attacks, and cloud misconfigurations.
- Regulatory pressure: Requirements such as GDPR and SEC breach disclosures increase the need for security controls, documentation, monitoring, and response capability.
- Cloud adoption: As companies move workloads and data to cloud platforms, they need engineers who understand shared responsibility, identity controls, logging, encryption, and secure configuration.
- Remote and hybrid work: Distributed work expands the number of devices, networks, and access points that must be secured.
- IoT and connected systems: More connected devices create more possible entry points for attackers.
For professionals who want to move toward research, executive leadership, or highly specialized academic and policy roles, the shortest online doctoral programs may be worth reviewing. For most engineering roles, however, employers will continue to place heavy weight on practical experience, technical credibility, and current security skills.
Information security engineers usually work in corporate offices, technology firms, financial institutions, government environments, healthcare organizations, consulting firms, or managed security service providers. Many roles are now remote or hybrid because much of the work involves digital systems, cloud platforms, logs, tickets, and collaboration tools.
Industry distribution also shows where demand is concentrated: 26% are employed in computer systems design and related services, 19% in finance and insurance, and 8% in management of companies and enterprises. These settings often have complex systems, valuable data, and strong compliance needs.
A typical workday includes independent technical analysis and frequent collaboration. Engineers may work with IT operations, software developers, cloud teams, risk managers, legal staff, compliance officers, vendors, and executives. Clear communication is essential because security recommendations often require other teams to change systems, patch software, adjust permissions, or accept temporary disruption.
Do security engineers work weekends? Usually, the schedule follows standard weekday business hours, but evening or weekend work can happen during major incidents, maintenance windows, audits, migrations, or urgent security upgrades. Some roles include on-call rotations. Candidates should ask about on-call expectations, incident volume, overtime policies, and staffing levels before accepting a position.
An information security engineer career can be highly rewarding, but it is not a low-pressure path. The same factors that make the role meaningful—high stakes, constant change, and direct responsibility for protecting systems—can also make it stressful. A realistic view of both sides helps you decide whether the career fits your temperament and goals.
Pros
- Strong impact: The work directly protects company assets, customer data, employee information, and business continuity.
- Continuous learning: New threats, technologies, and defense strategies keep the role intellectually engaging.
- Career mobility: Skills can transfer across industries, including finance, healthcare, technology, government, and consulting.
- Clear advancement routes: Engineers can move into senior technical roles, architecture, management, consulting, or executive security leadership.
- Meaningful collaboration: Security engineers often work across departments and influence organization-wide decisions.
Cons
- High-pressure incidents: Breaches and severe alerts can require fast decisions with limited information.
- Rapidly changing threats: Skills can become outdated if professionals stop learning.
- Compliance workload: Documentation, audits, and regulatory requirements can compete with hands-on technical work.
- Resource constraints: Security teams may have to protect complex systems with limited budgets, older tools, or understaffed teams.
- On-call demands: Some roles require availability outside normal business hours.
This career is a strong fit for people who enjoy technical depth, can tolerate ambiguity, and want work with visible consequences. If you are testing the field before committing to a degree or major career change, good paying certifications can help you compare shorter training options and identify credentials that may support entry-level opportunities.
Information security engineer career advancement can follow two main directions: technical specialization or leadership. Some professionals become senior experts who design complex defenses and guide architecture decisions. Others move into management, risk leadership, or executive roles.
Advancement paths
- Junior or entry-level information security engineer: Handles foundational tasks such as alert review, network security support, endpoint protection, documentation, and basic vulnerability management.
- Information security engineer: Designs and maintains controls, investigates incidents, supports secure architecture, and works with IT and business teams to reduce risk.
- Senior information security engineer: Leads complex projects, improves detection and response processes, mentors junior staff, and handles higher-risk technical decisions.
- Security architect or cybersecurity manager: Shapes enterprise security strategy, designs secure systems, leads teams, and coordinates security programs.
- Chief information security officer (CISO) or director of security: Oversees cybersecurity policy, budget, risk governance, incident readiness, and executive communication.
Specialization opportunities
Specialization can help engineers stand out and qualify for more advanced roles. The best choice depends on whether you prefer hands-on technical work, strategic design, investigation, compliance, or leadership.
- Cloud security: Protecting cloud infrastructure, applications, identities, configurations, and automated deployment pipelines.
- Penetration testing / red team operations: Simulating attacks, identifying exploitable weaknesses, and helping organizations improve defenses.
- Security architecture: Designing secure systems, selecting controls, integrating threat intelligence, and aligning architecture with business risk.
- Governance, risk, and compliance (GRC): Managing risk frameworks, audits, policies, regulatory requirements, and control documentation.
- Incident response and forensics: Investigating breaches, containing threats, analyzing evidence, and improving recovery procedures.
Advancement depends on more than tenure. Engineers who document results, communicate clearly, mentor others, understand business priorities, and keep their skills current are more likely to move into senior and leadership roles.
If information security engineering interests you, several related careers may also fit. The right choice depends on whether you prefer hands-on technical defense, policy and compliance, software development, investigation, consulting, or privacy work.
- Risk Management Consultant: Assesses security and operational risks across organizations, recommends controls, and helps leaders make informed risk decisions.
- Data Privacy Officer: Focuses on data protection laws, privacy strategy, consent practices, data handling, and compliance obligations.
- Security Software Developer: Builds secure applications, security tools, authentication systems, or code-level protections against common vulnerabilities.
- Forensic Computer Analyst: Investigates incidents, analyzes digital evidence, reconstructs events, and supports cybercrime or internal investigations.
- Information Security Analyst: Monitors systems, reviews alerts, investigates threats, and supports day-to-day security operations.
A useful way to choose is to compare your preferred work style. If you like building and configuring defenses, information security engineering may fit well. If you prefer investigation, consider forensics or incident response. If you enjoy law, policy, and documentation, privacy or GRC may be better. If you like coding, security software development may be the stronger path.
- : "In my role as an information security engineer, I often think about how the work protects more than company data. A single stopped breach can prevent financial and personal harm for many people. Speaking at industry events and mentoring junior colleagues also makes the role feel larger than my own team. Those moments make the late nights feel worthwhile. —Jefferson"
- : "The hardest part is how quickly threats change. Before one major pentest, I had very little information and had to use unconventional tactics, including social engineering, to understand the environment. Early in my career, I often wondered whether I knew enough. Taking on difficult work and staying curious helped me move past that doubt. —Reynel"
- : "One of the best feelings is finding a complex vulnerability that others missed and helping the client fix it. Passing difficult certifications gave me confidence, but mentoring newer engineers showed me that my growth was not just technical. The appreciation from teammates and clients reminds me why I chose this field. —Daniel"
Key Findings
- Information security engineers protect systems and data by designing defenses, managing vulnerabilities, monitoring threats, and responding to incidents.
- The role requires strong technical foundations in networking, operating systems, cloud security, risk management, scripting, and security tools.
- Soft skills matter. Clear communication, judgment, business awareness, and calm decision-making are essential during high-pressure security events.
- A common path includes relevant education, hands-on IT or security experience, certifications, and specialization in areas such as cloud security, incident response, architecture, or GRC.
- Salary potential is strong, with a median annual salary of $102,573 in 2025, an information security engineer starting salary 2025 of approximately $68,952, and experienced professionals earning up to $141,000 annually.
- The job outlook is favorable, with a projected 29% growth rate from 2024 to 2034.
- The career offers meaningful impact and advancement potential, but candidates should be prepared for continuous learning, compliance demands, occasional on-call work, and high-pressure incidents.
Other Things You Should Know About Information Security Engineer
Artificial intelligence is reshaping information security by increasing the complexity of cyber threats like AI-generated phishing, deepfakes, and automated attacks. Simultaneously, it provides powerful defense tools such as AI-driven anomaly detection and automated incident response. This shift urges engineers to master AI integration and focus on solving intricate, unique security challenges rather than routine tasks.
A Bachelor’s degree in computer science, information technology, or cybersecurity is most beneficial for aspiring Information Security Engineers in 2026. This foundational education, coupled with industry certifications like CISSP or CISM, prepares individuals for technical challenges and advances their career prospects.
- Steps for becoming a cybersecurity engineer | edX https://www.edx.org/become/how-to-become-a-cybersecurity-engineer
- Cyber Security Job FAQs https://www.wgu.edu/blog/faqs-about-cyber-security-jobs1810.html
- Top 10 Pros and Cons of Cyber Security in 2025 https://www.stationx.net/pros-and-cons-of-cyber-security/
- Cyber Security Engineer Interview Questions and Answers https://www.digitalregenesys.com/blog/cyber-security-engineer-interview-questions
- What Is a Security Engineer? 2025 Career Guide https://www.coursera.org/gb/articles/what-is-a-security-engineer
- Computer and Information Technology Occupations: Occupational Outlook Handbook: U.S. Bureau of Labor Statistics https://www.bls.gov/ooh/computer-and-information-technology/
- Pros and cons of working in cybersecurity: is it right for you? https://www.upskilled.edu.au/skillstalk/pros-and-cons-working-in-cybersecurity
- How to Become a Security Engineer https://cybersecurityguide.org/careers/security-engineer/
- Cybersecurity Engineer Skills in 2025 (Top + Most Underrated Skills) https://www.tealhq.com/skills/cybersecurity-engineer