2027 Cybersecurity Careers: Skills, Education, Salary & Job Outlook

Co-Founder and Chief Data Scientist
Choosing a cybersecurity career means deciding whether you are ready to build technical depth, stay current with fast-changing threats, and work in roles where mistakes can have real consequences. The path is demanding, but it is not limited to people with advanced degrees or years of coding experience. Many professionals enter through IT support, networking, security operations, degree programs, certifications, internships, labs, or military and government-adjacent experience.
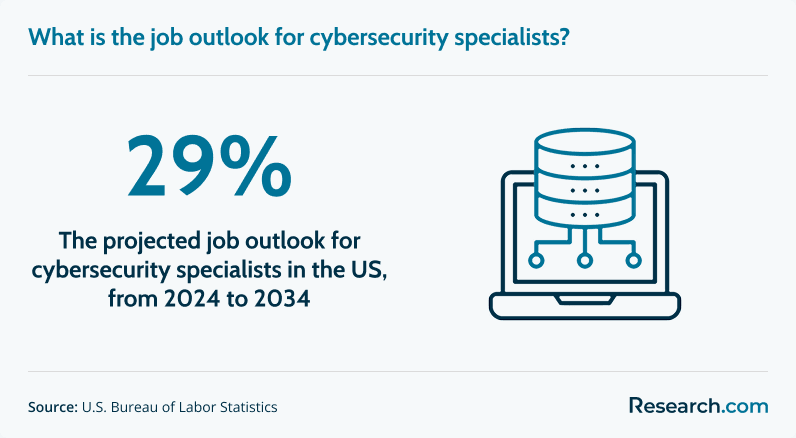
The appeal is clear: jobs in this field are projected to grow 32% through 2032, and some cybersecurity roles report median salaries above $120,000. Still, pay and opportunity vary by role, location, employer, clearance requirements, experience, and specialization. This guide explains what cybersecurity specialists do, what skills and credentials matter, how to get started, what the work environment is like, and how to decide whether this career fits your strengths and long-term goals.
Key Things You Should Know About Cybersecurity Career
- The typical earning potential for cybersecurity specialists in the U.S. is around $124,910 annually, reflecting a strong, well-compensated career path.
- This field is expanding rapidly, with a job outlook growth rate of 32% from 2022 to 2032, making it one of the most stable and in-demand professions.
- A bachelor's degree in computer science, information technology, or a related field is usually required to start, along with industry certifications that boost employability.
- Success depends on mastering network security, risk assessment, incident response, penetration testing, and effectively communicating complex issues.
- Career growth typically moves from security analyst to engineer, then to manager or architect roles, with top opportunities leading to chief information security officer or director positions.
What do Cybersecurity Specialists do?
Cybersecurity specialists help organizations prevent, detect, investigate, and respond to digital threats. Their work protects networks, systems, cloud environments, applications, employee accounts, customer records, financial data, and other critical information assets. In practical terms, they reduce the chance that attackers can steal data, disrupt operations, damage systems, or exploit security weaknesses.
The role can look different by employer. In a smaller organization, a cybersecurity specialist may handle a broad mix of monitoring, user training, tool configuration, policy support, and incident response. In a larger organization, the role may be more specialized, such as security operations, vulnerability management, identity and access management, cloud security, compliance, or threat detection.
A Day in the Life of Cybersecurity Specialists
A typical day often includes reviewing alerts, investigating unusual activity, documenting findings, checking system logs, coordinating with IT teams, updating security tools, and communicating risks to managers or business units. Some days are routine and analytical; others are urgent, especially when a suspected breach, malware infection, phishing campaign, or system vulnerability requires immediate attention.
Cybersecurity specialists usually work closely with network administrators, system engineers, software teams, compliance staff, legal teams, vendors, and leadership. The best specialists are not only technically capable; they can explain risk clearly, prioritize what matters most, and help the organization make practical security decisions.
What are the key responsibilities of Cybersecurity Specialists?
Cybersecurity specialists are responsible for reducing security risk before an attack happens and responding effectively when suspicious activity appears. Their responsibilities depend on the organization’s size, industry, security maturity, and regulatory obligations, but most roles include a blend of monitoring, prevention, investigation, documentation, and user support.
- Monitor computer systems, networks, endpoints, and cloud environments for suspicious activity or signs of compromise.
- Investigate alerts from security tools and determine whether they represent real threats, false positives, misconfigurations, or user errors.
- Conduct vulnerability assessments and penetration tests to identify weaknesses before attackers can exploit them.
- Support incident response by helping contain threats, preserve evidence, remove malware, restore systems, and document lessons learned.
- Install, configure, and maintain security tools such as firewalls, endpoint protection, intrusion detection systems, and access control platforms.
- Develop, update, and enforce security policies, procedures, standards, and best practices.
- Train employees on phishing prevention, password hygiene, secure file handling, and other everyday security behaviors.
- Prepare reports that explain risks, remediation steps, incident timelines, or compliance status to technical and nontechnical audiences.
The Most Challenging vs. The Most Rewarding Tasks
The hardest part of the job is often incident response. During an active security event, specialists may have to make quick decisions with incomplete information, coordinate with multiple teams, and balance containment with business continuity. These situations can happen outside regular hours and may involve financial, legal, operational, or reputational risk.
The most rewarding work is preventing a serious incident or stopping an attack before it causes damage. Finding a critical vulnerability, improving a weak process, or helping employees recognize a phishing attempt can have a measurable effect on organizational safety. For professionals who want to deepen their expertise quickly, a 12 month master's degree online may be one possible route, depending on career goals, cost, schedule, and prior experience.
What are the key skills for Cybersecurity Specialists?
Cybersecurity specialists need a balanced skill set. Technical ability matters, but so do judgment, communication, documentation, and the ability to connect security decisions to business priorities. The cybersecurity competencies roadmap 2025 emphasizes that effective professionals combine hands-on technical knowledge with strong interpersonal and analytical skills.
Key Hard Skills for Cybersecurity Specialists
- Network security analysis: Understanding traffic patterns, protocols, segmentation, firewalls, VPNs, and signs of unauthorized access.
- Incident response: Investigating alerts, containing threats, documenting timelines, and helping systems return to safe operation.
- Scripting: Using tools such as Python or PowerShell to automate repetitive tasks, parse logs, analyze data, and support investigations.
- Vulnerability assessment: Identifying, validating, prioritizing, and tracking security weaknesses across systems and applications.
- Security tool fluency: Working with monitoring platforms, endpoint protection, identity systems, vulnerability scanners, and ticketing tools.
- Operating systems knowledge: Understanding Windows, Linux, and common server environments well enough to recognize abnormal behavior.
Essential Soft Skills
- Critical thinking: Separating real risks from noise and recognizing when an alert, pattern, or configuration deserves attention.
- Complex problem solving: Tracing security issues across systems, users, networks, vendors, and business processes.
- Active listening: Understanding what users, managers, engineers, and auditors are reporting before recommending a fix.
- Judgment and decision making: Choosing actions that reduce risk without unnecessarily disrupting business operations.
- Clear communication: Translating technical findings into plain language that leaders and nontechnical teams can act on.
The One Overlooked Skill That Separates the Good from the Great
Business acumen is often what separates a capable cybersecurity specialist from a trusted security leader. A specialist who understands revenue, operations, customer trust, compliance, and downtime can explain why a technical issue matters and help leaders choose the right response.
For example, identifying a critical vulnerability is useful. Explaining which business process it threatens, what could happen if it is exploited, how quickly it should be fixed, and what trade-offs are involved is far more valuable. This is especially important in organizations where security teams compete for budget, staffing, and executive attention.
Combining business acumen with the core cybersecurity skills employers want can support movement into higher-value roles, especially in the management of companies and enterprises sector-the top-paying industry. If you are still comparing educational starting points, researching what's the easiest degree to get can help you understand program formats, though cybersecurity success still depends on building real technical competence.
Starting a cybersecurity career is easier to plan when you treat it as a sequence of skill-building steps rather than a single leap into an advanced security role. Most beginners need a foundation in IT, networking, systems, and basic security concepts before they can credibly investigate threats or protect infrastructure.
- Build foundational IT knowledge. Learn how computers, operating systems, networks, user accounts, servers, and cloud services work. Cybersecurity is built on understanding the systems you are trying to protect.
- Earn entry-level education or certification. Consider an associate degree, bachelor's degree, certificate program, bootcamp, or foundational certification, depending on your budget, schedule, and starting point.
- Practice in labs and projects. Use hands-on labs, home networks, capture-the-flag exercises, virtual machines, and security tools to turn theory into practical ability.
- Gain experience in adjacent roles. IT support, help desk, systems administration, network administration, and technical support roles can provide the troubleshooting background many security teams value.
- Apply for entry-level security roles. Look for titles such as security analyst, SOC analyst, junior cybersecurity analyst, vulnerability analyst, or security operations technician.
- Develop a specialization. After gaining broad exposure, move toward areas such as penetration testing, digital forensics, cloud security, governance, risk, compliance, identity management, or security engineering.
- Pursue advanced responsibility. With experience, certifications, and strong results, move into senior analyst, lead specialist, architect, manager, consultant, or executive-track roles.
A common mistake is skipping the basics and applying only to security jobs that require experience. A stronger strategy is to build evidence of ability: completed labs, documented projects, internships, certifications, technical writing, volunteer work, or prior IT experience. Employers want proof that you can reason through security problems, not just interest in the field.
The most common qualifications for a cybersecurity specialist include an associate or bachelor's degree in Cybersecurity, Computer Science, Information Technology, or Information Systems. A Bachelor of Science (B.S.) degree is one of the most direct and common pathways, but it is not the only route. Employers may also value technical experience, internships, military training, labs, apprenticeships, and certifications.
Foundational certifications such as CompTIA Security+ and the Systems Security Certified Practitioner (SSCP) are often used to demonstrate entry-level knowledge. They can be especially helpful for candidates who need a structured way to prove familiarity with security principles, access controls, risk management, network defense, and incident response concepts.
On-the-job training remains essential. Cybersecurity is applied work, and many skills are developed through real alerts, real systems, real users, and real constraints. Internships, supervised junior roles, labs, competitions, and project-based coursework can help bridge the gap between classroom learning and job performance.
How to choose the right education path
| Path | Best for | Key trade-off |
| Associate degree | Students seeking a lower-cost foundation or a pathway into entry-level IT and security roles | May need additional experience, certifications, or a bachelor's degree for some employers |
| Bachelor's degree | Learners who want a broad academic foundation and access to roles that prefer or require a four-year degree | Requires more time and financial commitment than shorter options |
| Certifications | Career changers, IT workers, and students who need targeted proof of specific skills | Usually strongest when paired with hands-on practice or work experience |
| Bootcamps or short programs | Learners who want focused, practical training on a shorter timeline | Quality varies, and outcomes depend heavily on projects, support, and employer recognition |
| Internships and entry-level IT roles | Candidates who need real-world experience and professional references | May require starting outside cybersecurity before moving into a dedicated security role |
Are advanced degrees or niche certifications worth the investment?
Advanced degrees such as a Master of Science in Cybersecurity or Information Assurance can be useful for leadership, policy, research, architecture, or specialized technical roles. Niche certifications such as Certified Information Security Manager (CISM) or Certified Ethical Hacker (CEH) can also strengthen credibility when they match the role you want.
The investment is not automatically worth it for everyone. Advanced credentials can require significant time and money, and some employers place more weight on demonstrated skill, relevant experience, and strong references. Certifications may also require maintenance, continuing education, and renewal fees. Before enrolling, compare job descriptions for your target roles and look for patterns in required and preferred qualifications.
For candidates considering research or academic pathways, options such as a PhD with no dissertation may be worth exploring. For most aspiring cybersecurity specialists, however, the first priority should be a strong foundation, practical experience, and credentials aligned with the jobs they actually plan to pursue.
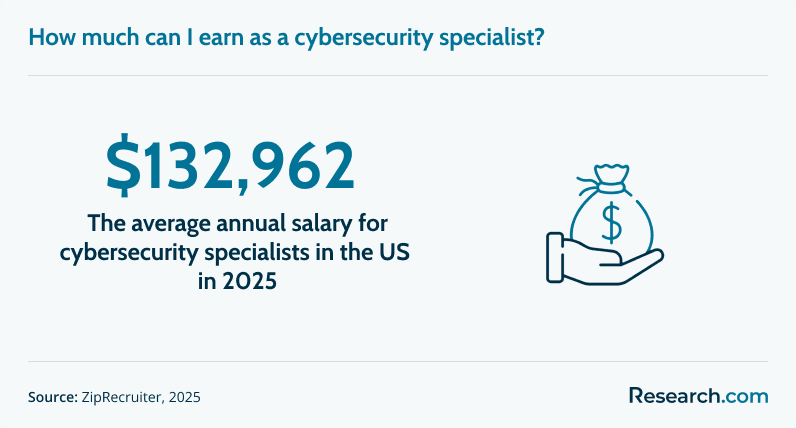
The median salary for a Cyber Security Specialist is $93,170 per year. Entry-level professionals earn about $78,500 annually, while experienced specialists with senior-level expertise can reach salaries near $132,500. These figures make cybersecurity financially attractive, but they should be treated as benchmarks rather than guarantees.
Actual earnings depend on several factors: job title, location, employer size, industry, education, certifications, security clearance requirements, years of experience, and specialization. Roles involving cloud security, incident response, architecture, governance, or leadership may pay differently from generalist security operations positions. Major metro areas and technology-heavy regions may offer higher salaries, but cost of living can reduce the real financial advantage.
When evaluating cybersecurity salary potential 2025, look beyond the headline number. Ask whether the role includes on-call work, overtime expectations, bonus eligibility, shift differentials, clearance requirements, remote flexibility, professional development support, and certification reimbursement. Total compensation and work-life fit matter as much as base salary.
The projected 10-year growth rate for cybersecurity specialists, reflected by information security analysts, is 32%, much faster than the average 3% growth across all occupations. This strong outlook is driven by the growing dependence on digital systems and the continuing need to protect data, infrastructure, financial transactions, customer accounts, and business operations.
The Key Factors Shaping the Future Outlook
Several forces support long-term demand. Cyberattacks continue to increase in frequency and sophistication, which pushes organizations to invest in threat detection, vulnerability management, incident response, and security architecture. Regulatory and compliance requirements also continue to expand, especially in industries that handle financial, healthcare, government, education, or consumer data.
Cloud adoption, remote work, connected devices, and digital transformation have widened the attack surface. As organizations move more systems online, they need professionals who can secure cloud platforms, identity systems, endpoints, applications, and third-party integrations. This demand can create opportunities for both new entrants and experienced IT professionals who reskill into security.
Job seekers should still expect competition for desirable entry-level roles. A strong outlook does not mean every applicant will be hired quickly. Candidates who combine education, hands-on practice, certifications, internships, prior IT experience, and clear communication skills are usually better positioned. If affordability is a concern, comparing online schools accepting financial aid may help you find a practical education path.
Cybersecurity specialists commonly work in office, hybrid, or remote settings, depending on the employer and the sensitivity of the systems they support. Many roles are based at company headquarters, IT centers, security operations centers, consulting firms, government contractors, financial institutions, healthcare organizations, universities, or technology companies.
Industry concentration varies. Cybersecurity specialists are commonly employed in computer systems design and related services (26%), finance and insurance (19%), and management of companies and enterprises (9%). These settings often require collaboration with IT operations, software development, compliance, risk management, legal, and executive teams.
Work hours depend on the role. Many specialists work standard business hours, but security incidents do not always follow a predictable schedule. Evening, weekend, or on-call work may be required during breaches, major vulnerabilities, system upgrades, audits, or urgent investigations. Security operations center roles may also involve shift work because monitoring may need to continue around the clock.
Remote work is increasingly common in cybersecurity, especially for monitoring, analysis, governance, consulting, and cloud-focused roles. However, some employers require onsite work because of classified systems, physical infrastructure, regulatory controls, hardware access, or incident response needs. Candidates should ask about on-call expectations, shift schedules, remote work policies, and emergency response procedures before accepting a role.
Cybersecurity can be meaningful, well-compensated, and intellectually engaging, but it is not a low-pressure career. The work requires constant learning, attention to detail, and the ability to act calmly when systems, data, or business operations may be at risk.
Pros
- Strong sense of purpose: Cybersecurity specialists protect people, organizations, data, and critical systems from real threats.
- High demand: The field benefits from strong projected growth and continued organizational need for security expertise.
- Varied career paths: Professionals can move into technical, investigative, compliance, consulting, management, or executive roles.
- Continuous learning: New tools, threats, and technologies keep the work intellectually active.
- Visible impact: Preventing a breach, improving controls, or responding well to an incident can earn trust across the organization.
Cons
- High-pressure incidents: Breaches and urgent vulnerabilities can require fast decisions with incomplete information.
- On-call demands: Some roles require evening, weekend, holiday, or shift work.
- Constant change: Professionals must keep learning as attack methods, tools, regulations, and systems evolve.
- Alert fatigue: Monitoring tools can generate large volumes of alerts, some of which may be repetitive or low value.
- Documentation burden: Policies, audits, reports, and compliance work are important but may feel less engaging than technical problem solving.
This career is a strong fit for people who enjoy investigation, structured problem solving, technology, risk reduction, and continuous improvement. It may be less appealing if you want highly predictable work, minimal stress, or a field where skills remain stable for long periods. If you need flexible study options before entering the field, reviewing affordable online universities for working adults can help you compare programs that fit around work and family responsibilities.
Cybersecurity offers multiple advancement routes. Some professionals move into leadership, while others deepen their technical expertise and become specialists in high-demand domains. The best path depends on whether you prefer managing people and strategy, solving technical problems, investigating incidents, advising clients, or designing secure systems.
Advancement Paths in Cybersecurity
- Entry-Level Specialist / Analyst: Roles such as Cybersecurity Analyst and SOC Analyst focus on monitoring alerts, documenting incidents, supporting investigations, and learning core security operations.
- Senior Specialist / Lead Analyst: Positions such as Senior Cybersecurity Specialist and Threat Hunter involve leading investigations, improving detection logic, mentoring junior staff, and managing security projects.
- Management / Executive Roles: Titles such as Security Operations Manager and Chief Information Security Officer (CISO) focus on budgets, staffing, governance, risk strategy, executive reporting, and organization-wide security planning.
Specialization Areas in Cybersecurity
- Penetration Testing & Ethical Hacking: Simulating attacks, validating vulnerabilities, testing defenses, and helping organizations fix exploitable weaknesses.
- Digital Forensics & Incident Response: Investigating breaches, preserving digital evidence, reconstructing timelines, and supporting recovery.
- Cloud Security: Securing platforms such as AWS and Azure, improving identity controls, hardening configurations, and designing secure cloud architectures.
- Security Architecture & Engineering: Designing secure systems, networks, infrastructure, and controls that reduce risk before incidents occur.
- Governance, Risk & Compliance: Developing policies, managing audits, assessing enterprise risk, and helping organizations meet regulatory and contractual obligations.
To advance, build a record of measurable results. Examples include reducing unresolved vulnerabilities, improving response times, creating stronger documentation, leading incident reviews, mentoring junior analysts, automating manual tasks, or helping pass audits. Promotions often depend on trust, judgment, communication, and business impact as much as technical skill.
If cybersecurity interests you but you are unsure about becoming a cybersecurity specialist, compare related roles. Many use similar skills but differ in daily tasks, pressure level, technical depth, customer interaction, or specialization.
- Information Security Analyst: Monitors systems, evaluates risks, recommends protections, and develops security procedures. This role closely overlaps with cybersecurity specialist work and may be used interchangeably by some employers.
- Network Security Engineer: Designs, secures, and maintains network infrastructure. This path suits people who enjoy routers, firewalls, segmentation, traffic analysis, and secure connectivity.
- Incident Response Analyst: Investigates and contains security breaches. This role is a strong fit for people who like high-pressure analysis, timelines, evidence, and rapid response.
- Security Consultant: Assesses security programs, recommends improvements, and works across multiple client environments. It can offer variety but may involve travel, deadlines, and client-facing communication.
- Digital Forensics Analyst: Examines digital evidence after cybercrimes or policy violations. This role suits detail-oriented professionals interested in investigations, documentation, and evidence handling.
Use these comparisons to identify what you actually want from the work. If you prefer prevention and monitoring, security operations may fit. If you enjoy building systems, security engineering may be stronger. If you like investigation, consider incident response or forensics. If you enjoy advising and communicating with stakeholders, consulting or governance may be a better match.
- Harold: "I first got drawn to cybersecurity because I saw it as a way to protect national interests in a critical, often overlooked arena. Working in something that contributes directly to our country's security felt like a natural extension of my commitment to public service. The field is challenging but rewarding, especially knowing the work I do makes a tangible difference. It quickly became clear this was where I wanted to deepen my expertise and make an impact."
- Amina: "Starting out in cybersecurity during my school years was eye-opening because the students weren't shy about exploring system weaknesses, which gave me unique insight into what needed fixing. I remember discovering that students could print to any printer, including the headmaster's office, which posed a serious security flaw. Fixing that issue taught me how real-world systems can be vulnerable in unexpected ways. Hands-on experiences like this have shaped how I approach security challenges today."
- Jonas: "The most difficult part of breaking into cybersecurity was overcoming my own doubts, especially when I had little technical background and saw job listings asking for experience I didn't yet have. One project involved writing a security policy I named 'Tron,' inspired by the film, which locked down student settings but was misunderstood and deleted because of unclear naming. I rewrote it with clearer terminology, learning that communication is just as important as technical skill. That lesson stuck with me as I moved forward in my career."
Key Findings
- Cybersecurity specialists protect systems, networks, data, and users by preventing, detecting, investigating, and responding to cyber threats.
- The field is projected to grow 32% through 2032, with a 32% projected 10-year growth rate for information security analysts compared with 3% across all occupations.
- The median salary for a Cyber Security Specialist is $93,170 per year, with entry-level professionals earning about $78,500 and experienced specialists reaching salaries near $132,500.
- Common education paths include an associate or bachelor's degree in Cybersecurity, Computer Science, Information Technology, or Information Systems, along with certifications such as CompTIA Security+ or SSCP.
- Hands-on experience matters. Labs, internships, IT support roles, SOC analyst positions, and real-world projects can be as important as classroom learning.
- Strong cybersecurity specialists combine technical skills with critical thinking, business acumen, communication, documentation, and sound judgment under pressure.
- The career offers multiple advancement paths, including senior analyst, threat hunter, penetration tester, cloud security specialist, security architect, governance and compliance professional, manager, and CISO.
- The trade-offs are real: cybersecurity can involve alert fatigue, constant learning, on-call work, documentation, and high-pressure incidents.
- This career is best for people who enjoy technical problem solving, continuous learning, risk reduction, and work that directly protects organizations and people.
Other Things You Should Know About Cybersecurity
In 2027, certifications like Certified Information Systems Security Professional (CISSP), Certified Ethical Hacker (CEH), and CompTIA Security+ are highly regarded for cybersecurity careers. These certifications validate skills in areas such as network security, risk management, and offensive security, making them crucial for advancing in the field.
In 2027, cybersecurity specialists can expect competitive salaries, with entry-level positions around $70,000 annually, while experienced professionals with advanced skills and certifications might earn upwards of $120,000 or more, depending on location and the complexity of their role.
In 2027, cybersecurity professionals must master skills like artificial intelligence integration, cloud security, and quantum computing defense. Understanding the latest encryption techniques and developing proficiency in threat intelligence and risk management are also crucial to tackle evolving cybersecurity challenges effectively.
- 6 In-demand Cybersecurity Roles — And The Skills Needed https://vervoe.com/skills-for-cybersecurity/
- Find a cybersecurity career https://cybersecurityguide.org/careers/
- Cybersecurity Career Pathway https://www.cyberseek.org/pathway.html
- 20 Coolest Cybersecurity Careers and Jobs | SANS Institute https://www.sans.org/cybersecurity-focus-areas/cybersecurity-careers/20-coolest-cyber-security-careers
- Our Cyber Security student success stories | Learning People https://www.learningpeople.com/au/resources/student-testimonials/our-cyber-security-student-success-stories/
- Answers to your questions about a career in cybersecurity - Women in cybersecurity — Kаspersky report https://wit.kaspersky.com/answers-to-your-questions-about-a-career-in-cybersecurity/
- 2025 Cybersecurity Hiring Trends: Why Investing in Entry- and Junior-Level Talent is Key to Building a More Resilient Cybersecurity Workforce https://www.isc2.org/Insights/2025/06/cybersecurity-hiring-trends-study
- Cybersecurity Job Description: What to Expect https://www.coursera.org/articles/cybersecurity-job-description
- What Skills Do Cyber Security Professionals Need? https://arxiv.org/html/2502.13658v1
- Cyber Security Specialist - Alternative Careers and Similar Jobs (Updated for 2025) https://resumeworded.com/career-profiles/cyber-security-specialist-career-profile