2027 How to Become a Security Architect: Education, Salary, and Job Outlook

Co-Founder and Chief Data Scientist
Becoming a security architect is a long-term cybersecurity career path for professionals who want to design how an organization prevents, detects, and withstands attacks. The role is not usually entry-level. It sits at the intersection of network security, cloud architecture, risk management, compliance, and executive decision-making.
Security architects help decide which systems are trusted, how data is protected, how users are authenticated, how incidents are contained, and how security controls support business operations. That makes the job valuable in finance, healthcare, government, education, technology, and any organization that depends on secure digital infrastructure.
This guide explains the credentials, skills, career steps, earning potential, internships, advancement options, work settings, challenges, and fit factors to consider if you are planning a security architect career for 2025 and beyond.
What are the benefits of becoming a security architect?
- The job outlook for security architects is strong, with a projected growth rate of 10% from 2023 to 2033, reflecting increasing demand for cybersecurity expertise.
- Average salary ranges from $110,000 to $160,000 annually, depending on experience, location, and industry specialization.
- Security architects play a critical role in protecting organizational assets, making this career a stable and rewarding choice amid rising cyber threats.
What credentials do you need to become a security architect?
To become a security architect in the United States, you generally need a combination of formal education, cybersecurity experience, recognized certifications, and ongoing professional development. Employers rarely hire architects based on credentials alone; they look for evidence that you can design secure systems, evaluate risk, and make security decisions that hold up in real business environments.
Core credentials employers commonly expect
- Bachelor's degree: A bachelor's degree in computer science, cybersecurity, information technology, or network engineering is widely considered essential. The strongest programs build a foundation in networking, operating systems, programming, databases, secure systems design, cryptography, risk management, and compliance frameworks.
- Advanced degrees: Many employers prefer or require a master's degree in cybersecurity, information assurance, or a related discipline for management-level or enterprise architecture roles. A graduate degree can be especially useful if you want to move into governance, enterprise security strategy, security leadership, or highly regulated sectors.
- Professional certifications: Entry and mid-career credentials such as CompTIA Security+ and Certified Ethical Hacker (CEH) can help validate technical knowledge. Senior security architect roles often favor advanced credentials such as Certified Information Systems Security Professional (CISSP), Certified Cloud Security Professional (CCSP), AWS Security Specialty, Microsoft Cybersecurity Architect Expert, TOGAF, or SABSA.
- Ongoing education and renewal: Cybersecurity credentials usually require continuing education or renewal. This is not a formality. Security architects must keep current with cloud platforms, identity systems, regulatory changes, AI-related risks, zero trust models, software supply chain security, and new attack techniques.
How to choose the right credential path
If you are early in your career, prioritize a degree or foundational certification plus hands-on IT experience. If you already work in cybersecurity, choose certifications that match the architecture work you want to do: cloud, enterprise security, application security, identity and access management, or governance. If you plan to work in finance, healthcare, or government, compliance knowledge can be as important as technical skill.
Credential expectations do not vary much by U.S. state, but they can vary significantly by industry and employer. Regulated sectors such as finance and healthcare may place more weight on compliance, audit readiness, data protection, and risk documentation. If you need a more flexible route to complete academic requirements, fast track online degrees may help you compare accelerated options while still evaluating accreditation, curriculum quality, cost, and student support.
What skills do you need to have as a security architect?
A strong security architect needs more than broad cybersecurity knowledge. The role requires the ability to design secure systems, explain trade-offs, challenge weak assumptions, and align technical controls with business risk. The best candidates combine deep technical fluency with judgment, communication, and leadership.
Technical skills
- Network Security & Architecture: You should understand TCP/IP, DNS, routing, segmentation, firewalls, VPNs, intrusion detection, secure remote access, and resilient network design. Architects are often responsible for deciding where controls belong and how systems should communicate safely.
- Cloud Security: Security architects need practical knowledge of AWS, Azure, and Google Cloud security models, including identity management, encryption, logging, key management, network controls, workload protection, and shared responsibility boundaries.
- Cryptography & Encryption: You do not need to invent algorithms, but you should understand how AES, RSA, public key infrastructure, certificate management, hashing, tokenization, and key rotation protect confidentiality and integrity.
- Secure System Design & DevSecOps: Architects help embed security into the software development lifecycle. That includes threat modeling, secure coding standards, vulnerability scanning, dependency review, secrets management, infrastructure as code, and automated security testing.
- Security Information and Event Management (SIEM): Tools such as Splunk and QRadar help organizations collect logs, detect suspicious behavior, and support incident response. Architects should understand what must be logged, how alerts are tuned, and how monitoring supports investigation.
- Scripting & Automation: Python, PowerShell, and similar tools help automate repetitive security tasks, validate configurations, collect evidence, and scale security operations across large environments.
- Operating Systems: Security architects should understand Linux, Windows, and MacOS security features, hardening practices, authentication mechanisms, patching, privilege management, and common misconfigurations.
Risk, governance, and business skills
- Incident Response & Risk Management: Architects must design systems with failure in mind. That means planning for detection, containment, forensics, recovery, and business impact—not just prevention.
- Security Governance: You need to work with frameworks and regulations such as ISO 27001, NIST, GDPR, HIPAA, and PCI DSS. The goal is to build security programs that are practical, auditable, and aligned with organizational obligations.
- Risk Assessment: Security architecture is about prioritization. You must evaluate likelihood, impact, exposure, control effectiveness, and legal or operational consequences before recommending investments.
- Compliance Integration: Architects help ensure that systems are designed to meet applicable data protection, privacy, audit, and reporting requirements from the start rather than after deployment.
Leadership and professional skills
- Communication: You must explain technical risk clearly to engineers, legal teams, executives, auditors, and nontechnical stakeholders. A strong recommendation is only useful if decision-makers understand it.
- Collaboration & Leadership: Security architects often influence teams they do not directly manage. Success depends on building trust with developers, infrastructure teams, product leaders, vendors, and executives.
- Problem-Solving & Integrity: This role requires disciplined judgment, confidentiality, ethical decision-making, and the courage to identify unacceptable risk even when it creates short-term friction.
What is the typical career progression for a security architect?
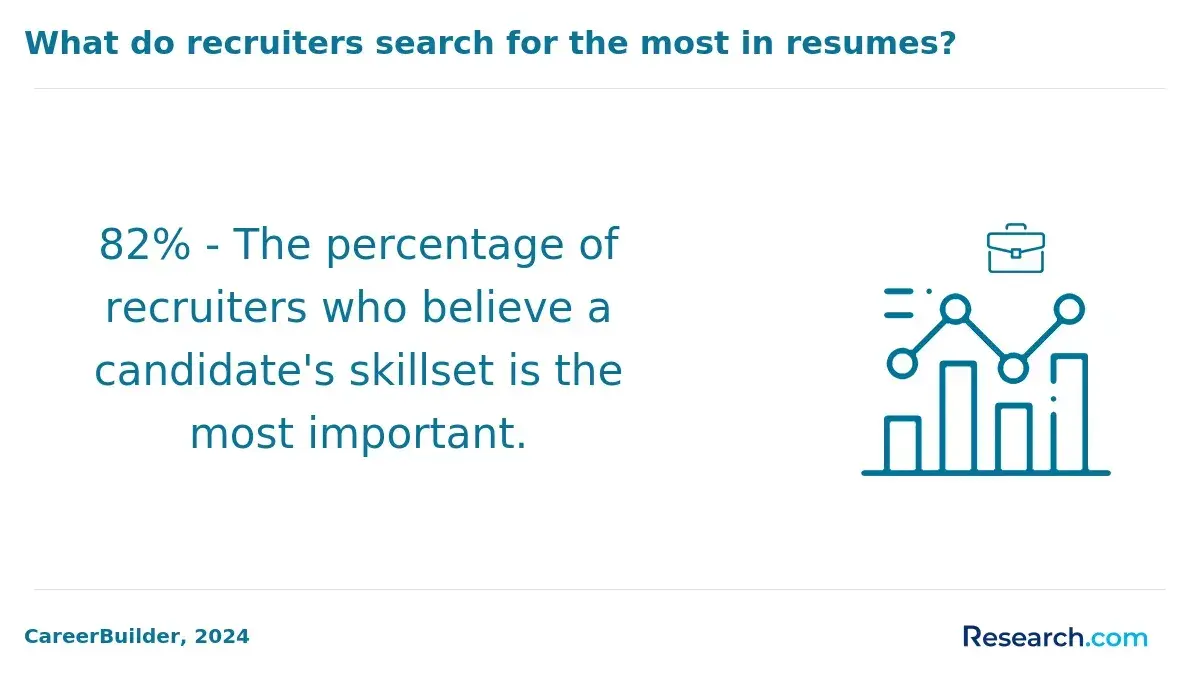
Security architect is usually a senior role reached after several years of hands-on IT and cybersecurity work. Most professionals build credibility by first learning how systems are deployed, attacked, monitored, repaired, and governed. The more experience you have with real incidents, migrations, audits, and trade-offs, the better prepared you are to design architecture that works outside a diagram.
- Start in foundational IT or cybersecurity roles: Many security architects begin as Security Analysts, Network Administrators, Systems Administrators, or Penetration Testers. These roles build practical skills in threat identification, system configuration, access control, vulnerability management, and incident handling, typically over 2 to 5 years.
- Move into engineering or consulting roles: Mid-level positions such as Security Engineer, Cybersecurity Consultant, or Systems Architect help you shift from monitoring and maintenance into implementation, audits, control design, architecture review, and technical advisory work.
- Reach the security architect level: Many professionals move into the Security Architect role after roughly 5 to 10 years of combined IT and cybersecurity experience. At this stage, employers expect you to evaluate risk, design secure environments, guide enterprise security strategy, and defend your recommendations to technical and business leaders.
- Advance into senior architecture leadership: Roles such as Lead Security Architect, Principal Security Architect, or Enterprise Security Strategist involve mentoring, setting standards, reviewing major technology decisions, leading architecture boards, and shaping long-term security direction.
- Specialize by domain: Common specialization paths include Cloud Security Architect, Application Security Architect, Network Security Architect, and Identity and Access Management (IAM) Architect. These paths are useful if you want to become the go-to expert for a high-demand security area.
- Move laterally or upward: Experienced security architects may transition into cybersecurity consulting, risk management, enterprise architecture, product security leadership, or executive roles such as Chief Information Security Officer (CISO).
A common mistake is trying to move into architecture too early. Certifications can help, but employers usually want proof that you have solved complex security problems in production environments. Build a portfolio of architecture reviews, threat models, incident lessons learned, compliance projects, and secure design decisions.
Security architects are typically well compensated because they protect high-value systems and influence expensive technology decisions. Pay varies widely by experience, specialization, employer size, industry, city, and whether compensation includes bonuses, equity, or stock options.
The average annual salary ranges from $110,500 to $147,647, based on data from VelvetJobs and PayScale. Total compensation, including bonuses and stock options, can rise significantly, with some earning between $161,000 and $505,000 annually. Verified profiles project an average income of approximately $220,000 in 2025, especially for senior or specialized roles.
What affects security architect pay?
- Experience level: Professionals with over ten years of expertise or leadership titles such as chief architect often exceed $300,000 annually.
- Specialization: Cloud security, enterprise architecture, application security, and identity architecture can command higher compensation when the employer has complex systems or regulatory pressure.
- Location: Major tech and finance hubs such as San Francisco, Washington, DC, and New York often offer higher salaries, although cost of living and competition can also be higher.
- Education and certifications: A bachelor's degree is typically sufficient for many roles, but advanced degrees and cybersecurity certifications can strengthen your profile for senior positions.
- Compensation structure: Base salary is only one part of pay. Bonuses, stock options, retirement contributions, remote-work flexibility, and benefits can significantly change the value of an offer.
If you are changing careers or returning to school, flexible study options such as online college courses for seniors may help you build relevant knowledge while comparing cost, accreditation, transfer policies, and program outcomes.
There are few internships titled “security architect” because architecture is usually a senior function. Instead, look for internships that expose you to secure system design, cloud security, risk analysis, compliance, DevSecOps, security operations, or application security. These roles help you build the experience that later supports an architecture career.
- Vanguard's College to Corporate Internship: This program can provide exposure to secure software development, cloud environments, DevSecOps, mentorship, and agile methods within a major financial firm.
- Hewlett Packard Enterprise (HPE) Global Security Early Career Program: This program includes rotations in security operations, risk and compliance, and security field operations, with training in pipeline code security, API security, and AI/ML integration.
- Google Public Sector Internships: These internships may involve security architecture for cloud and on-premise systems that support government and education environments. They are especially relevant for students interested in protecting critical infrastructure and public-sector systems, including those exploring security architecture internships in India and similar markets.
- Healthcare, Education, and Nonprofit Internships: These settings can be valuable because they emphasize compliance, data privacy, limited budgets, and sensitive information. They also build communication and problem-solving skills that security architects need.
Internship titles worth searching
- Cybersecurity intern
- Security operations intern
- Cloud security intern
- Application security intern
- DevSecOps intern
- Risk and compliance intern
- Identity and access management intern
- Information security analyst intern
For students seeking cyber security internship opportunities in the United States, prioritize roles that provide hands-on work rather than observation only. Good signals include access to mentors, real security tooling, incident response exercises, cloud configuration review, threat modeling, audit evidence collection, or secure coding work. If you want to deepen your qualifications while gaining experience, fast masters programs may help you compare accelerated graduate options that fit your schedule and career goals.
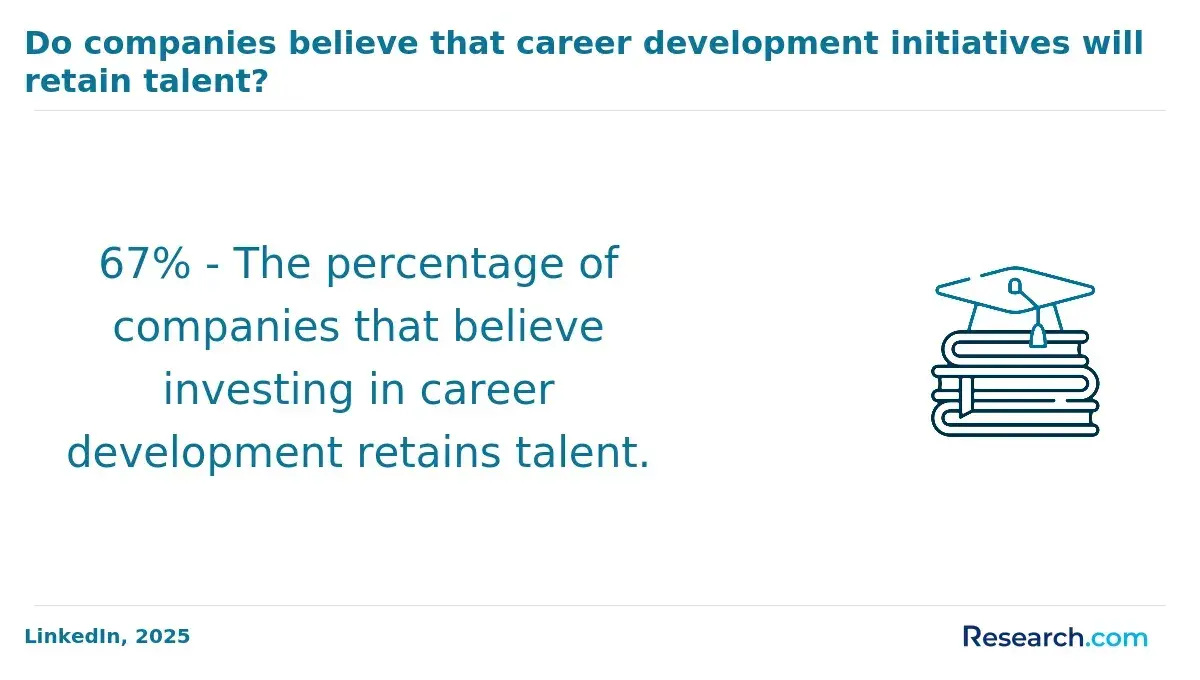
Advancing as a security architect means expanding your influence. Early in the role, you may review designs and recommend controls. At higher levels, you set standards, shape security strategy, guide investments, mentor teams, and influence executive decisions. Technical depth still matters, but leadership and business judgment become more important over time.
- Advanced Education: A master's degree in cybersecurity, information assurance, or a related field can strengthen your profile for senior roles, especially in large organizations and government agencies where advanced qualifications may be valued.
- Certifications: Credentials such as CISSP, CCSP, or ISSAP can demonstrate advanced knowledge. Cloud platform certifications in AWS, Azure, or GCP, along with training in AI and IoT security, can also help you stand out for specialized roles.
- Experience and Specialization: Security architect roles typically require 5 to 10 years of IT and cybersecurity experience. Specializing in cloud security, application security, identity management, or enterprise architecture can make your expertise more marketable.
- Networking and Mentorship: Professional groups, conferences, cybersecurity communities, and internal architecture forums can help you stay current and visible. Mentors can help you navigate promotion paths, while mentoring others demonstrates leadership readiness.
- Leadership and Strategic Capabilities: Roles such as Principal Security Architect or CISO require team leadership, project oversight, governance knowledge, budget awareness, and the ability to align security initiatives with organizational objectives.
Practical ways to show readiness for promotion
- Lead a cross-functional security architecture review for a major system or cloud migration.
- Create reusable security patterns that engineering teams can adopt.
- Document business risk clearly enough for executives to make funding decisions.
- Improve an audit, compliance, incident response, or vulnerability management process.
- Mentor junior analysts or engineers and help raise the security maturity of other teams.
Security architects work anywhere organizations need to protect data, systems, users, intellectual property, or critical operations. The role is common in large enterprises, regulated industries, technology companies, consulting firms, and public-sector agencies. Remote and hybrid work are increasingly common, but highly sensitive environments may still require on-site work or clearance-related constraints.
- Large corporations: Finance, healthcare, and technology companies such as JPMorgan Chase, Kaiser Permanente, and Google hire security architects to protect sensitive data, secure platforms, and meet regulatory obligations.
- Government agencies: Federal, state, and local agencies, including departments such as Homeland Security and Defense, rely on security architects to secure critical infrastructure, classified data, public services, and mission-critical systems.
- Technology companies: Employers ranging from Microsoft and Cisco to cybersecurity startups need architects to design secure products, platforms, cloud environments, and customer-facing services.
- Healthcare organizations: Hospital systems and healthcare companies, including Mayo Clinic and UnitedHealth Group, rely on security architects to protect patient data and support HIPAA compliance.
- Educational institutions: Universities and research centers use security architects to protect student records, intellectual property, research data, and campus networks. Students comparing affordable accredited online colleges no application fee should still examine cybersecurity curriculum quality, accreditation, and career support before enrolling.
Additional opportunities exist in consulting firms, nonprofit organizations, managed security service providers, and independent contracting. Consulting can offer variety and faster exposure to different environments, while in-house roles may provide deeper ownership of long-term architecture decisions. For those evaluating the best cities for security architects in the US, New York ranks highly because of its concentration of financial institutions and technology firms.
Security architecture is rewarding, but it is not a low-pressure career. You are often accountable for decisions that affect business continuity, regulatory exposure, customer trust, and incident response. The challenges are manageable, but they require resilience, credibility, and continuous learning.
- High workload and emotional strain: Security architects design and protect complex IT environments. Major incidents, urgent vulnerabilities, audits, and executive escalations can require work outside normal business hours.
- Competitive job market: Because this is a senior role, openings can be limited and highly selective. Employers prioritize candidates with proven experience in risk management, incident handling, impact evaluation, architecture review, and communication with executives.
- Rapid industry evolution: AI, cloud computing, software supply chain risks, identity threats, and changing regulations continually reshape the work. Architects must stay current with technical changes and regulatory demands such as GDPR and SEC breach disclosure regulations.
- Outsourcing and budget constraints: Some organizations outsource security functions or limit internal security budgets. This can reduce in-house development opportunities and force architects to justify investments with clear risk and business reasoning.
Common mistakes to avoid
- Designing controls that are technically strong but too expensive or impractical to operate.
- Ignoring user experience, which can lead employees to bypass security processes.
- Failing to document architecture decisions, assumptions, and accepted risks.
- Relying only on tools instead of understanding process, ownership, and accountability.
- Communicating in technical language when leadership needs a business-risk explanation.
To excel as a security architect, build depth in technology, credibility through experience, and influence through clear communication. The role rewards people who can see both the technical system and the business context around it.
- Build a strong foundation in networking, systems administration, cloud computing, and security principles. A bachelor's degree in computer science, cybersecurity, or a related field can support this foundation.
- Consider a master's degree in cybersecurity or information assurance if you want to pursue senior leadership roles, especially in organizations that value formal academic credentials.
- Develop expertise in secure network design, AWS, Azure, GCP, encryption, identity and access management, and secure software development lifecycles.
- Gain practical experience in roles such as security analyst, network engineer, or penetration tester. Seek work involving audits, threat modeling, vulnerability management, incident response, and architecture review.
- Earn industry-recognized certifications such as CISSP, CCSP, or cloud-specific credentials when they align with your career stage and target roles.
- Practice structured problem-solving. Security architects often work with incomplete information, competing priorities, and high-stakes decisions.
- Improve your writing and presentation skills. You will need to explain risk, trade-offs, and recommendations to engineers, executives, auditors, and legal teams.
- Stay current through security publications, conferences, vendor documentation, professional networks, and post-incident reports.
- Align security frameworks with business goals. The best architecture recommendations reduce risk without unnecessarily slowing the organization.
- Maintain strong ethical standards. Security architects handle sensitive information and influence decisions that affect employees, customers, and public trust.
How to stand out
Create evidence of your work. Document threat models, design reviews, control mappings, cloud security improvements, incident response lessons, and architecture standards you helped build. When interviewing, be ready to explain not only what you recommended, but why it was the right choice given cost, risk, compliance, and operational constraints.
Security architecture may be a good fit if you enjoy solving complex technical problems, thinking several steps ahead, and helping organizations make safer decisions. It is less ideal if you want a narrow technical role with little stakeholder communication or a predictable work environment with few urgent issues.
- Inquisitive and Analytical Mindset: Strong security architects like investigating how systems work, how they can fail, and how attackers might exploit weak points. Critical thinking is one of the most important skills needed to become a security architect.
- Collaborative and Socially Responsible: The role is fundamentally protective. You need to care about safeguarding users, customers, employees, and organizations while working fairly with teams that may have competing priorities.
- Detail-Oriented and Composed: Architecture decisions often involve complex dependencies and high-pressure situations. Persistence, accuracy, and calm judgment matter.
- Comfort with Ongoing Learning: Threats, platforms, and regulations change constantly. If you prefer stability and fixed routines, this career may feel exhausting.
- Leadership and Communication: You should be comfortable guiding cross-functional teams and translating complex technical ideas for nontechnical audiences.
- Long-Term Impact and Career Stability: If you want intellectually challenging work with meaningful organizational impact, security architecture can be a strong long-term career path.
If you are asking, “Is security architect a good career for me?”, compare the role against your strengths, tolerance for pressure, and interest in both technology and business risk. A dual post graduate degree may be worth exploring if you want to combine cybersecurity with another field such as business, law, data science, or public policy.
What Professionals Who Work as a Security Architect Say About Their Careers
- : "Working as a security architect has provided me with unparalleled job stability and a highly competitive salary. The demand for skilled professionals in this role is consistently growing, making it a secure and rewarding career choice. I feel confident knowing my expertise is valued across industries. — Aryan"
- : "The role of a security architect challenges me every day to innovate and adapt to emerging threats. This career offers unique opportunities to work on complex systems and collaborate with diverse teams, which keeps the work engaging and fulfilling. It's a constant learning journey that sharpens both my technical and strategic skills. — Jireh"
- : "Choosing to become a security architect has been pivotal in my professional growth. The continuous education programs and certifications available have allowed me to advance steadily, opening doors to leadership roles within cybersecurity. It's a career path that truly supports long-term development and impact. — Aziel"
Other Things You Should Know About Becoming a Security Architect
The CISSP from (ISC)² is the most common baseline, and the ISSAP concentration is a strong security-architecture credential. Many employers also value CCSP for cloud work and SABSA Foundation for enterprise architecture, with several senior roles asking for at least 5 years of security experience.
Continuing education is crucial for security architects due to the constantly evolving nature of cybersecurity threats and technologies. Staying current with new security protocols, software developments, and emerging cyber risks ensures that security architectures remain robust. Many professionals pursue ongoing certifications, attend industry conferences, and participate in training programs to maintain their expertise.
In 2027, the demand for security architects continues to grow as cybersecurity threats evolve. Organizations prioritize securing their digital assets, creating ample opportunities for professionals in this field. The cybersecurity industry expects robust growth throughout the decade, with security architects playing a crucial role.
- How to Become a Security Architect | Education and Experience https://www.cyberdegrees.org/careers/security-architect/how-to-become/
- How to Be a Security Architect | Career & Certification Guide https://destcert.com/resources/how-to-be-a-security-architect/
- How to Become a Security Architect in 2025 - GeeksforGeeks https://www.geeksforgeeks.org/blogs/how-to-become-a-security-architect/
- How to Become a Security Architect https://cybersecurityguide.org/careers/security-architect/
- The role of Security Architect | Michael Page Poland https://www.michaelpage.pl/en/advice/profession/information-technology/role-security-architect
- Top 10 Skills for Career Success as a Cloud Security Architect https://www.eccu.edu/blog/key-skills-every-cloud-security-architect-should-master-for-career-success/
- Considerations for Fortifying an Enterprise Security Architecture | CISO Collective https://www.fortinet.com/blog/ciso-collective/what-cisos-need-to-know-about-their-security-architects-trends-and-challenges
- Common Challenges Security Architects Face in 2025 https://www.infosectrain.com/blog/common-challenges-security-architects-face-in-2025/
- How to Become a Security Architect https://www.wgu.edu/career-guide/information-technology/security-architect-career.html