2027 Data Governance Councils vs IT Steering Committees

Co-Founder and Chief Data Scientist
A healthcare organization can approve a new analytics platform and still disagree about which patient data it may use, who can access it, or how its results should be interpreted. Those decisions belong to different governance bodies. This guide compares data governance councils with IT steering committees, shows where their work intersects, and helps healthcare professionals choose relevant education or credentials. It is especially useful if you are moving from clinical, administrative, information management, or technology work toward governance leadership - and want to know whether a degree is necessary for your next step.
Key Things You Should Know
- A data governance council sets rules and accountability for data; an IT steering committee prioritizes technology investments, resources, and implementation risks. Major projects often need decisions from both.
- Neither body is a substitute for the organization's privacy officer, security officer, legal counsel, or executive accountability under applicable law.
- A relevant degree can develop leadership skills, but governance roles also require demonstrated healthcare experience. For context, the May 2025 median wage across all US management occupations was $126,520 - not a healthcare data governance salary.
What is the difference between data governance councils and IT steering committees?
A data governance council decides how an organization defines, uses, protects, and takes responsibility for data. An IT steering committee decides which technology initiatives to fund and prioritize, and how to manage their delivery. Membership varies, but councils typically bring together operational data owners, stewards, privacy, compliance, clinical, and analytics representatives. Steering committees commonly include executives from IT, finance, operations, clinical leadership, and risk management.
The distinction is easiest to see when a hospital proposes a new reporting platform. The council may settle patient-matching standards, definitions of quality measures, permitted uses, and ownership of disputed records. The steering committee may approve the budget, select between competing projects, assess vendor and implementation risk, and monitor whether deployment meets organizational goals.
This comparison shows which body should lead a decision - and when the other must be consulted.
| Decision | Data governance council | IT steering committee |
| Primary question | Are data trustworthy, appropriately used, and clearly owned? | Is this technology investment the right priority and being delivered responsibly? |
| Typical outputs | Definitions, stewardship assignments, access principles, and data-quality escalation | Portfolio priorities, funding recommendations, implementation oversight, and project escalation |
| Point of overlap | A system change affecting data access, interoperability, reporting, or retention needs coordinated decisions. |
Neither committee should quietly override the other's remit. A project charter can name who approves the investment, who approves data-use standards, and where unresolved conflicts go. Professionals seeking a broader view of that cross-functional work can examine online MHA options for healthcare administration study, rather than assuming technology coursework alone covers it.
How do data governance councils support healthcare administration and compliance?
A council turns broad obligations into workable organizational decisions: who owns a dataset, which definition applies across departments, how data-quality problems are corrected, and when a proposed use needs privacy or legal review. In healthcare, inconsistent patient identities or conflicting definitions can affect care coordination, reporting, reimbursement, and management decisions.
The council can establish an escalation route for disputed data, but it should not declare a use "HIPAA compliant" without appropriate review. HIPAA privacy and security requirements, state law, contracts, and - where applicable - rules governing substance-use-disorder records can affect a proposed use differently. Privacy and security specialists interpret their respective obligations; the council helps put approved policies into practice and track exceptions.
For someone entering healthcare from another industry, this is an important boundary: general data-management experience transfers, but healthcare workflows and regulatory context must be learned. An applicant exploring graduate study without prior sector experience can review understanding MHA admission routes for non-healthcare graduates and seek a supervised healthcare data project alongside coursework.
What does an IT steering committee do in a healthcare organization?
An IT steering committee connects technology spending to organizational priorities. It may weigh an electronic health record upgrade against cybersecurity work, interoperability improvements, or a new analytics tool; review proposed budgets and dependencies; and escalate projects that are over budget or no longer meet their intended need. It should obtain clinical, privacy, security, procurement, and data-governance input when a decision affects those functions.
For example, approving an AI-assisted documentation pilot is not the same as approving unrestricted use of patient data. The steering committee can assess the investment and rollout; the data council and designated experts can evaluate data definitions, access, permitted uses, and monitoring. Clear handoffs prevent a vendor contract from becoming the organization's de facto data policy.
An MBA can help an experienced healthcare or IT professional assess budgets, organizational change, and competing investments, but it does not replace technical or regulatory expertise. Those comparing a shorter management route can examine accelerated online MBA programs in healthcare management and verify that the curriculum actually addresses healthcare information systems.
The right degree depends on what the professional already knows. A bachelor's degree in healthcare administration can build a foundation in operations, finance, and health systems. An MHA generally offers more focused preparation for leading healthcare organizations; an MBA emphasizes broader management and may offer healthcare coursework. A health informatics or health information management program may be more direct for someone whose main gap is data, systems, or information practice. Degree names alone do not establish how much governance content a program contains.
This table compares the educational emphasis - not guaranteed access to a committee seat or leadership job.
| Path | Potential fit | Gap to check |
| Healthcare administration bachelor's | Building sector and management foundations | Depth of data governance and applied experience |
| MHA | Healthcare operations and cross-functional leadership | Technical information-systems coursework |
| MBA with healthcare coursework | Budgeting, strategy, and enterprise decisions | Whether healthcare data and compliance are substantively covered |
| Health informatics or information management degree | Data and information-workflow specialization | Executive finance and portfolio leadership |
For a community-college student, healthcare administration degree completion after community college may be a more sensible first step than planning immediately for graduate school. For an experienced analyst or manager, a targeted course and a governance assignment may close a narrower skills gap at lower cost than another degree.
Look beyond a program's concentration label to its course descriptions and applied work. Relevant study may include health information systems, data quality and stewardship, healthcare analytics, privacy and security governance, healthcare law and ethics, operations, managerial finance, and organizational change. A general MBA analytics elective may teach leaders to use dashboards without teaching patient-record standards or healthcare data-access decisions.
A particularly useful assignment asks students to resolve a realistic conflict - for example, a proposed dashboard that combines clinical and billing data. It should require an accountable data owner, a documented use case, privacy and security review, quality checks, and a plan for escalating unresolved issues. Ask whether projects use healthcare cases and whether students receive feedback from practitioners; do not assume those features are available in every online program.
Time-sensitive applicants comparing choosing a 12-month health administration master's pathway should check which relevant courses fit into the accelerated sequence, rather than judging depth by completion time alone.
Yes, if the program teaches the needed material and lets students apply it to real decisions. Online delivery can accommodate employment, but it does not guarantee flexible deadlines, asynchronous classes, access to healthcare projects, or the same recruiting opportunities as a campus program. Working professionals should check live-session times, group-project expectations, required visits, and whether employer data can be used safely in coursework.
A useful selection test is whether you can graduate with a defensible example of governance work: a data-definition policy, stewardship map, access-decision process, or evaluated technology proposal. If a program cannot support that work, an employer-sponsored project paired with shorter training may be more valuable.
Applicants who need frequent entry points can compare online health administration degree start schedules, while separately confirming course availability and the pace needed to finish.
First verify that the institution holds recognized institutional accreditation and that the status applies to the school awarding the degree. Then check program-specific accreditation where it matters to your goal: CAHME accredits eligible graduate healthcare management programs, while business-school and health-informatics programs may be evaluated under different specialized frameworks. An institution's accreditation does not mean every program has specialized accreditation; the absence of a particular specialized credential does not, by itself, make a degree invalid.
Use the accreditor's current directory and the school's program page to confirm the exact degree and delivery option. This matters especially when comparing advanced credentials: a doctorate's title, institutional accreditation, and any applicable program recognition are separate questions. Readers considering that longer route can review shorter healthcare administration doctorate options and requirements, but should not assume a doctorate is required to serve on either committee.
Requirements vary by degree and school. Bachelor's applicants should check transfer-credit rules and general admission standards. Graduate applicants commonly need a bachelor's degree and application materials documenting academic and professional preparation; work-experience expectations, prerequisite courses, tests, and waivers are program-specific. A nonbusiness or non-healthcare bachelor's degree is not automatically disqualifying.
Published tuition is only one part of the decision. Ask each school for the credits required, tuition basis, mandatory fees, books or software, any travel, and the effect of part-time enrollment. Also ask whether previous credits transfer, whether your employer will reimburse approved courses, and whether an accelerated schedule would require reducing paid work. Without those program- and student-specific inputs, a credible total price or completion date cannot be stated.
When you compare accelerated healthcare administration degrees, confirm both the advertised pace and the course sequence you can actually take. A faster program is not necessarily cheaper if fees, lost work time, or an unmanageable course load change its effective cost.
Relevant paths include data steward, health information manager, privacy or compliance specialist, healthcare analytics manager, health IT project or portfolio manager, and - after substantial experience - director-level governance or technology leadership. A clinician may bring workflow knowledge; an analyst may bring data-quality skills; an IT manager may bring implementation experience. Each may still need exposure to the other functions before leading an enterprise committee.
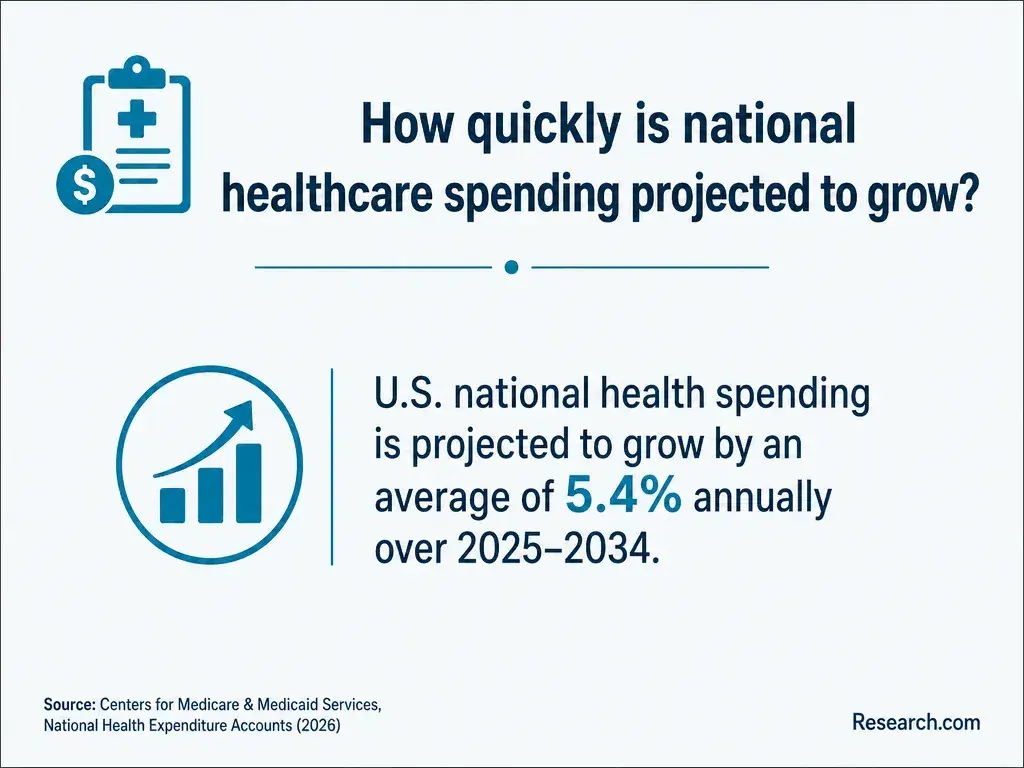
The US Bureau of Labor Statistics reports a $126,520 median annual wage for management occupations in May 2025 and projects about 1.1 million openings per year across that broad group from 2025 to 2035. Those figures describe management occupations collectively, not healthcare governance positions, MBA graduates, or a promised salary. Job title, location, employer, and prior responsibility matter more when evaluating a specific offer.
Before choosing a degree for its earning potential, review actual job postings for the role you want and distinguish required experience from preferred credentials. You can explore higher-paying healthcare administration careers for broader role context, then compare that context with local openings and your current qualifications.
Which certifications strengthen healthcare data governance and IT committee careers?
Choose a credential for the work you want to do, not merely for its initials. Health information management credentials from AHIMA can be relevant to information and records leadership; privacy credentials from IAPP may support privacy-focused work; ISACA credentials can be useful in IT governance, risk, or audit roles; and project-management credentials can support technology delivery. Eligibility, examinations, continuing education, and employer recognition differ, so verify the current rules with the issuing body.
Certifications demonstrate defined knowledge or experience; they do not grant authority to approve a hospital's data uses or technology budget. If you already have a degree and relevant experience, a targeted credential plus an opportunity to document committee work may be more direct than another degree. For a senior professional considering doctoral study instead, compare the cost and career context of healthcare administration doctorates against the actual requirements of the desired role.
Other Things You Should Know About Healthcare Administration
No. A formal council is an organizational governance choice, not a universal HIPAA requirement. The organization still must meet applicable legal obligations regardless of its committee structure.
Use a documented escalation path to an accountable executive or established governing body. Record the decision, its rationale, and any conditions rather than allowing a project to proceed through an unclear approval.
HIPAA generally gives individuals a right to request amendment of protected health information in a designated record set. The covered entity reviews the request under applicable rules; a governance council should not replace that process.
Look for documented decisions, named owners, resolved data-quality issues, tracked exceptions, and evidence that approved technology projects follow the agreed data rules. Meeting frequency alone is not a useful outcome measure.
- Data Governance and Stewardship - PMC - NIH https://pmc.ncbi.nlm.nih.gov/articles/PMC2965885/
- Data governance and management | gsa.gov https://coe.gsa.gov/coe/ai-guide-for-government/data-governance-management/
- Roles and Responsibilities - UNM Data Governance https://data.unm.edu/roles-and-responsibilities.html
- Data Governance Structure - Institutional Research https://www.ir.iastate.edu/data-governance/structure
- Data Governance Steering Committee Procedures | University Data Governance https://datagovernance.ecu.edu/dgsc-procedures/
- Data Governance Council - an overview https://www.sciencedirect.com/topics/computer-science/data-governance-council
- Data Governance Policy | Brandeis University https://www.brandeis.edu/its/policies/data-governance-policy.html
- Data Governance Committee: Operating Model - Princeton OIT https://oit.princeton.edu/initiatives/data-governance/data-governance-committee-operating-model
- What is Data Governance? Definition & Benefits - Boomi https://boomi.com/blog/data-governance-complete-guide/
- Data Owners vs Stewards vs Custodians: Roles Explained | Censinet https://censinet.com/perspectives/data-owners-vs-stewards-vs-custodians-roles-explained