2027 Security Management Careers: Skills, Education, Salary & Job Outlook

Co-Founder and Chief Data Scientist
Security management is for people who want to protect organizations from physical, digital, operational, and human risks—not just respond after something goes wrong. The career can lead to roles in corporate security, public safety, healthcare, government, critical infrastructure, cybersecurity-adjacent operations, and executive risk leadership.
The decision is not simply whether the field sounds interesting. You need to know what security management specialists actually do, which credentials matter, how much experience employers expect, and whether the work environment fits your tolerance for pressure, accountability, and occasional irregular hours. Earning potential is strong, with a median annual figure of $111,790, but advancement usually depends on a mix of education, field experience, leadership ability, and certifications such as CPP, CSM, CISSP, or PSP.
This guide explains the role in practical terms: daily responsibilities, required skills, education and certification paths, salary potential, job outlook, work settings, pros and cons, advancement options, and related careers to consider before committing to this path.
Key Things You Should Know About Security Management Careers
- The typical earning potential for a security management specialist is around $111,790 annually, with most professionals earning between $98,500 and $132,000.
- This field remains stable and growing, supported by strong demand and active job postings, even though exact long-term projections for this specific role are not published.
- Most employers require a bachelor's degree in criminal justice, security management, or business, though significant industry experience can sometimes substitute for formal education.
- Success depends on skills such as risk assessment, emergency response planning, incident investigation, leadership, communication, and expertise with security technologies.
- Career advancement typically moves from security officer or analyst to specialist or manager roles, with opportunities to become a security director, chief security officer, or regional security manager as experience builds.
What do security management specialists do?
Security management specialists design, coordinate, and improve the systems that protect an organization’s people, property, information, facilities, and operations. Their work sits at the intersection of risk management, emergency planning, physical security, cybersecurity awareness, compliance, investigations, and leadership.
Unlike frontline security officers who may focus primarily on patrol, screening, monitoring, or incident response, security management specialists usually take a broader planning and coordination role. They identify vulnerabilities, create policies, supervise security procedures, recommend technology upgrades, train employees, document incidents, and help leaders make informed decisions about risk.
A day in the life of security management specialists
A typical day may include reviewing incident reports, checking access control data, meeting with facilities or IT staff, updating emergency procedures, evaluating vendor performance, conducting a site inspection, or briefing managers on a security concern. In higher-risk environments, the work may also involve coordinating investigations, preparing for audits, managing crisis response drills, or helping an organization recover after a breach, theft, workplace threat, or operational disruption.
The best security management specialists are proactive. Their success is often measured by what does not happen: fewer preventable incidents, faster response times, better compliance, safer facilities, and employees who understand how to report and avoid security risks.
What are the key responsibilities of security management specialists?
Security management specialists are responsible for turning risk assessments into practical controls. Their duties vary by employer, but most roles combine planning, monitoring, training, documentation, and incident response.
- Assess risks and vulnerabilities: Conduct security audits, site inspections, threat assessments, and procedural reviews to find weak points before they become incidents.
- Create and update security policies: Develop procedures for access control, visitor management, emergency response, incident reporting, surveillance use, workplace violence prevention, and asset protection.
- Monitor security systems: Oversee surveillance, alarms, access control platforms, visitor logs, and related tools, then respond when systems show suspicious or unauthorized activity.
- Coordinate incident response: Help manage security breaches, thefts, threats, emergencies, policy violations, and investigations while communicating with internal teams and external partners.
- Train employees and security staff: Teach people how to follow security protocols, use equipment correctly, report suspicious behavior, and respond during emergencies.
- Document findings and actions: Prepare incident reports, audit records, investigation summaries, compliance documentation, and recommendations for leadership or legal review.
- Recommend security improvements: Evaluate procedures, staffing models, vendor services, and technology upgrades to strengthen protection without creating unnecessary operational barriers.
The most challenging vs. the most rewarding tasks
The most challenging part of the job is often making decisions during an active incident. A specialist may need to act quickly with incomplete information, coordinate multiple teams, preserve evidence, protect people, and limit operational disruption at the same time.
The most rewarding work is usually preventive. When a new access control process, emergency plan, training program, or risk assessment prevents a serious incident, the value of the role becomes clear. For students who want a faster route into a bachelor’s-level pathway, an accelerated bachelor's degree online may be worth comparing with traditional programs, especially if they already have work experience or transfer credits.
What are the key skills for security management specialists?
Security management specialists need both technical judgment and people skills. The role is not only about knowing security tools; it also requires explaining risk, gaining cooperation, leading during stressful events, and making policies that employees can realistically follow.
Key hard skills
- Risk assessment and vulnerability management: Identifying threats, ranking risks, evaluating controls, and recommending improvements based on likelihood and impact.
- Incident response: Coordinating containment, communication, documentation, escalation, and recovery after security events.
- Compliance and security frameworks: Understanding standards and frameworks such as NIST and ISO 27001 when they apply to organizational security practices.
- Access control and identity management: Helping prevent unauthorized access through badge systems, permissions, physical controls, and tools such as Okta or Active Directory.
- Security technology evaluation: Reviewing surveillance, alarm, monitoring, and reporting systems to determine whether they support the organization’s actual risk profile.
- Report writing and documentation: Producing clear records that can support audits, investigations, insurance claims, internal reviews, or legal processes.
Essential soft skills
- Analytical thinking: Interpreting incident patterns, system alerts, employee reports, and environmental risks without jumping to unsupported conclusions.
- Communication: Explaining security requirements to executives, employees, contractors, vendors, and frontline staff in plain language.
- Attention to detail: Noticing small gaps, inconsistent procedures, incomplete records, or unusual activity that could signal a larger issue.
- Problem-solving: Creating workable solutions when ideal security controls are too expensive, disruptive, or difficult to implement immediately.
- Professional judgment: Balancing safety, privacy, compliance, cost, and operational continuity.
The overlooked skill that separates strong specialists from average ones
Leadership during uncertainty is one of the most valuable skills in this field. A specialist who can keep people calm, assign roles, communicate clearly, and escalate issues appropriately can reduce confusion during a breach, workplace threat, emergency, or major systems failure.
For example, during a sudden cyberattack or physical security incident, a strong security management specialist does more than follow a checklist. They coordinate response teams, stabilize operations, document decisions, and help leaders understand the immediate risks. That combination of technical awareness and crisis leadership is often what separates a capable practitioner from a future manager or director.
Students still comparing academic options should choose a program that builds writing, analysis, technology awareness, and leadership—not just a narrow set of security terms. If ease and flexibility are major concerns, reviewing the easiest degree course options can help, but the better long-term choice is the program that aligns with the type of security role you want.
Security management careers usually develop in stages. Most professionals do not begin as managers; they build credibility through education, security operations experience, law enforcement or military experience, internships, technical training, or related risk and compliance work.
- Build foundational education: Start with a relevant postsecondary program in security management, criminal justice, homeland security, cybersecurity, emergency management, or a closely related field. Coursework should help you understand risk, law, ethics, investigations, technology, and organizational behavior.
- Gain practical experience: Look for internships, campus safety roles, security operations positions, emergency preparedness work, loss prevention roles, military experience, law enforcement experience, or entry-level analyst/coordinator positions. Employers value candidates who have seen how security procedures work in real settings.
- Document your accomplishments: Keep records of projects you supported, systems you used, audits you assisted with, reports you wrote, trainings you delivered, and incidents you helped manage. These details make your resume stronger than a generic list of duties.
- Earn professional credentials: Add certifications when they match your target role. Some credentials are better for physical security, some for cyber-focused work, and others for management or program leadership.
- Move into supervisory or specialized roles: With experience, pursue roles such as security coordinator, security analyst, security supervisor, security manager, risk analyst, physical security specialist, or emergency management specialist.
- Continue professional development: Security threats, technology, compliance expectations, and workplace risks change quickly. Advancement depends on staying current and proving that you can lead people, improve systems, and communicate risk to decision-makers.
A strong entry strategy is to choose a target environment early. Corporate headquarters, hospitals, schools, government facilities, logistics operations, data centers, and critical infrastructure employers may all use security management skills, but they may prioritize different credentials and experience.
The primary qualifications for becoming a security management specialist include a bachelor's degree in security management, criminal justice, homeland security, cybersecurity, or emergency management. Common degree titles include Bachelor of Science in Security Management, Criminal Justice, or a closely related field.
Employers may also consider candidates with strong military, law enforcement, emergency management, security operations, or IT security backgrounds, especially when that experience includes leadership, investigations, compliance, or risk assessment. However, a degree can make it easier to qualify for management-track roles, especially in larger organizations.
Common education and credential options
| Pathway | Best fit | What to consider |
| Bachelor's degree in security management, criminal justice, homeland security, cybersecurity, or emergency management | Students seeking entry into specialist, coordinator, analyst, or management-track roles | Look for coursework in risk assessment, emergency planning, law, investigations, leadership, and technology. |
| Certified Protection Professional (CPP) issued by ASIS International | Professionals pursuing broader protection management and leadership credibility | Best suited for candidates with meaningful field experience rather than absolute beginners. |
| Certified Security Manager (CSM) from CorpSecurity | Professionals who want a management-focused security credential | Can strengthen advancement prospects when paired with practical experience. |
| Certified Information Systems Security Professional (CISSP) | Security professionals moving toward cybersecurity leadership or information security management | Most valuable when the target role includes digital security, governance, or enterprise risk. |
| Physical Security Professional (PSP) | Professionals focused on facilities, access control, surveillance, and physical protection systems | Useful for roles centered on site security, infrastructure, and physical security design. |
On-the-job training often includes internships during undergraduate study, supervised work under senior security personnel, and gradual exposure to audits, incident response, access control systems, reporting, emergency drills, and vendor coordination. Although there are no standardized residency programs, many employers require between one to five years of relevant work experience in security operations, law enforcement, or the military before promotion to specialist or manager roles.
Are advanced degrees or niche certifications worth the investment?
Advanced credentials such as a Master of Science in Security Management, Homeland Security, or an MBA with a security focus can support movement into leadership roles and specialized positions. Certifications like the Certified Information Systems Security Professional (CISSP) or Physical Security Professional (PSP) further signal expertise, often leading to higher salaries ranging from $75,000 to $146,000 annually.
The trade-off is cost and time. Tuition fees can exceed $50,000, and certification preparation may require months of study plus qualifying experience. Advanced degrees and senior credentials are usually unnecessary for entry-level roles, so they make the most sense when they clearly support a target outcome: director-level advancement, cybersecurity leadership, physical security specialization, consulting, teaching, or executive risk roles.
Before enrolling, compare the credential against job postings you actually want. If employers repeatedly request a specific certification or graduate degree, the investment may be easier to justify. If your goal is academic leadership, research, or senior consulting, an affordable PhD may be relevant, but it should be evaluated against the opportunity cost and your long-term career plan.
The security management salary in 2025 for a security management specialist has a median annual figure of $111,790. This is a midpoint figure, not a guaranteed starting salary. Actual pay depends heavily on the employer, location, industry, scope of responsibility, certifications, and years of experience.
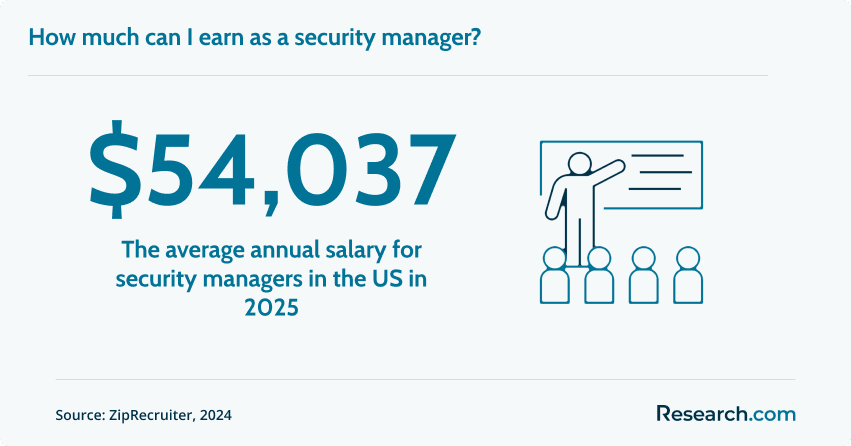
The security manager earning potential over time spans a wide range, from about $98,500 at the entry level to $145,000 for those with senior experience and advanced skills. Professionals who supervise teams, manage enterprise-wide programs, combine physical and cyber risk knowledge, or work in high-risk and highly regulated environments may have stronger earning potential than those in narrower operational roles.
What affects salary the most?
- Experience level: Entry-level specialists typically earn less than managers, directors, and senior risk leaders with a record of successful programs.
- Industry: Government, healthcare, corporate security, critical infrastructure, finance, technology, and defense-related employers may value different security expertise.
- Location: Metropolitan areas and certain states tend to offer higher pay, though cost of living can reduce the real advantage.
- Specialization: Cybersecurity, physical security systems, executive protection, intelligence analysis, compliance, and emergency management can affect compensation.
- Credentials: Certifications such as CPP, CSM, CISSP, or PSP may improve competitiveness when they match the job’s responsibilities.
- Leadership scope: Managing budgets, vendors, teams, audits, crisis response, and enterprise policy usually supports higher compensation than purely task-based roles.
When evaluating a job offer, look beyond salary alone. On-call expectations, travel, overnight incident response, clearance requirements, retirement benefits, tuition support, certification reimbursement, and promotion pathways can significantly change the value of a role.
The projected 10-year growth rate for security management specialists is approximately 5.9%, which is slightly below the average growth for all occupations in the United States. That points to moderate, steady opportunity rather than explosive growth. Candidates who combine security operations experience with technology awareness, compliance knowledge, and leadership skills are likely to be more competitive.
The key factors shaping the future outlook
- Cyber and technology risk: As digital threats evolve, including AI-driven attacks and increased automation, organizations need security professionals who understand how digital and physical risks overlap.
- Workplace safety and physical security concerns: Employers continue to need specialists who can assess facilities, improve access controls, prepare emergency plans, and reduce preventable harm.
- Geopolitical and economic instability: Global tensions, regional conflicts, supply chain vulnerabilities, and infrastructure concerns can increase demand for professionals who understand threat assessment and continuity planning.
- Regulatory and compliance pressure: Organizations face growing legal and operational expectations related to data privacy, infrastructure protection, reporting, and safety procedures.
- Hybrid security environments: Many employers now need leaders who can coordinate across security, IT, HR, facilities, legal, compliance, and executive teams.
The outlook is strongest for professionals who do not treat security as a single narrow function. If your goal is senior leadership, build evidence that you can manage programs, explain risk to executives, and improve measurable outcomes. For professionals considering advanced study to deepen expertise, a 1 year online doctorate may be worth reviewing, but only if it fits your career goals and the expectations of your target employers.
The security management workplace culture and environment usually combines office-based planning with on-site evaluation and direct coordination. Most security management specialists spend much of their time indoors in environmentally controlled offices, but many also visit facilities, checkpoints, control rooms, parking areas, restricted spaces, or worksites to verify that policies are working in practice.
Some work on-site at government facilities, corporate offices, or hospitals—industries that employ 27%, 13%, and 9% of professionals respectively. The role often requires collaboration with security officers, executives, IT teams, HR, legal counsel, facilities managers, contractors, emergency responders, and employees across departments.
Schedule and flexibility
The typical work schedule is primarily full-time during standard business hours. However, security issues do not always happen on schedule. Specialists may occasionally be on-call or work evenings, weekends, holidays, or extended hours during emergencies, investigations, major events, audits, technology rollouts, or special projects.
Some planning, reporting, policy writing, training design, and analysis can be done remotely. Fully remote security management positions are uncommon because many responsibilities require physical presence, including site inspections, access control reviews, emergency drills, incident response, and coordination with on-site teams.
Workplace fit
This environment may suit you if you are comfortable switching between desk-based analysis and field-based problem-solving. It may be less appealing if you need predictable hours at all times, want fully remote work, or prefer jobs with low exposure to emergencies, conflict, or compliance enforcement.
Security management can be meaningful and financially rewarding, but it is not a low-pressure career. The same responsibility that makes the work important can also make it stressful. Before choosing this path, weigh the benefits against the realities of incident response, accountability, and ongoing professional development.
| Pros | Cons |
| Work has visible purpose because it protects people, assets, facilities, and sensitive information. | High-pressure incidents may require fast decisions with incomplete information. |
| The role offers variety, including planning, investigations, training, technology review, and emergency preparedness. | Some positions require on-call work, evenings, weekends, or urgent response outside normal hours. |
| Professionals can advance into management, consulting, cybersecurity, physical security, risk, or executive leadership. | Security threats and technologies change quickly, requiring continuous learning. |
| The work builds transferable skills in leadership, compliance, risk assessment, communication, and operations. | Enforcing policies can create conflict when employees or departments resist security procedures. |
| Earning potential can be strong for experienced specialists and managers. | Entry-level candidates may need several years of experience before qualifying for higher-paying management roles. |
Who is this career best for?
This career is a strong fit for people who are observant, calm under pressure, organized, ethical, and willing to hold others accountable. It is also well suited to professionals who like practical problem-solving and want a role that blends operations, people, technology, and policy.
If you are a working adult preparing for this field, flexibility and cost may matter as much as program title. Comparing the best affordable online schools for working adults can help you find a pathway that supports career change or advancement without pausing your current job.
Security management advancement usually follows one of two routes: broader leadership responsibility or deeper specialization. Some professionals move toward director, chief security officer, or executive risk roles. Others become experts in cybersecurity, physical security systems, intelligence, emergency management, compliance, or program management.
Advancement in leadership roles
- Security Specialist/Analyst/Coordinator: Build foundational experience by supporting daily security functions, reviewing incidents, assisting with audits, maintaining documentation, and helping implement protocols. This level is ideal for those with 0-3 years in security management.
- Security Manager/Director: Oversee teams, budgets, vendors, procedures, training programs, and security operations. These roles often involve policy development, departmental strategy, and cross-functional coordination, and are suited for professionals with 7+ years of experience.
- Executive Security Leadership (CSO/CISO/VP): Shape organizational security at the highest level by setting strategy, leading enterprise-wide programs, advising senior executives, and connecting security decisions to business risk. These positions generally require 11+ years of leadership experience.
Specialization opportunities
- Cybersecurity and IT Security: Protect digital environments through policy, incident response, vulnerability management, cloud security, or penetration testing. Credentials such as CISSP and CompTIA Security+ may be useful depending on the role.
- Physical Security and Protection Management: Focus on facilities, access control, surveillance, executive protection, threat assessment, and emergency procedures. Credentials such as ASIS CPP or PSP can support credibility.
- Intelligence and Risk Management: Analyze threats, assess organizational exposure, and help leaders prepare for security, geopolitical, operational, or infrastructure risks. Certifications like ASIS APP and CPP may be relevant.
- Security Project and Program Management: Lead security implementations, technology upgrades, vendor transitions, emergency preparedness projects, and multi-site programs. Credentials such as SIA CSPM or PMP may help demonstrate project leadership.
How to position yourself for promotion
Promotion is easier when you can show measurable contributions. Track improvements such as reduced incident response time, better audit results, completed training initiatives, successful technology deployments, improved reporting processes, or stronger compliance outcomes. Leadership roles require evidence that you can manage people, communicate with executives, and make security practical for the organization.
If security management interests you but you are not sure it is the right fit, compare it with adjacent careers. Many use similar skills—risk assessment, investigation, compliance, communication, technology awareness, and emergency planning—but differ in work setting, technical depth, and daily responsibilities.
- Cybersecurity Manager / Cybersecurity Specialist: A stronger fit if you prefer digital systems, vulnerability management, security architecture, incident response, and technology strategy.
- Information Security Analyst: A more hands-on technical path focused on monitoring systems, analyzing threats, responding to alerts, and helping protect networks and data.
- Risk Management Professional: A broader business-focused option that involves identifying, measuring, and reducing operational, financial, compliance, physical, or cyber risks.
- Protection / Asset Protection Manager: A practical, operations-focused career centered on preventing loss, protecting people and property, improving procedures, and managing emergency plans.
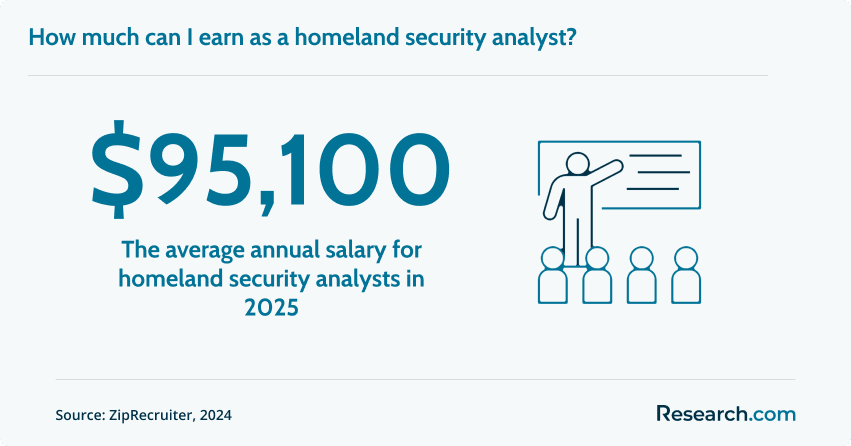
- Homeland Security Professional: A public-service-oriented path involving critical infrastructure, emergency preparedness, intelligence coordination, public safety, and interagency collaboration.
Choose security management if you want a broad role that connects people, facilities, information, technology, and organizational risk. Choose a more specialized path if you already know you want to focus mainly on cyber defense, investigations, emergency management, physical protection systems, or enterprise risk strategy.
- Andy: "I find the most meaningful part of my role as a security management specialist is the direct impact I have on people's lives-knowing that the safety protocols I develop and enforce protect not only physical assets but also the well-being of my colleagues. Being the person who solves problems quickly when threats arise gives me a deep sense of pride. It's rewarding to hear from employees that they feel secure at work because of the systems I maintain. This career lets me contribute to something bigger than myself, which keeps me motivated every day."
- Tom: "Transitioning from a background in law enforcement to corporate security was initially overwhelming, especially when adapting to new digital monitoring systems and corporate procedures. I remember feeling frustrated by how much I didn't know about the technologies that are now crucial for daily operations. That challenge forced me to commit to extensive training and seek advice from mentors within the company. Over time, bridging that gap not only improved my confidence but also helped me lead my team more effectively under evolving circumstances."
- Mary: "One of the most rewarding experiences I've had was when I took charge of reorganizing my unit's duties during a critical contract period. The recognition I received from both my superiors and clients after we pulled through successfully boosted my confidence and led to two promotions within a year. Supporting my colleagues and watching them grow because of the structures I helped implement gave me lasting satisfaction. Being acknowledged for leadership and tangible results keeps me passionate about this role even during tough times."
Key Findings
Other Things You Should Know About Security Management Careers
Employers often value ASIS International’s Certified Protection Professional (CPP) and Physical Security Professional (PSP) credentials. For management roles, the ASIS Associate Protection Professional (APP) can help early-career candidates, while CISM is useful when the job includes security governance and risk oversight.
In 2027, certifications like Certified Information Systems Security Professional (CISSP) and Certified Protection Professional (CPP) are highly recognized for security management professionals, enhancing job prospects and credibility in the field. These credentials are offered by the International Information System Security Certification Consortium and ASIS International, respectively.
- Security Management Specialists Income and Hiring - BigFuture Career Search https://bigfuture.collegeboard.org/careers/security-management-specialist/income-and-hiring
- First Steps into Security Management: Your Guide to a Successful Career in the Security Industry https://www.get-licensed.co.uk/get-daily/first-steps-into-security-management-your-guide-to-a-successful-career-in-the-security-industry/
- Your fast track to become an infosec manager https://cybersecurityguide.org/careers/information-security-manager/
- Career Pathways in Security - Security Institute https://www.security-institute.org/career-pathways-in-security/
- Security manager https://nationalcareers.service.gov.uk/job-profiles/security-manager
- 6 Factors When Considering a Career in Security – Paragon https://paragonsecurity.ca/6-factors-when-considering-a-career-in-security/
- Career Outlook and Job Vacancies for Security Managers https://www.recruiter.com/careers/security-managers/outlook/
- Soft Skills in the Context of Security - Taurus Security https://securitybytaurus.com/soft-skills-in-the-context-of-security/
- Field of degree: Security and protective service https://www.bls.gov/ooh/field-of-degree/security-and-protective-service/security-and-protective-service-field-of-degree.htm