2027 How to Become a Security Auditor: Education, Salary, and Job Outlook

Co-Founder and Chief Data Scientist
Becoming a security auditor means choosing a career focused on finding security weaknesses before they become business, legal, or operational problems. Security auditors review systems, policies, controls, vendor practices, and technical evidence to determine whether an organization is protecting data properly and meeting required standards.
This guide is for students, early-career IT professionals, cybersecurity workers, and career changers who want a practical view of the role. You will learn what credentials employers typically expect, which skills matter most, how the career path develops, what salary ranges look like, where security auditors work, and how to decide whether this profession fits your strengths and long-term goals.
What are the benefits of becoming a security auditor?
- Security auditors enjoy a solid job outlook, with employment expected to grow 10% by 2025, driven by rising cybersecurity concerns across industries.
- The average salary for security auditors is around $75,000 to $95,000 per year, offering competitive pay for entry-level and experienced professionals.
- Choosing this career means joining a high-demand field, with opportunities for advancement and the chance to help protect vital information systems.
What credentials do you need to become a security auditor?
Most security auditor roles require a mix of formal education, hands-on technical experience, and recognized certifications. A bachelor's degree is often the baseline credential, but employers rarely hire auditors on education alone. They want proof that you understand systems, security controls, risk, documentation, and compliance requirements in real environments.
Core credentials employers look for
- Bachelor's Degree: Employers commonly prefer a degree in computer science, cybersecurity, information systems, or a closely related technical field. Relevant coursework may include network security, cryptography, operating systems, database security, risk management, and penetration testing.
- Work Experience: Many auditors build experience first as security analysts, network administrators, systems administrators, compliance analysts, or penetration testers. This background helps you understand how controls work in practice, not just how they appear in policy documents.
- Certified Information Systems Auditor (CISA): CISA is widely treated as a leading audit credential. It requires five years of professional auditing experience and a passing exam. You have five years after passing to apply for certification.
- Other Certifications: Credentials such as Certified Information Systems Security Professional (CISSP), CompTIA Security+, and Certified Internal Auditor can strengthen your profile, especially when they match the type of role you want.
- Continuing Education: Many certifications require ongoing professional learning. Some require up to 120 hours every three years to maintain active status.
How to choose the right education path
If you are starting from scratch, prioritize a cybersecurity or information systems program that includes networking, auditing, cloud security, scripting, and compliance. If you already work in IT, a certification-first path may help you move into audit work faster. If you want leadership, consulting, or specialized audit roles, graduate study can help, especially when paired with professional experience.
Requirements generally do not vary much by state, but they can vary by industry. Financial services, healthcare, government, and technology employers may emphasize different frameworks, evidence standards, and risk priorities. If you are comparing graduate options, 1 year online masters programs can be worth reviewing if you want a faster academic route while continuing to work.
What skills do you need to have as a security auditor?
A strong security auditor combines technical depth with judgment. The job is not only about finding vulnerabilities; it is about deciding which weaknesses matter, documenting evidence clearly, and helping an organization reduce risk without disrupting essential operations.
Technical skills
- Network and application security: You need to understand how systems communicate, where common weaknesses appear, and how attackers might exploit misconfigurations, insecure code, weak authentication, or exposed services.
- Compliance standards: Security auditors often work with SOC 2, PCI DSS, ISO 27001, and NIST. You do not need to memorize every clause immediately, but you must know how to interpret control requirements and gather evidence.
- Audit tools: Vulnerability scanners, configuration review tools, penetration testing software, ticketing systems, and governance platforms are common parts of the workflow.
- Incident response and log analysis: Auditors frequently review logs, access records, incident histories, and response processes to determine whether controls are working as designed.
- Cloud security: Familiarity with AWS, Azure, and Google Cloud is increasingly important because many organizations run critical workloads in cloud or hybrid environments.
- Programming basics: Python or Java knowledge can help you review scripts, understand application behavior, automate evidence collection, and communicate more effectively with engineering teams.
Risk, communication, and business skills
- Risk assessment: The best auditors do not treat every finding as equal. They assess likelihood, impact, compensating controls, and business context.
- Analytical thinking: You must connect technical findings to patterns, root causes, and control failures.
- Clear communication: Audit reports must be understandable to both technical teams and nontechnical decision-makers.
- Teamwork: Security auditors work with IT, legal, compliance, finance, operations, vendors, and executives. Cooperation matters because audit work often requires evidence from many teams.
One common mistake is focusing only on tools. Tools can identify issues, but auditors must validate findings, explain consequences, and recommend realistic remediation steps. That judgment is what separates a checklist reviewer from a trusted security professional.
What is the typical career progression for a security auditor?
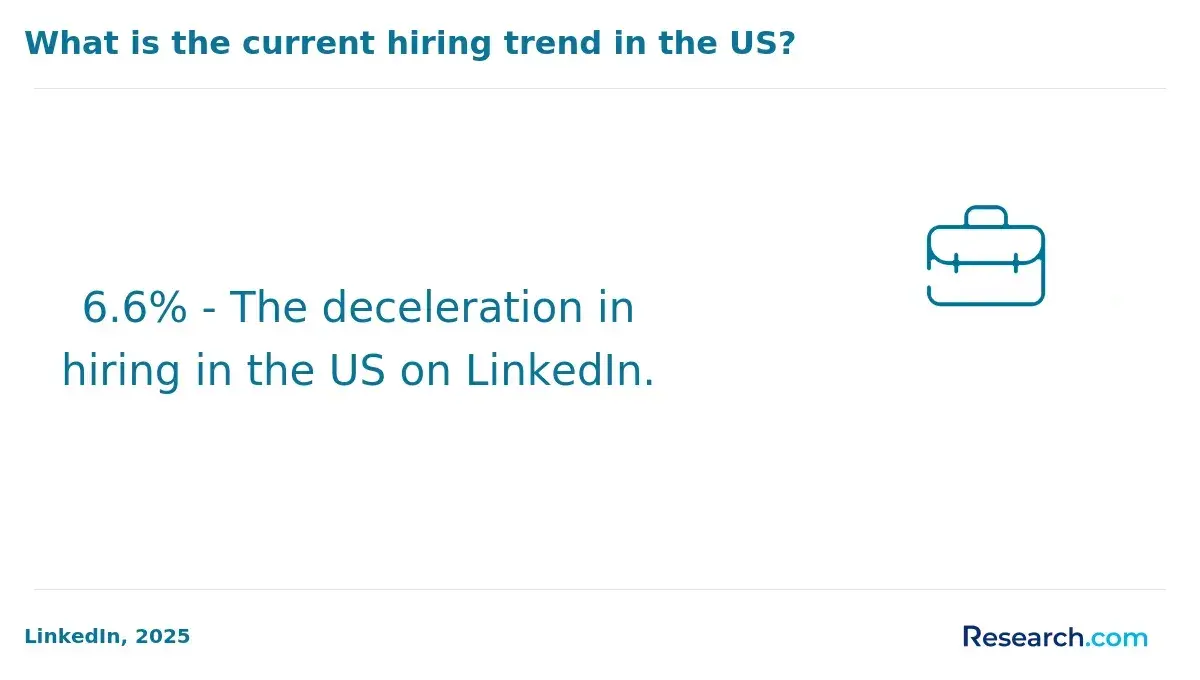
Security auditing usually begins with technical or compliance support work and progresses toward audit leadership, risk strategy, or executive security roles. The pace depends on your experience, certifications, industry, and ability to communicate risk to business leaders.
Entry-level roles
Early roles may include Junior Security Auditor, IT Auditor, or Application Security Analyst. At this stage, you may assist with audit planning, collect evidence, run vulnerability scans, review access controls, document findings, and learn frameworks such as OWASP Top 10 and NIST. Entry-level certifications such as CompTIA Security+ or Certified Ethical Hacker can help demonstrate readiness.
Mid-level roles
After gaining experience and earning credentials such as CISA or CISSP, many professionals move into positions such as Senior Security Auditor or IT Audit Lead. These roles involve leading audit activities, developing testing plans, reviewing remediation evidence, coordinating with stakeholders, and presenting risk findings to management. This move often happens after about 3-5 years of solid performance.
Advanced roles
Experienced auditors may advance into IT Audit Manager, Director of IT Audit, or Chief Information Security Officer (CISO) roles. At this level, the work shifts from individual audits to strategy, staffing, budgets, governance, and alignment between security priorities and organizational goals. Some professionals also specialize in cloud security, forensic investigations, risk management, compliance, or cybersecurity consulting.
- Entry-Level: Junior Security Auditor, IT Auditor, Application Security Analyst — assisting audits, scanning code, learning industry standards, and building practical security judgment.
- Mid-Level: Senior Security Auditor, IT Audit Lead — overseeing audits, managing smaller teams, developing plans, validating findings, and advising leadership on risk.
- Advanced: IT Audit Manager, Director of IT Audit, Chief Information Security Officer (CISO) — leading strategy, managing budgets, setting priorities, and connecting security work to business objectives.
Security auditor pay varies widely because the title can cover entry-level audit support, senior technical auditing, compliance leadership, consulting, and specialized cybersecurity audit work. Experience, certifications, industry, location, and the complexity of the systems you audit all affect compensation.
In the United States, salaries typically range from around $59,013 to over $98,295 annually, depending on your experience and the specific role. On average, most Information Security Auditors earn between $71,610 and $78,163. Highly experienced auditors, specialists, and professionals in senior or consulting roles may earn more.
Certifications can make a meaningful difference. For example, certifications like CISA can boost your pay significantly, with certified auditors earning $120,000 to over $129,000. That does not mean every certified professional will immediately reach that level, but it shows why employers value audit-specific credentials when hiring for higher-responsibility roles.
Factors that influence earning potential
- Experience level: Auditors who can lead engagements, interpret evidence, and advise leadership generally command higher pay than those who only support testing tasks.
- Certifications: CISA, CISSP, CompTIA Security+, and related credentials can help validate expertise and improve competitiveness.
- Industry: Finance, technology, consulting, healthcare, and government contractors may value different combinations of audit, risk, and technical knowledge.
- Specialization: Cybersecurity auditing, cloud audits, application security, and regulatory compliance can increase earning potential when demand is strong.
- Education: Advanced degrees can support movement into leadership, consulting, or specialized positions when paired with relevant experience.
If you are considering graduate education as part of your long-term plan, reviewing what is the easiest masters degree to get may help you compare workload, program fit, and career value. Choose a program based on relevance and credibility, not just speed or convenience.
Internships are one of the best ways to test whether security auditing fits you. They also help you build evidence-based experience before applying for full-time audit or cybersecurity roles. Look for internships that involve risk assessment, control testing, documentation, vulnerability management, compliance, or security operations.
Internship settings to consider
- Corporate Settings: Companies like Cloudflare offer internships where students may assist with IT and cybersecurity audits, including planning, fieldwork, evidence review, and reporting. These internships can build practical exposure to operational auditing and risk management.
- Government and Non-Profit Agencies: These internships may focus on cybersecurity compliance, policy development, incident response, and public-sector security requirements. They can be a good fit if you are interested in mission-driven or regulated environments.
- Healthcare and Education: Interns may work with sensitive records and learn how organizations address regulations such as HIPAA and FERPA. This experience is valuable because auditors in these sectors must understand both privacy obligations and technical safeguards.
- Industry-Specific Organizations: Firms like Dewberry offer cybersecurity internships where students may help maintain security systems, support risk mitigation procedures, and gain exposure to security tools and technical documentation.
What to look for in a strong internship
- Opportunities to review real policies, access records, logs, or control evidence.
- Exposure to frameworks such as SOC 2, ISO 27001, NIST, PCI DSS, HIPAA, or FERPA.
- Mentorship from security, audit, compliance, or risk professionals.
- A chance to produce audit documentation or remediation recommendations.
- Hands-on work with vulnerability scanners, ticketing systems, cloud tools, or governance platforms.
Advanced research-focused education is not required for most entry-level security auditor roles, but some professionals pursue doctoral study for academic, policy, or senior research paths. If that direction interests you, low cost PhD programs may help you compare options before committing to a long-term program.
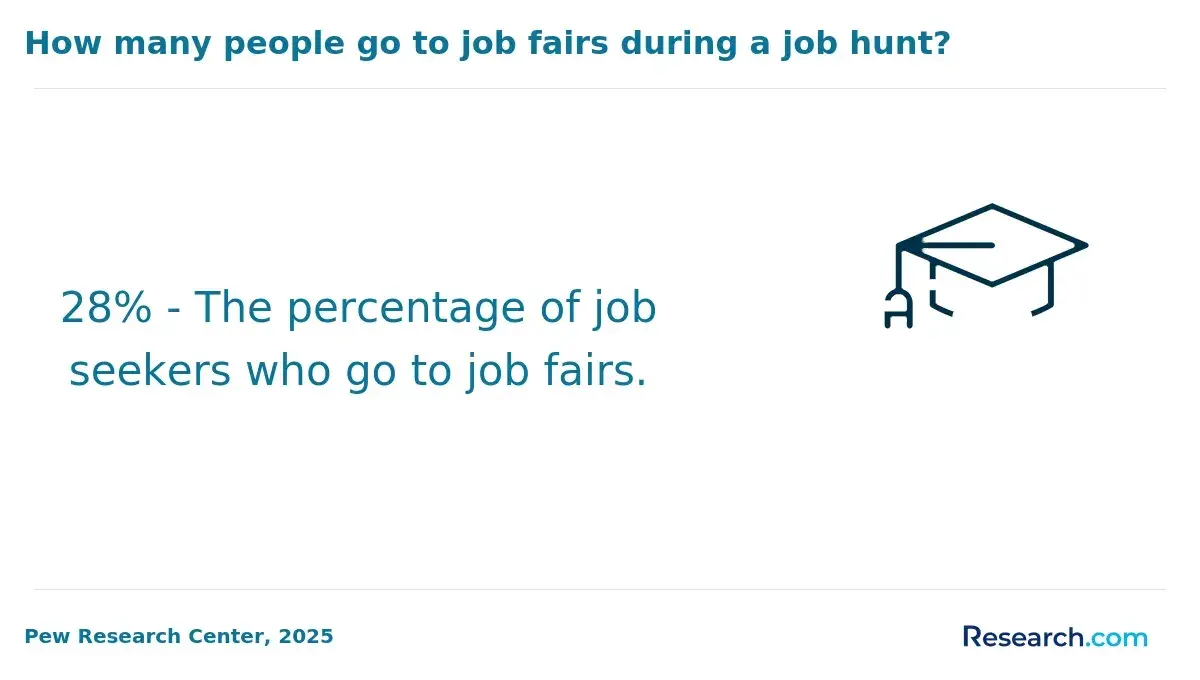
Career advancement in security auditing comes from expanding your technical range, earning trusted credentials, building business judgment, and proving that your work helps organizations reduce risk. Years of experience matter, but progression usually depends on the complexity of audits you can lead and the confidence stakeholders have in your recommendations.
Practical ways to move forward
- Earn targeted certifications: Credentials such as CISA, CSSLP, or CISSP can improve credibility and help qualify you for senior audit, consulting, or leadership roles. Choose certifications that match your intended path rather than collecting credentials without a plan.
- Continue your education: A bachelor's degree is often the minimum requirement, while a master's in cybersecurity or a related field may support advancement into leadership, specialized technical auditing, consulting, or government roles.
- Build a professional network: Organizations such as ISACA or (ISC)² can provide training, events, mentorship, and access to professionals who understand hiring needs in audit and security.
- Master advanced tools: Experience with code analysis software, cloud security frameworks, governance platforms, and data analytics tools can make your audit work more efficient and defensible.
- Develop leadership habits early: Volunteer to write sections of reports, present findings, coordinate evidence requests, or mentor junior staff. These tasks prepare you for lead auditor and manager roles.
- Learn the business side: Senior auditors must understand risk appetite, budgets, operational constraints, vendor relationships, and regulatory exposure. Technical findings carry more weight when you can explain their business impact.
A strong advancement strategy is specific. For example, an auditor aiming for cloud security should build cloud platform knowledge and related controls expertise. Someone aiming for IT audit management should develop reporting, stakeholder management, and team leadership skills.
Security auditors work wherever organizations need to protect systems, prove compliance, or manage cyber risk. Opportunities exist across private companies, public agencies, consulting firms, and regulated industries. The right setting depends on whether you prefer technical depth, regulatory work, client variety, or long-term internal governance.
- Financial institutions: Banks and other financial organizations need auditors to protect financial data, review controls, and support banking regulatory requirements. Many roles are concentrated in major business centers such as New York.
- Technology companies: Startups and large technology firms hire auditors to identify weaknesses, protect user data, evaluate engineering controls, and maintain customer trust.
- Consulting firms: Consulting roles place auditors across many client organizations. These jobs can offer broad exposure and, in major markets, salaries ranging from $100,000 to $200,000 annually.
- Government agencies: Public-sector roles may involve CJIS security, compliance reviews, policy enforcement, and protection of sensitive government systems. These positions may also offer stable employment and strong benefits.
- Healthcare systems, educational institutions, and insurance companies: These employers need auditors who can protect sensitive information and support regulatory compliance. Hybrid or remote roles may be available, especially in technology-forward organizations.
Demand remains robust, with hundreds of openings particularly in California and New York. If you are preparing for this career, it is worth comparing education options carefully, including FAFSA approved online colleges if financial aid eligibility is part of your decision.
Security auditing can be rewarding, but it is not a low-pressure compliance checklist job. Auditors often work with incomplete information, tight deadlines, evolving threats, and stakeholders who may resist findings. Knowing the challenges in advance can help you prepare.
- Rapidly changing cyber threats: Attack methods continue to evolve, including AI-driven malware and zero-day attacks. Auditors must keep learning so their assessments reflect current risks rather than outdated assumptions.
- Complex work environments: Modern organizations use cloud platforms, remote work systems, third-party vendors, legacy infrastructure, and interconnected applications. This complexity makes it harder to confirm whether controls are complete and effective.
- Increasing regulatory demands: New rules coming in 2025, especially from groups like the Institute of Internal Auditors, will push auditors to examine risks such as ransomware, supply chain issues, and insider threats more closely.
- Heavy workloads with limited resources: Smaller organizations may expect auditors to cover broad responsibilities with small teams and tight budgets. Prioritization becomes essential.
- Competitive job market and technical expectations: Employers increasingly value auditors who understand data analytics and AI tools. Candidates who combine audit discipline with technical fluency are more likely to stand out.
- Stakeholder pushback: Teams may disagree with findings, delay evidence, or underestimate risk. Auditors need diplomacy, documentation, and confidence to handle these situations professionally.
The challenge is part of the appeal for many professionals. If you enjoy structured investigation, complex systems, and work that requires both evidence and judgment, security auditing can stay intellectually engaging over the long term.
To excel as a security auditor, build credibility in three areas: technical competence, audit discipline, and communication. Employers and clients need to trust that your findings are accurate, your evidence is sound, and your recommendations are practical.
- Master the fundamentals of network and application security before trying to specialize.
- Learn major compliance frameworks such as ISO 27001 and SOC 2, and understand how control requirements translate into evidence.
- Practice with audit tools, vulnerability scanners, log review platforms, and ticketing systems so you can work efficiently during assessments.
- Do not just identify security gaps; explain how each issue affects operations, legal exposure, customer trust, or business continuity.
- Write clearly. A useful audit report should help leaders understand risk and help technical teams fix the problem.
- Translate findings into prioritized, realistic recommendations instead of overwhelming teams with vague or impractical advice.
- Earn respected credentials such as CISA, CISSP, or CompTIA Security+ when they align with your target roles.
- Keep learning after certification through professional groups, conferences, webinars, and peer networks.
- Stay detail-focused, proactive, and curious. Small evidence gaps can change the outcome of an audit.
- Build professional judgment by asking: What is the risk, what evidence supports it, what control failed, and what remediation is reasonable?
Avoid the common mistake of sounding alarmist. Strong auditors are direct but measured. They distinguish between theoretical risk and urgent exposure, which makes their recommendations more credible.
Security auditing may be a good fit if you enjoy investigative work, technical systems, structured standards, and clear documentation. It is especially suitable for people who like finding weaknesses, asking precise questions, and helping organizations make better risk decisions.
- Curiosity and Problem-Solving: You should enjoy digging into systems, asking why controls exist, spotting patterns, and identifying how a failure could affect the organization.
- Attention to Detail: Audit work requires careful evidence review, organized documentation, and consistent follow-through. Missing small details can lead to incomplete or inaccurate conclusions.
- Communication Skills: You need to explain technical problems to leaders, employees, and business teams that may not have cybersecurity backgrounds.
- Ethics and Trustworthiness: Security auditors handle sensitive information. Integrity, discretion, and sound judgment are essential.
- Work Environment: Expect a role that includes technical review, meetings, report writing, evidence collection, and deadline-driven projects. It can be stressful during audit cycles but may offer stability because organizations continue to need security expertise.
- Personal Fit: This career may suit you if you like standards, systems, teamwork, and independent analysis. It may be less appealing if you dislike documentation, stakeholder communication, or detailed review work.
Questions to ask yourself
- Do I enjoy both technology and policy?
- Can I explain technical risks without using unnecessary jargon?
- Am I comfortable challenging teams respectfully when evidence does not support a claim?
- Do I like structured work that still requires investigation and judgment?
- Am I willing to keep learning as threats, tools, and regulations change?
If you are unsure, try an introductory cybersecurity course, a compliance project, a help desk or systems role, or an internship before committing fully. You can also compare related technology pathways, including these top vocational degree careers, if you are exploring alternative education routes into technical work.
What Professionals Who Work as a Security Auditor Say About Their Careers
-
: "Pursuing a career as a security auditor has offered me unmatched job stability and a competitive salary that continues to grow with demand in cybersecurity. The constant evolution of threats means my skills remain crucial, giving me confidence in long-term prospects. I appreciate how the role blends technical expertise with strategic insight, making every project rewarding.
— Ryatt
"
-
: "What I find most challenging-and rewarding-in security auditing is staying ahead of the latest regulatory changes and cyber threats. It requires continuous learning and adaptability, which keeps the work engaging. The profession opens doors to diverse industries, providing unique opportunities to broaden one's perspective and impact.
— Harry
"
-
: "Working as a security auditor has been a significant catalyst for my professional development. The structured training programs and industry certifications available have accelerated my career growth and deepened my expertise in risk management. I value the collaborative environment where knowledge sharing is encouraged and leadership roles are attainable.
— Cyrus
"
Other Things You Should Know About Becoming a Security Auditor
Certifications like Certified Information Systems Auditor (CISA), Certified Information Systems Security Professional (CISSP), and Certified Ethical Hacker (CEH) are beneficial for security auditors in 2027 as they demonstrate expertise and commitment to the field, improving job prospects and salary potential.
While not all security auditors are IT experts, a solid understanding of information technology is crucial. Many auditors have backgrounds in IT, cybersecurity, or computer science, which helps them identify vulnerabilities effectively. Hands-on IT experience allows security auditors to better communicate with technical teams and interpret complex security issues.
Ethical hacking is a crucial part of a security auditor's role. It involves probing systems to identify vulnerabilities that could be exploited by malicious hackers, ensuring robust security measures are in place. Certification programs like CEH (Certified Ethical Hacker) are beneficial for honing these skills.
Aspiring security auditors typically need a bachelor's degree in cybersecurity, information technology, or a related field. Degrees should be complemented by internships and coursework relevant to risk assessment and network security to meet the job's evolving demands by 2027.
- How to Become a Security Auditor | Education and Experience https://www.cyberdegrees.org/careers/security-auditor/how-to-become/
- Pathways Internship Program https://www.dcaa.mil/Careers/Specialized-Hiring/Pathways-Internship-Program/
- Bank Auditors’ Focus on Cyber Security – How to Excel in a Critical Area - ThreatReady Resources https://www.getthreatready.com/bank-auditors-focus-cyber-security-excel-critical-area/
- Cyber and IT Interns | CISA https://www.cisa.gov/careers/work-rolescyber-and-it-interns
- Challenges in Cyber Security Auditing - Huntsman https://huntsmansecurity.com/blog/challenges-in-cyber-security-auditing/
- Security Audit - A Complete Guide to Cyber Safety https://www.fortinet.com/resources/cyberglossary/security-audit
- 7 Critical Auditing Skills to Enhance Your Audit Career Path | Workiva https://www.workiva.com/sg/blog/7-critical-skills-enhance-your-audit-career-path
- 2023 Volume 6 Future Skills Needed in Audit Cybersecurity Privacy and Emerging Technology https://www.isaca.org/resources/isaca-journal/issues/2023/volume-6/future-skills-needed-in-audit-cybersecurity-privacy-and-emerging-technology
- How to Become a Security Code Auditor https://cybersecurityguide.org/careers/security-code-auditor/
- How to excel in a career in cyber security - IT Governance Blog https://www.itgovernance.co.uk/blog/how-to-excel-in-a-career-in-cyber-security