2027 Governance, Risk, and Compliance Careers: Skills, Education, Salary & Job Outlook

Co-Founder and Chief Data Scientist
A career in governance, risk, and compliance is for people who want to help organizations make safer, more ethical, and better-controlled decisions. GRC professionals sit at the intersection of business operations, law, finance, cybersecurity, audit, and corporate strategy. Their work matters because organizations face tighter regulatory scrutiny, more complex technology risks, and higher expectations from customers, investors, employees, and regulators.
The path can be attractive, but it is not a casual career choice. You need a strong foundation in risk management, internal controls, regulatory requirements, communication, and business judgment. Frameworks and laws such as SOX and GDPR often shape the work, and technology-driven compliance is becoming more important across industries.
This guide explains what Governance, Risk, and Compliance Officers do, the skills and credentials employers commonly value, how to enter the field, what salaries and job growth look like, and how to decide whether this career fits your strengths. The field shows steady job growth of 3%, while median salaries for GRC officers and managers can range between $105,846 and $153,223, with some professionals exceeding $200,000 depending on role, industry, location, and experience.
Key Things You Should Know About Governance, Risk, and Compliance Career
- The typical earning potential for governance, risk, and compliance professionals ranges from around $105,846 annually for entry-level roles to $153,223 for managers, with specialized positions reaching up to $209,000 based on experience and industry.
- This field offers stable and steady growth, with employment for compliance officers expected to increase by about 3% over the next decade, keeping pace with the average growth for all occupations.
- A bachelor's degree in business, finance, accounting, law, or a related field is generally required to start, and professional certifications like CRCM or CISA can enhance opportunities.
- Success depends on sharp analytical thinking, attention to detail, strong communication, deep knowledge of regulatory requirements, ethical judgment, and growing technical skills in data analysis and GRC software.
- Career paths typically begin at compliance analyst or officer levels, advancing to risk or compliance manager roles, then progressing to leadership positions such as director of compliance or chief risk officer, with increased strategic responsibility.
What do Governance, Risk, and Compliance Officers do?
Governance, Risk, and Compliance Officers help organizations operate responsibly while reducing legal, financial, operational, cybersecurity, and reputational risk. They translate laws, standards, policies, and risk frameworks into practical controls that employees and leaders can follow. Their goal is not simply to “check boxes.” A strong GRC function helps the organization make better decisions before problems become audits, fines, breaches, lawsuits, or public trust failures.
In practice, GRC professionals evaluate how an organization is governed, where risks are most likely to appear, and whether the company is meeting internal and external requirements. They may work with executives, legal teams, IT departments, finance leaders, auditors, vendors, and frontline employees. The role requires both technical understanding and influence because compliance only works when people across the organization understand and follow the process.
A day in the life of Governance, Risk, and Compliance Officers
A typical day may include reviewing risk reports, updating policy language, preparing audit evidence, meeting with business units, investigating control gaps, or explaining regulatory changes to leadership. During stable periods, the work is structured and analytical. During audits, incidents, new regulations, system implementations, or vendor reviews, the pace can become more urgent.
Many GRC officers spend significant time documenting decisions, testing controls, tracking remediation plans, and communicating findings in plain language. The best professionals are not only detail-oriented; they can show why a risk matters, what the business impact could be, and which response is realistic.
What are the key responsibilities of Governance, Risk, and Compliance Officers?
Governance, Risk, and Compliance Officers are responsible for building and maintaining the systems that help an organization follow rules, manage uncertainty, and act ethically. Their duties vary by industry, but most roles include a mix of policy work, risk analysis, monitoring, reporting, training, and incident response.
- Develop, review, and enforce internal policies that support legal, regulatory, contractual, and ethical requirements.
- Conduct risk assessments to identify threats, estimate their potential impact, and recommend practical mitigation steps.
- Monitor controls, test compliance procedures, and document whether business units are following required standards.
- Prepare reports for managers, executives, boards, auditors, or regulators using clear evidence and defensible conclusions.
- Train employees on compliance expectations, policy updates, reporting obligations, and risk-aware behavior.
- Investigate suspected noncompliance, control failures, process gaps, or misconduct and help design corrective action plans.
- Coordinate with legal, audit, IT, finance, human resources, procurement, and operations teams to close risk and compliance gaps.
The most challenging vs. the most rewarding tasks
The hardest part of the job is often managing change. Regulations evolve, business models shift, systems are replaced, and risks can emerge faster than policies are updated. GRC officers must often persuade busy teams to change how they work, even when those teams see compliance as an obstacle.
The most rewarding part is seeing risk management become part of the organization’s culture. When employees report issues early, leaders ask better risk questions, and audits produce fewer surprises, the GRC function is working. For early-career learners who need a fast academic starting point, exploring associate degrees in 6 months online can help identify short programs that build business, accounting, technology, or legal foundations.
What are the key skills for Governance, Risk, and Compliance Officers?
GRC careers require a combination of technical knowledge, structured thinking, and stakeholder management. Employers look for professionals who can interpret requirements, identify weak controls, explain risk clearly, and help the business fix issues without creating unnecessary complexity.
Key hard skills for GRC Officers
- Regulatory and compliance analysis: Ability to interpret laws, standards, policies, and contractual obligations and convert them into workable procedures.
- Risk assessment and mitigation: Skill in identifying risks, estimating likelihood and impact, ranking priorities, and recommending controls.
- Audit and monitoring: Understanding how to test controls, gather evidence, document findings, and track remediation.
- GRC software proficiency: Familiarity with tools such as RSA Archer or MetricStream for risk registers, workflows, control testing, and reporting.
- Data and reporting skills: Ability to summarize trends, exceptions, incidents, and control performance for nontechnical audiences.
- Cybersecurity and privacy awareness: Increasingly important for roles involving technology controls, vendor risk, data protection, and incident response.
Crucial soft skills for GRC Officers
- Analytical thinking: Breaking down complex information and identifying what is relevant, material, and actionable.
- Critical thinking: Challenging assumptions, spotting control weaknesses, and weighing trade-offs before recommending action.
- Communication: Explaining requirements, risks, and findings clearly to executives, auditors, technical teams, and frontline staff.
- Integrity: Maintaining ethical judgment, confidentiality, and independence even when findings are uncomfortable.
- Influence: Earning cooperation from teams that may not report directly to the GRC function.
- Project discipline: Tracking deadlines, evidence, owners, corrective actions, and repeat findings across multiple departments.
The one overlooked skill that separates the good from the great
Cultural competence and global awareness are often underestimated. Many organizations operate across jurisdictions, serve international customers, or rely on global vendors. A GRC professional who understands how regulatory expectations, business customs, privacy norms, and communication styles differ across regions can prevent avoidable misunderstandings and compliance failures.
For example, a compliance officer supporting a multinational product launch may need to consider privacy rules, vendor obligations, local documentation expectations, and escalation norms at the same time. The professional who asks the right cultural and jurisdictional questions early can save the organization from delays, rework, and reputational damage.
Professionals who combine these skills with targeted credentials can compete for roles in higher-paying fields, including securities and commodity investments. If you are comparing short training options, reviewing quick certifications that pay well can help you evaluate credentials that may strengthen a GRC resume.
Starting a GRC career is easier when you treat it as a staged plan: build relevant education, get close to risk or compliance work, add credentials, then specialize. You do not need to begin in a job with “GRC” in the title. Many professionals enter through internal audit, compliance operations, finance controls, IT security, privacy, legal support, or risk analyst roles.
- Build a relevant education base. Choose coursework in business, accounting, finance, information technology, cybersecurity, law, data analysis, or public administration. Focus on classes that teach controls, regulation, documentation, ethics, and decision-making.
- Gain practical exposure early. Look for internships, entry-level compliance roles, risk analyst roles, audit support positions, security analyst roles, or operations jobs involving policies and controls.
- Learn common frameworks and regulations. Depending on your target field, become familiar with internal controls, privacy, cybersecurity, financial services rules, healthcare compliance, vendor risk, or enterprise risk management.
- Document your impact. Track examples of risk assessments, audit evidence, process improvements, policy updates, training materials, or remediation projects. Employers value proof that you can apply concepts.
- Add professional credentialing when it fits your direction. Certifications are most useful when they match the role you want, such as compliance, audit, cybersecurity governance, or financial regulation.
- Move into broader ownership. In mid-level roles, seek responsibility for control testing, issue management, policy governance, audit coordination, vendor assessments, or regulatory reporting.
- Specialize or lead. Senior professionals often focus on areas such as cybersecurity risk, privacy, internal audit, enterprise risk, third-party risk, or regulatory compliance leadership.
The strongest GRC candidates show progression: they understand the rules, can evaluate risk, communicate findings, and help the organization fix problems. Each step should build evidence that you can protect the business while supporting practical operations.
Most Governance, Risk, and Compliance roles begin with a bachelor's degree. Common degree paths include Bachelor of Business Administration (BBA), Bachelor of Science in Finance, Accounting, Information Technology, or Law (LLB). These programs can prepare students for GRC work when they include subjects such as risk management, corporate governance, auditing, ethics, cybersecurity, business law, and regulatory compliance.
Employers also value hands-on experience. Entry-level roles in compliance, risk management, internal audit, finance controls, cybersecurity operations, or policy administration can provide the real-world training needed to understand how organizations document, test, and improve controls.
Common certifications for GRC professionals
Certifications can strengthen a resume, but they should be chosen carefully. The best credential depends on whether you want to work in corporate compliance, cybersecurity governance, banking regulation, internal audit, privacy, or enterprise risk.
- Certified in Governance, Risk and Compliance (CGRC) by ISC2: Useful for professionals focused on security governance, risk frameworks, and compliance in technology environments.
- Certified Compliance & Ethics Professional (CCEP) by the Compliance Certification Board: Relevant for corporate compliance and ethics programs.
- Certified Regulatory Compliance Manager (CRCM): A specialized option for professionals focused on regulatory compliance management.
- Certified Internal Auditor (CIA): Valuable for professionals who want to deepen audit, assurance, and controls expertise.
Are advanced degrees or niche certifications worth the investment?
Advanced degrees can be worthwhile for professionals targeting leadership, specialized risk roles, or technical governance positions. A Master of Business Administration with a focus on Risk Management may support advancement into management or strategy roles. A Master of Science in Information Security may be a better fit for professionals focused on cybersecurity risk, security governance, or technology compliance.
However, a master's degree is not required for every GRC role. Many professionals advance through a combination of experience, strong documentation skills, industry knowledge, and targeted certifications. Before investing, compare the cost, time commitment, employer expectations, and your target job postings. If the roles you want consistently prefer a specific credential, the investment may be easier to justify.
If you are still choosing an undergraduate path, reviewing what bachelor degrees make the most money can help you compare academic options with long-term career value.
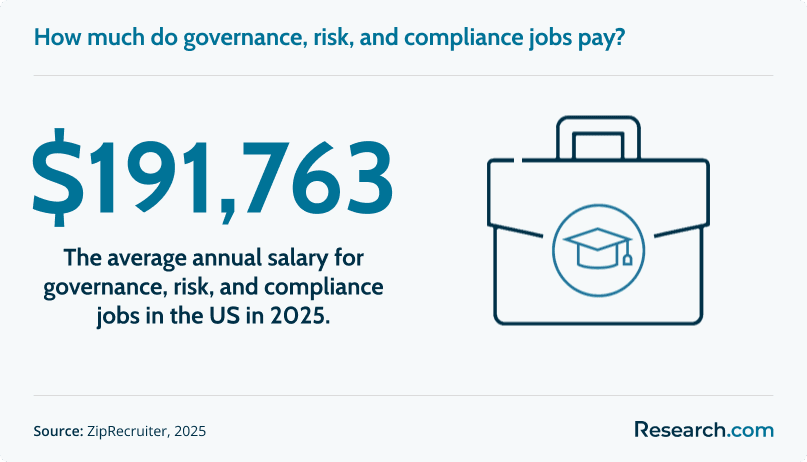
The governance risk and compliance salary range 2025 in the United States centers around a median annual salary of $95,103. Entry-level professionals can expect to start near $70,000, while senior-level experts can earn as much as $143,500. Compensation can rise further for leaders, specialized technology risk professionals, and executives in highly regulated or high-stakes industries.
Salary varies widely because “GRC” covers many job types. A compliance associate, IT risk analyst, internal audit manager, privacy officer, and chief risk executive may all work in the same broad field but command different pay. Factors that influence earnings include industry, location, employer size, regulatory complexity, technical specialization, certifications, and management responsibility.
What tends to increase earning potential?
- Specialization: Cybersecurity risk, financial regulation, privacy, third-party risk, and audit leadership can command stronger compensation when demand is high.
- Certifications: Relevant credentials can support advancement when paired with practical experience.
- Industry exposure: Heavily regulated sectors often place a higher value on experienced GRC talent.
- Leadership scope: Managing teams, owning enterprise programs, or reporting to executives can move professionals into higher salary bands.
- Business impact: Professionals who can reduce audit findings, improve controls, and prevent costly failures become more valuable over time.
When evaluating salary data, compare roles with similar scope. A job title alone can be misleading; review whether the position owns policy, testing, remediation, reporting, technology controls, people management, or enterprise strategy.
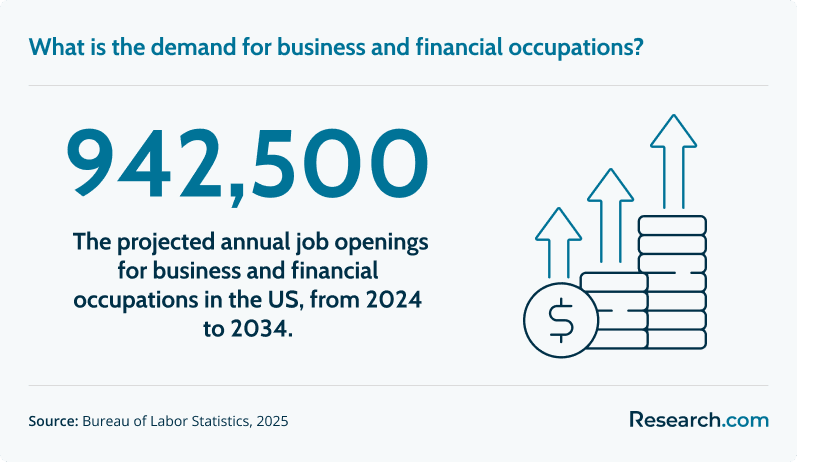
Employment for compliance officers is projected to grow 3 percent from 2024 to 2034, which is about as fast as the average for all occupations. That outlook suggests steady rather than explosive growth. However, demand remains durable because organizations must continue meeting regulatory, audit, privacy, security, and governance obligations regardless of economic cycles.
The key factors shaping the future outlook
Regulatory complexity is one of the strongest drivers of GRC demand. Organizations must update policies, controls, training, reporting, and documentation as rules change. This is especially important in industries such as finance, healthcare, technology, government contracting, insurance, and data-intensive services.
Cybersecurity and digitization are also reshaping the field. As organizations move more operations into cloud platforms, data systems, third-party tools, and automated workflows, GRC professionals increasingly need to understand technology risk. This does not mean every GRC officer must become a software engineer, but it does mean technical fluency is becoming more valuable.
AI and automation may reduce some repetitive compliance tasks, such as evidence collection, workflow reminders, and routine monitoring. At the same time, these tools create new governance questions around accuracy, bias, privacy, accountability, and oversight. Professionals who can evaluate both regulatory obligations and technology risk will be better positioned.
If you are comparing education paths that can lead to stable, practical careers, reviewing the fastest degrees that pay well may help you identify options beyond traditional long-format programs.
Most GRC professionals work full time during standard business hours, but the schedule can become more demanding around audits, regulatory deadlines, incidents, board reporting, system implementations, or major policy changes. The work is usually office-based, though hybrid and remote arrangements are increasingly common for roles centered on documentation, monitoring, reporting, and virtual collaboration.
The work environment depends heavily on industry. Employment data shows that 32% work in federal, state, and local government, 15% in finance and insurance, and 9% in healthcare and social assistance. Government roles may emphasize public accountability and statutory requirements. Finance and insurance roles often involve strict regulatory oversight, testing, and documentation. Healthcare roles may involve privacy, patient data, billing rules, and operational compliance.
GRC officers typically interact with many departments rather than working in isolation. A single week may involve meetings with legal counsel, IT security, finance, internal audit, procurement, operations, human resources, and executive leadership. The culture can be collaborative, but the role also requires comfort with difficult conversations because GRC professionals must sometimes challenge decisions, document weaknesses, or escalate unresolved risks.
Governance, Risk, and Compliance can be a strong career for people who like structure, analysis, ethical responsibility, and cross-functional problem-solving. It is less ideal for people who dislike documentation, ambiguity, policy detail, or having to push back on colleagues and leaders.
Pros
- Meaningful organizational impact: Your work can prevent fines, breaches, fraud, operational failures, and reputational damage.
- Strong visibility: GRC professionals often brief managers, executives, auditors, and boards on important risks.
- Transferable skills: Risk assessment, audit readiness, policy development, and control testing apply across many industries.
- Continuous learning: Regulations, technologies, threats, and business models change, keeping the work intellectually active.
- Multiple specialization paths: You can move toward cybersecurity risk, privacy, internal audit, financial compliance, vendor risk, or enterprise risk management.
Cons
- Regulatory complexity: Requirements can be detailed, overlapping, and frequently updated.
- Pressure during audits and incidents: Deadlines can be tight, and documentation must be accurate.
- Resistance from business units: Some teams may view compliance requirements as slowing down their work.
- High accountability: Mistakes in risk analysis, reporting, or escalation can have serious consequences.
- Heavy documentation: The role often involves evidence, logs, policies, reports, and formal remediation tracking.
If you are weighing GRC against other practical career paths, exploring the highest paying jobs trade school careers can provide useful comparisons for cost, training time, work environment, and long-term earning potential.
GRC offers clear advancement paths because organizations need both specialists and leaders. Early-career professionals often start by supporting audits, collecting evidence, maintaining risk registers, or tracking compliance tasks. Over time, they may own programs, advise executives, manage teams, or lead enterprise-wide risk strategy.
Clear advancement ladder
- Entry-Level: Start as a GRC Analyst, Risk Analyst, Compliance Associate, audit assistant, or control testing analyst. The focus is usually data gathering, documentation, issue tracking, and audit support.
- Mid-Level: Move into roles such as Risk Specialist, Compliance Specialist, Internal Auditor, GRC Consultant, or IT Risk Analyst. At this stage, professionals lead assessments, manage findings, and advise business units.
- Senior-Level: Advance to GRC Manager, Compliance Manager, Risk Manager, Audit Manager, or program lead. These roles oversee projects, manage teams, coordinate audits, and report to leadership.
- Leadership-Level: Become Director or Head of GRC, leading strategy, policies, risk appetite discussions, governance frameworks, and cross-functional programs.
- Executive-Level: Progress to Chief Risk Officer, CISO, or Compliance Executive, where the focus shifts to enterprise-wide risk direction, board communication, regulatory posture, and strategic decision-making.
Specialization opportunities
- Cybersecurity Risk Management: Use frameworks such as NIST and ISO 27001 to evaluate security controls, technology risk, and resilience.
- Regulatory Compliance: Focus on requirements such as GDPR, HIPAA, PCI-DSS, and industry-specific rules.
- Audit and Assurance: Lead internal and external audit preparation, testing, evidence review, and remediation tracking.
- Third-Party and Vendor Risk Management: Assess supplier, contractor, cloud provider, and outsourcing risks before and during business relationships.
- Policy Development and Governance: Design governance frameworks that connect business goals, accountability, controls, and risk oversight.
Advancement usually depends on a mix of credibility, judgment, communication, and proof of results. Professionals who can translate complex requirements into practical action are often the ones who move from analyst roles into leadership.
If you are interested in GRC but not sure the officer path is the best fit, related careers can offer similar skills with different day-to-day responsibilities. Consider whether you prefer analysis, investigation, consulting, technology, process design, or leadership.
- Risk Analyst: Focuses on identifying, measuring, and monitoring business, financial, operational, or technology risks. This can be a strong entry point into broader GRC work.
- Compliance Consultant: Advises organizations on regulatory requirements, policy design, audit readiness, and remediation. This path may involve more client-facing work and travel depending on the employer.
- IT Auditor: Reviews technology controls, system access, security processes, and IT governance. This is a good fit for people who like both audit structure and technical environments.
- Anti-Money Laundering Specialist: Investigates suspicious financial activity, reviews transactions, and supports anti-fraud and financial crime compliance programs.
- Business Architect: Designs and aligns business processes, systems, and governance structures so operations support organizational goals and compliance expectations.
To choose among these paths, compare the daily work rather than the title. Ask whether you want to investigate exceptions, design controls, advise clients, test systems, monitor regulations, or lead enterprise programs. The closer the work is to your natural strengths, the more sustainable the career is likely to be.
- : "I'm drawn to this role because it allows me to apply my skills in strategic security risk and governance directly to current and emerging challenges. Each day brings new threats that require careful analysis and proactive measures to keep our organization safe. Knowing that my efforts help safeguard essential operations makes the responsibility meaningful beyond just procedure. It feels like I'm genuinely protecting the future of the services we provide, not just managing risks on paper. — Kiran"
- : "One of the hardest parts of my work is keeping up with the constantly shifting regulatory landscape while making sure security is integrated from the very beginning of every project. Balancing immediate compliance checks with the long-term strategic goals of governance keeps me on my toes. It demands a mix of technical insight and careful planning, but overcoming these challenges sharpens my expertise and commitment. Without that vigilance from day one, the organization's risk posture just wouldn't hold. — Talia"
- : "What keeps me motivated is the variety and collaboration this role requires-working with IT, legal, and operations teams to embed security as a natural part of our culture. No two days feel alike, and seeing a team become truly security-aware rather than just ticking boxes is incredibly rewarding. It's powerful to contribute to that shift, where cybersecurity influences decisions and behaviors organization-wide. Being part of that cultural change is what makes the effort worthwhile every single day. — Samuel"
Key Findings
- Governance, Risk, and Compliance Officers help organizations follow rules, manage uncertainty, protect data and reputation, and make better decisions.
- The field is best suited for professionals who are analytical, ethical, detail-oriented, and comfortable communicating with many departments.
- Most roles begin with a bachelor's degree in areas such as business, finance, accounting, information technology, or law, supported by practical experience and targeted certifications.
- The governance risk and compliance salary range 2025 centers around a median annual salary of $95,103, with entry-level professionals near $70,000 and senior-level experts earning as much as $143,500.
- Employment for compliance officers is projected to grow 3 percent from 2024 to 2034, making the outlook steady rather than unusually fast.
- Career advancement can lead from analyst and associate roles to manager, director, Chief Risk Officer, CISO, or Compliance Executive positions.
- Cybersecurity risk, privacy, third-party risk, audit, and regulatory compliance are among the strongest specialization areas for long-term growth.
Other Things You Should Know About Governance, Risk, and Compliance
U.S. GRC analysts typically earn about $75,000 to $120,000 a year in 2027, with senior analysts and managers often exceeding $130,000. Pay is highest in finance, healthcare, and technology, and salaries are usually higher in large metropolitan markets and regulated industries.
Certifications like Certified Compliance & Ethics Professional (CCEP) and Certified Risk Manager (CRM) are highly valuable in 2027. They demonstrate expertise and commitment to the field, often preferred by employers seeking skilled professionals to navigate complex regulatory environments.
- Thinking about a Career in Governance, Risk and Compliance? Follow this Path. https://www.isc2.org/Insights/2023/10/Thinking-About-a-Career-in-Governance-Risk-and-Compliance
- Compliance Officers: Occupational Outlook Handbook: U.S. Bureau of Labor Statistics https://www.bls.gov/ooh/business-and-financial/compliance-officers.htm
- Career Pathways in GRC https://www.planetcompliance.com/grc/career-pathways-in-grc/
- What Is a Governance and Compliance Specialist? https://www.spencerclarkegroup.co.uk/what-is-a-governance-and-compliance-specialist/
- Beyond technical expertise: the importance of soft skills in hiring Risk Management professionals https://www.apollo-solutions.com/resources/blog/beyond-technical-expertise--the-importance-of-soft-skills-in-hiring-risk-management-professionals/
- Why demand for compliance professionals is high, and what you should do about it | Barclay Simpson https://www.barclaysimpson.com/why-demand-for-compliance-professionals-is-high-and-what-you-should-do-about-it/
- Governance, risk and compliance (GRC): Definitions and resources https://www.diligent.com/resources/guides/grc
- Top 10 GRC Interview Questions and Answers - ThinkCloudly https://thinkcloudly.com/blog/it-auditing-and-grc-interview-questions/top-10-grc-interview-questions-and-answers/
- What is GRC (Governance, Risk and Compliance)? https://pathlock.com/blog/grc/
- How to get into GRC https://allaboutgrc.com/how-to-get-into-grc/